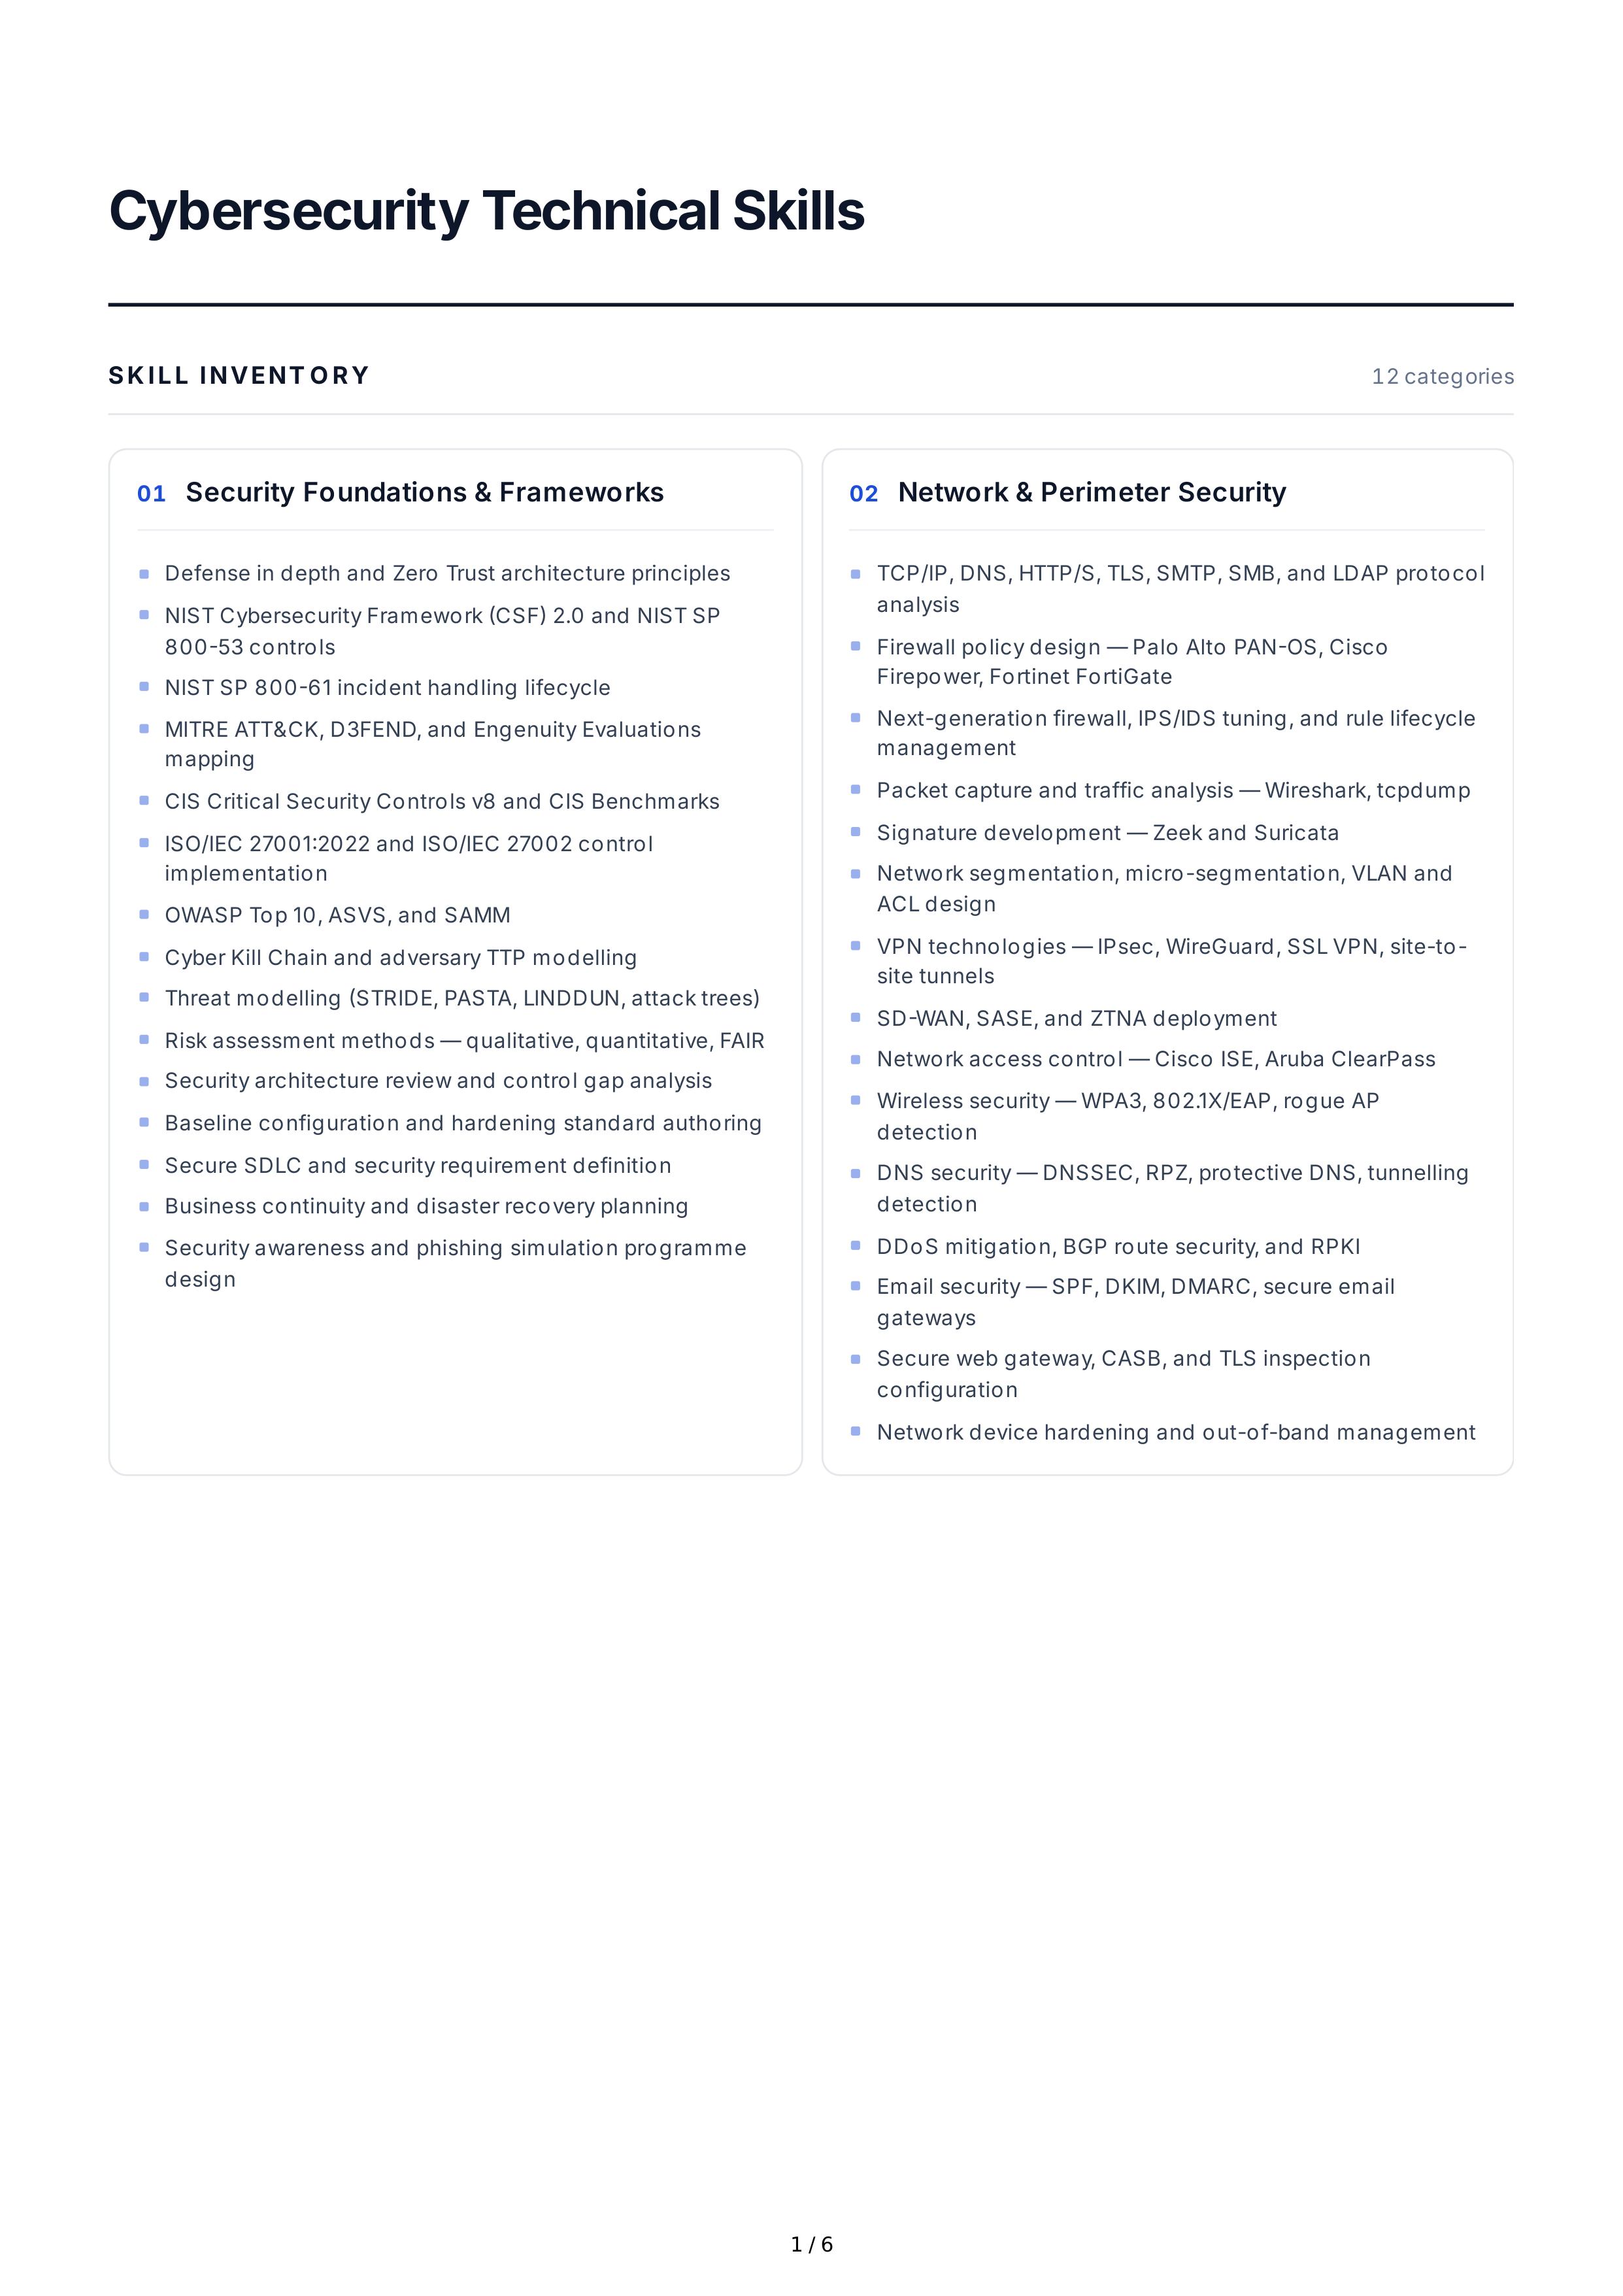
Cybersecurity
Technical
Skills
SK IL L
INVENT O RY
12
categories
01
Security
Foundations
&
Frameworks
02
Network
&
Perimeter
Security
Defense
in
depth
and
Zero
Trust
architecture
principles
NIST
Cybersecurity
Framework
(
CSF
) 2.0
and
NIST
SP
800-53
controls
NIST
SP
800-61
incident
handling
lifecycle
MITRE
ATT
&
CK
,
D
3
FEND
,
and
Engenuity
Evaluations
mapping
CIS
Critical
Security
Controls
v
8
and
CIS
Benchmarks
ISO
/
IEC
27001:2022
and
ISO
/
IEC
27002
control
implementation
OWASP
Top
10,
ASVS
,
and
SAMM
Cyber
Kill
Chain
and
adversary
TTP
modelling
Threat
modelling
(
STRIDE
,
PASTA
,
LINDDUN
,
attack
trees
)
Risk
assessment
methods
—
qualitative
,
quantitative
,
FAIR
Security
architecture
review
and
control
gap
analysis
Baseline
configuration
and
hardening
standard
authoring
Secure
SDLC
and
security
requirement
definition
Business
continuity
and
disaster
recovery
planning
Security
awareness
and
phishing
simulation
programme
design
TCP
/
IP
,
DNS
,
HTTP
/
S
,
TLS
,
SMTP
,
SMB
,
and
LDAP
protocol
analysis
Firewall
policy
design
—
Palo
Alto
PAN
-
OS
,
Cisco
Firepower
,
Fortinet
FortiGate
Next
-
generation
firewall
,
IPS
/
IDS
tuning
,
and
rule
lifecycle
management
Packet
capture
and
traffic
analysis
—
Wireshark
,
tcpdump
Signature
development
—
Zeek
and
Suricata
Network
segmentation
,
micro
-
segmentation
,
VLAN
and
ACL
design
VPN
technologies
—
IPsec
,
WireGuard
,
SSL
VPN
,
site
-
to
-
site
tunnels
SD
-
WAN
,
SASE
,
and
ZTNA
deployment
Network
access
control
—
Cisco
ISE
,
Aruba
ClearPass
Wireless
security
—
WPA
3, 802.1
X
/
EAP
,
rogue
AP
detection
DNS
security
—
DNSSEC
,
RPZ
,
protective
DNS
,
tunnelling
detection
DDoS
mitigation
,
BGP
route
security
,
and
RPKI
Email
security
—
SPF
,
DKIM
,
DMARC
,
secure
email
gateways
Secure
web
gateway
,
CASB
,
and
TLS
inspection
configuration
Network
device
hardening
and
out
-
of
-
band
management
1 / 6
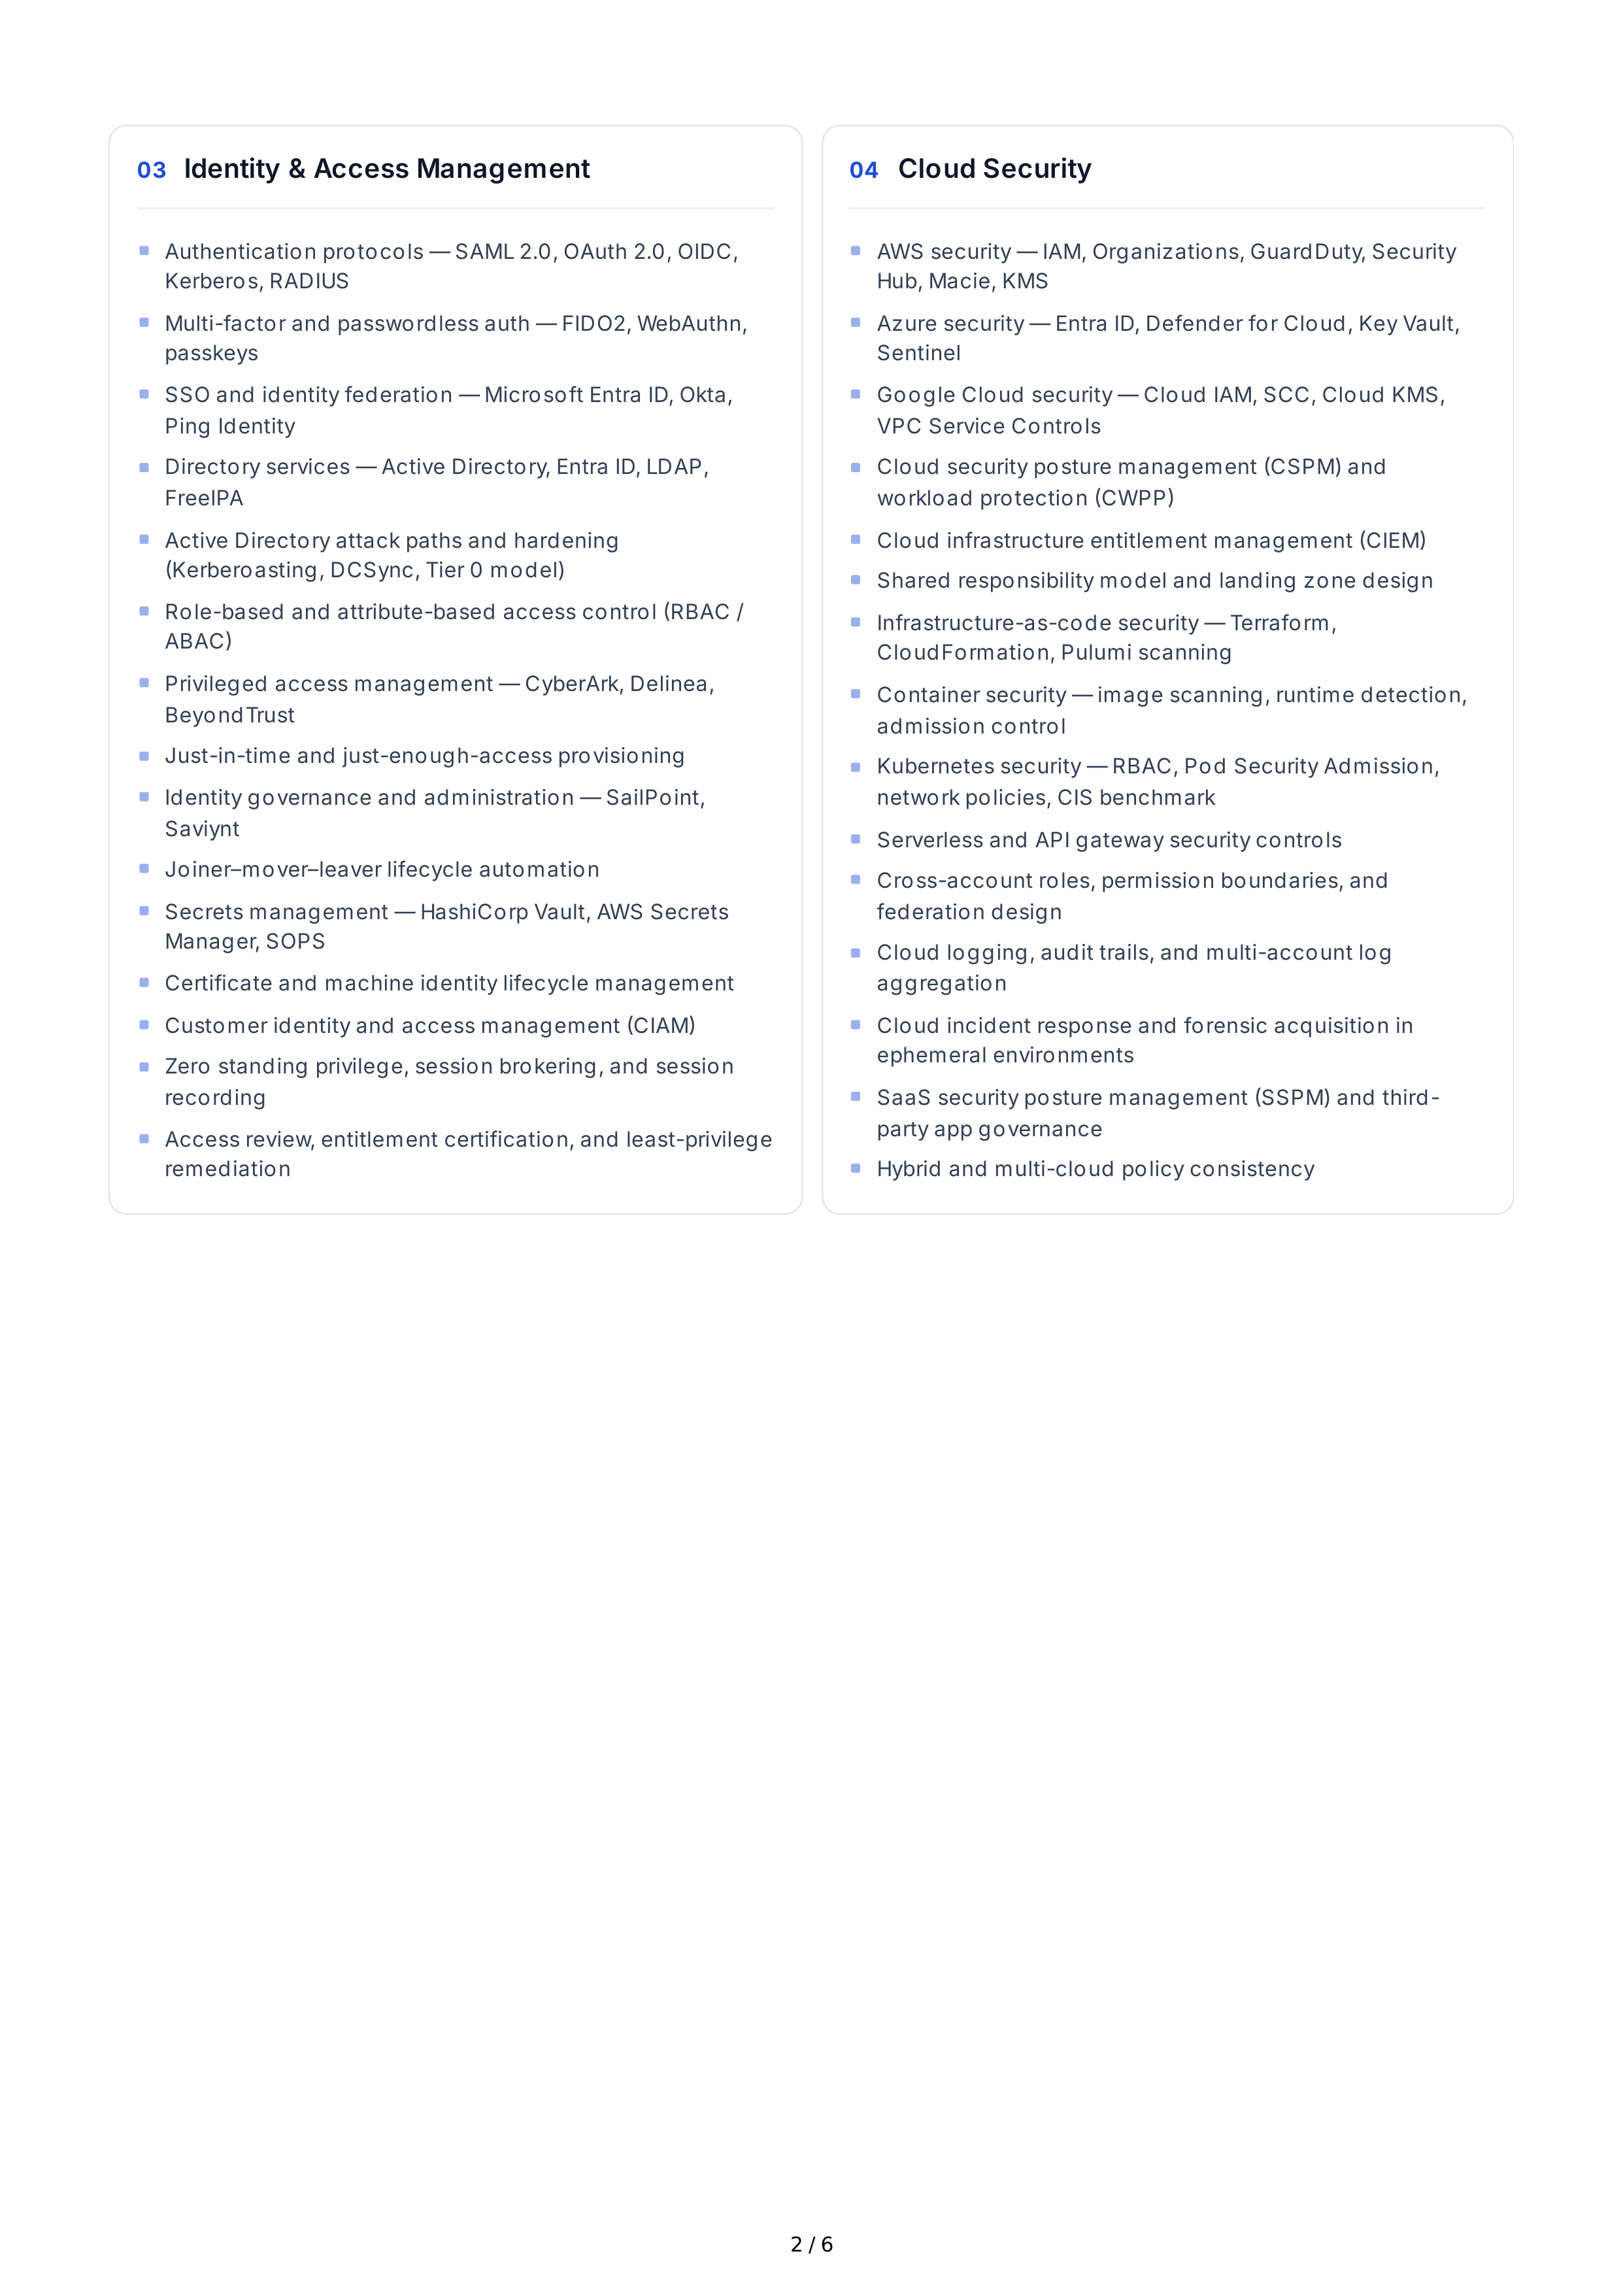
03
Identity
&
Access
Management
04
Cloud
Security
Authentication
protocols
—
SAML
2.0,
OAuth
2.0,
OIDC
,
Kerberos
,
RADIUS
Multi
-
factor
and
passwordless
auth
—
FIDO
2,
WebAuthn
,
passkeys
SSO
and
identity
federation
—
Microsoft
Entra
ID
,
Okta
,
Ping
Identity
Directory
services
—
Active
Directory
,
Entra
ID
,
LDAP
,
FreeIPA
Active
Directory
attack
paths
and
hardening
(
Kerberoasting
,
DCSync
,
Tier
0
model
)
Role
-
based
and
attribute
-
based
access
control
(
RBAC
/
ABAC
)
Privileged
access
management
—
CyberArk
,
Delinea
,
BeyondTrust
Just
-
in
-
time
and
just
-
enough
-
access
provisioning
Identity
governance
and
administration
—
SailPoint
,
Saviynt
Joiner
–
mover
–
leaver
lifecycle
automation
Secrets
management
—
HashiCorp
Vault
,
AWS
Secrets
Manager
,
SOPS
Certificate
and
machine
identity
lifecycle
management
Customer
identity
and
access
management
(
CIAM
)
Zero
standing
privilege
,
session
brokering
,
and
session
recording
Access
review
,
entitlement
certification
,
and
least
-
privilege
remediation
AWS
security
—
IAM
,
Organizations
,
GuardDuty
,
Security
Hub
,
Macie
,
KMS
Azure
security
—
Entra
ID
,
Defender
for
Cloud
,
Key
Vault
,
Sentinel
Google
Cloud
security
—
Cloud
IAM
,
SCC
,
Cloud
KMS
,
VPC
Service
Controls
Cloud
security
posture
management
(
CSPM
)
and
workload
protection
(
CWPP
)
Cloud
infrastructure
entitlement
management
(
CIEM
)
Shared
responsibility
model
and
landing
zone
design
Infrastructure
-
as
-
code
security
—
Terraform
,
CloudFormation
,
Pulumi
scanning
Container
security
—
image
scanning
,
runtime
detection
,
admission
control
Kubernetes
security
—
RBAC
,
Pod
Security
Admission
,
network
policies
,
CIS
benchmark
Serverless
and
API
gateway
security
controls
Cross
-
account
roles
,
permission
boundaries
,
and
federation
design
Cloud
logging
,
audit
trails
,
and
multi
-
account
log
aggregation
Cloud
incident
response
and
forensic
acquisition
in
ephemeral
environments
SaaS
security
posture
management
(
SSPM
)
and
third
-
party
app
governance
Hybrid
and
multi
-
cloud
policy
consistency
2 / 6
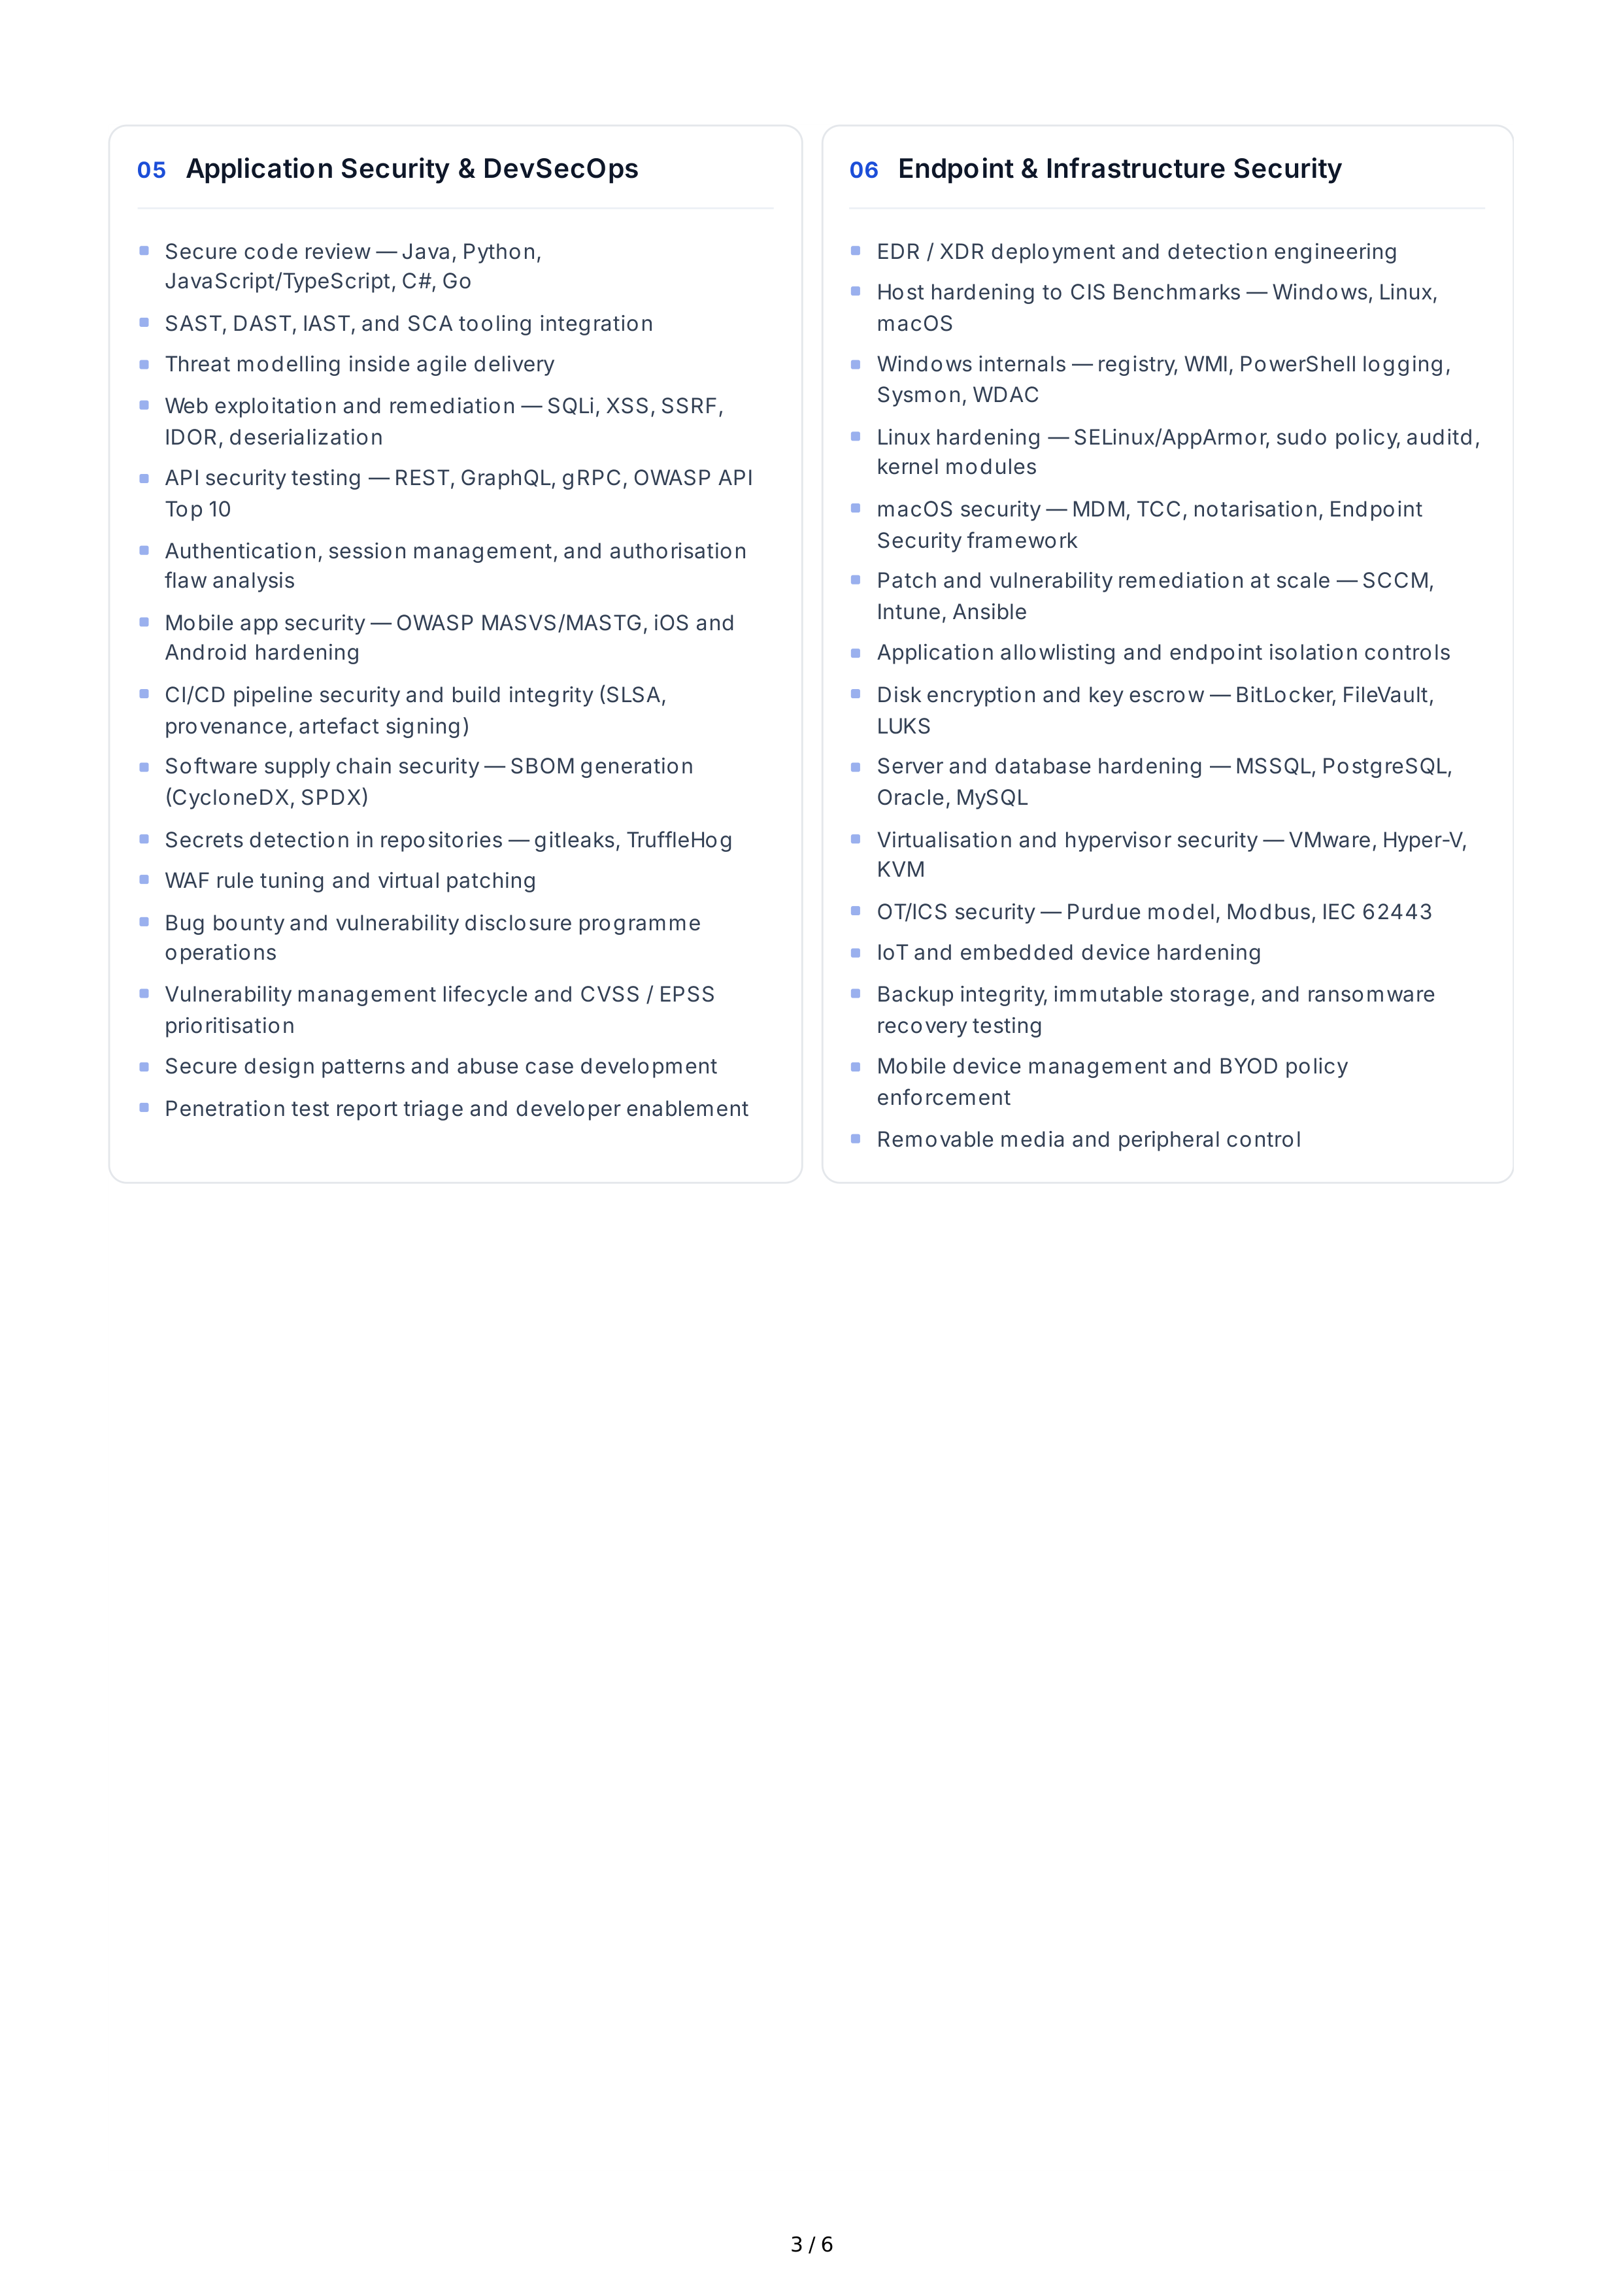
05
Application
Security
&
DevSecOps
06
Endpoint
&
Infrastructure
Security
Secure
code
review
—
Java
,
Python
,
JavaScript
/
TypeScript
,
C
#,
Go
SAST
,
DAST
,
IAST
,
and
SCA
tooling
integration
Threat
modelling
inside
agile
delivery
Web
exploitation
and
remediation
—
SQLi
,
XSS
,
SSRF
,
IDOR
,
deserialization
API
security
testing
—
REST
,
GraphQL
,
gRPC
,
OWASP
API
Top
10
Authentication
,
session
management
,
and
authorisation
flaw
analysis
Mobile
app
security
—
OWASP
MASVS
/
MASTG
,
iOS
and
Android
hardening
CI
/
CD
pipeline
security
and
build
integrity
(
SLSA
,
provenance
,
artefact
signing
)
Software
supply
chain
security
—
SBOM
generation
(
CycloneDX
,
SPDX
)
Secrets
detection
in
repositories
—
gitleaks
,
TruffleHog
WAF
rule
tuning
and
virtual
patching
Bug
bounty
and
vulnerability
disclosure
programme
operations
Vulnerability
management
lifecycle
and
CVSS
/
EPSS
prioritisation
Secure
design
patterns
and
abuse
case
development
Penetration
test
report
triage
and
developer
enablement
EDR
/
XDR
deployment
and
detection
engineering
Host
hardening
to
CIS
Benchmarks
—
Windows
,
Linux
,
macOS
Windows
internals
—
registry
,
WMI
,
PowerShell
logging
,
Sysmon
,
WDAC
Linux
hardening
—
SELinux
/
AppArmor
,
sudo
policy
,
auditd
,
kernel
modules
macOS
security
—
MDM
,
TCC
,
notarisation
,
Endpoint
Security
framework
Patch
and
vulnerability
remediation
at
scale
—
SCCM
,
Intune
,
Ansible
Application
allowlisting
and
endpoint
isolation
controls
Disk
encryption
and
key
escrow
—
BitLocker
,
FileVault
,
LUKS
Server
and
database
hardening
—
MSSQL
,
PostgreSQL
,
Oracle
,
MySQL
Virtualisation
and
hypervisor
security
—
VMware
,
Hyper
-
V
,
KVM
OT
/
ICS
security
—
Purdue
model
,
Modbus
,
IEC
62443
IoT
and
embedded
device
hardening
Backup
integrity
,
immutable
storage
,
and
ransomware
recovery
testing
Mobile
device
management
and
BYOD
policy
enforcement
Removable
media
and
peripheral
control
3 / 6
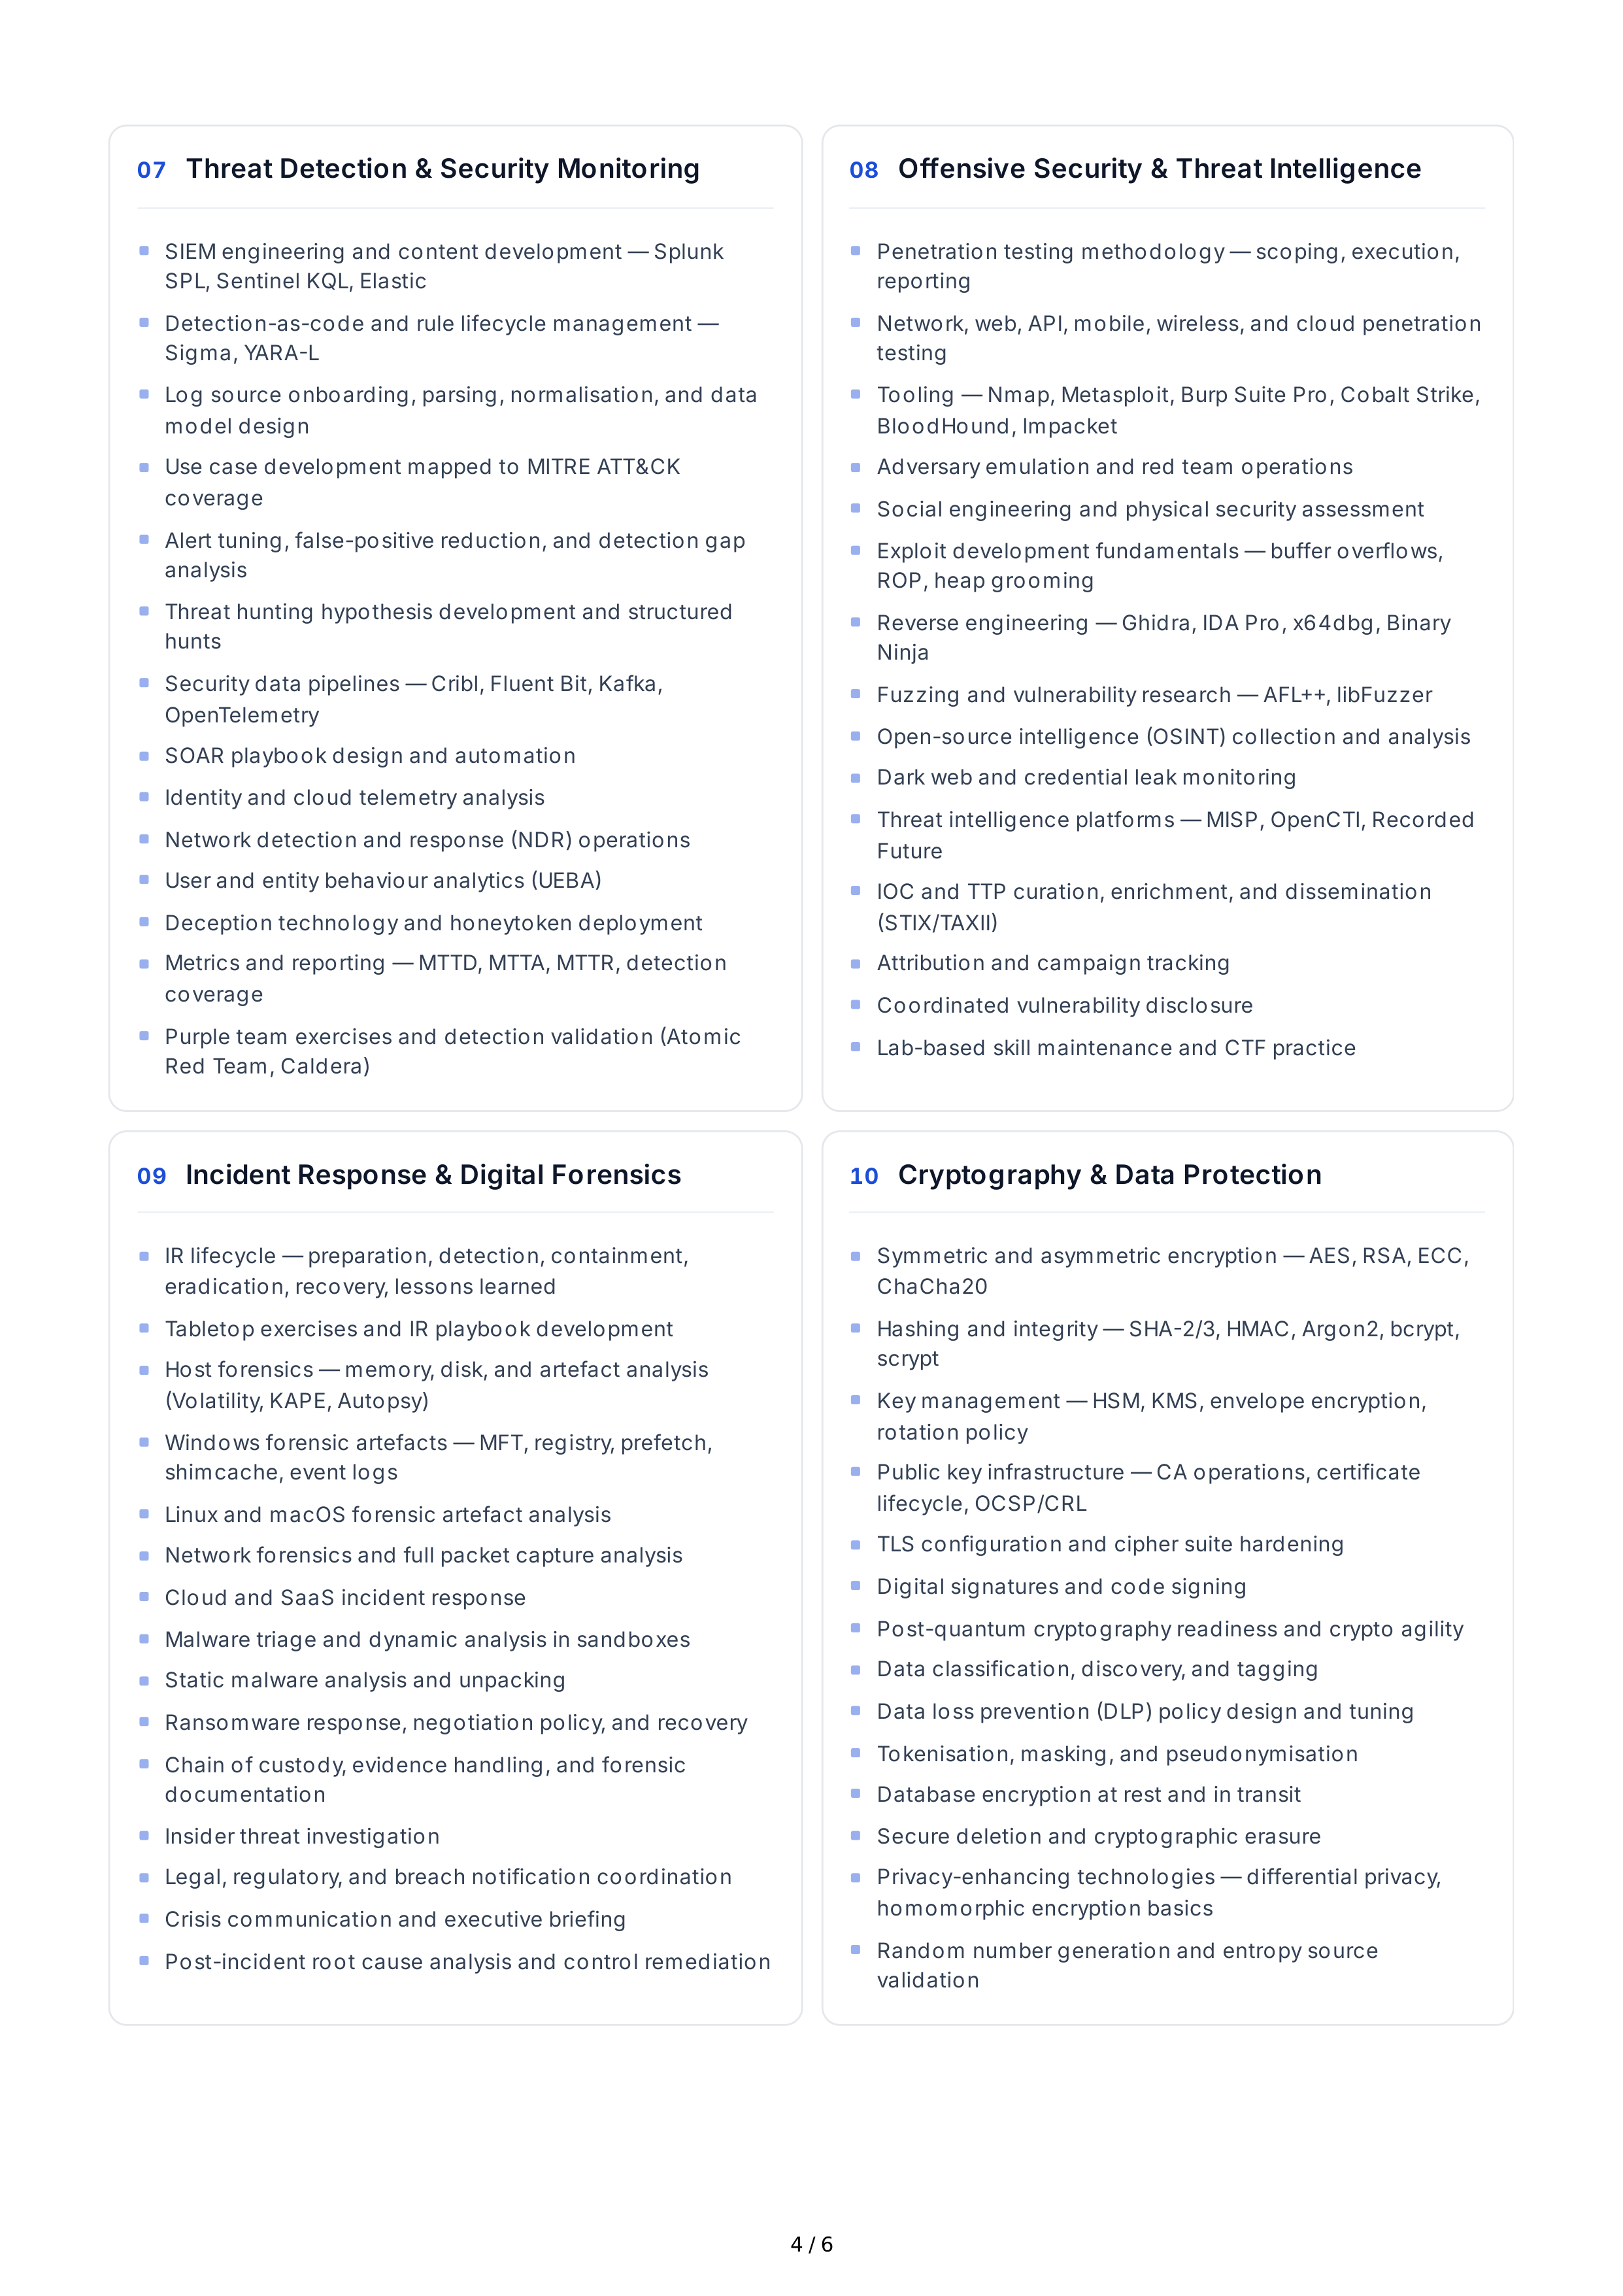
07
Threat
Detection
&
Security
Monitoring
08
Offensive
Security
&
Threat
Intelligence
09
Incident
Response
&
Digital
Forensics
10
Cryptography
&
Data
Protection
SIEM
engineering
and
content
development
—
Splunk
SPL
,
Sentinel
KQL
,
Elastic
Detection
-
as
-
code
and
rule
lifecycle
management
—
Sigma
,
YARA
-
L
Log
source
onboarding
,
parsing
,
normalisation
,
and
data
model
design
Use
case
development
mapped
to
MITRE
ATT
&
CK
coverage
Alert
tuning
,
false
-
positive
reduction
,
and
detection
gap
analysis
Threat
hunting
hypothesis
development
and
structured
hunts
Security
data
pipelines
—
Cribl
,
Fluent
Bit
,
Kafka
,
OpenTelemetry
SOAR
playbook
design
and
automation
Identity
and
cloud
telemetry
analysis
Network
detection
and
response
(
NDR
)
operations
User
and
entity
behaviour
analytics
(
UEBA
)
Deception
technology
and
honeytoken
deployment
Metrics
and
reporting
—
MTTD
,
MTTA
,
MTTR
,
detection
coverage
Purple
team
exercises
and
detection
validation
(
Atomic
Red
Team
,
Caldera
)
Penetration
testing
methodology
—
scoping
,
execution
,
reporting
Network
,
web
,
API
,
mobile
,
wireless
,
and
cloud
penetration
testing
Tooling
—
Nmap
,
Metasploit
,
Burp
Suite
Pro
,
Cobalt
Strike
,
BloodHound
,
Impacket
Adversary
emulation
and
red
team
operations
Social
engineering
and
physical
security
assessment
Exploit
development
fundamentals
—
buffer
overflows
,
ROP
,
heap
grooming
Reverse
engineering
—
Ghidra
,
IDA
Pro
,
x
64
dbg
,
Binary
Ninja
Fuzzing
and
vulnerability
research
—
AFL
++,
libFuzzer
Open
-
source
intelligence
(
OSINT
)
collection
and
analysis
Dark
web
and
credential
leak
monitoring
Threat
intelligence
platforms
—
MISP
,
OpenCTI
,
Recorded
Future
IOC
and
TTP
curation
,
enrichment
,
and
dissemination
(
STIX
/
TAXII
)
Attribution
and
campaign
tracking
Coordinated
vulnerability
disclosure
Lab
-
based
skill
maintenance
and
CTF
practice
IR
lifecycle
—
preparation
,
detection
,
containment
,
eradication
,
recovery
,
lessons
learned
Tabletop
exercises
and
IR
playbook
development
Host
forensics
—
memory
,
disk
,
and
artefact
analysis
(
Volatility
,
KAPE
,
Autopsy
)
Windows
forensic
artefacts
—
MFT
,
registry
,
prefetch
,
shimcache
,
event
logs
Linux
and
macOS
forensic
artefact
analysis
Network
forensics
and
full
packet
capture
analysis
Cloud
and
SaaS
incident
response
Malware
triage
and
dynamic
analysis
in
sandboxes
Static
malware
analysis
and
unpacking
Ransomware
response
,
negotiation
policy
,
and
recovery
Chain
of
custody
,
evidence
handling
,
and
forensic
documentation
Insider
threat
investigation
Legal
,
regulatory
,
and
breach
notification
coordination
Crisis
communication
and
executive
briefing
Post
-
incident
root
cause
analysis
and
control
remediation
Symmetric
and
asymmetric
encryption
—
AES
,
RSA
,
ECC
,
ChaCha
20
Hashing
and
integrity
—
SHA
-2/3,
HMAC
,
Argon
2,
bcrypt
,
scrypt
Key
management
—
HSM
,
KMS
,
envelope
encryption
,
rotation
policy
Public
key
infrastructure
—
CA
operations
,
certificate
lifecycle
,
OCSP
/
CRL
TLS
configuration
and
cipher
suite
hardening
Digital
signatures
and
code
signing
Post
-
quantum
cryptography
readiness
and
crypto
agility
Data
classification
,
discovery
,
and
tagging
Data
loss
prevention
(
DLP
)
policy
design
and
tuning
Tokenisation
,
masking
,
and
pseudonymisation
Database
encryption
at
rest
and
in
transit
Secure
deletion
and
cryptographic
erasure
Privacy
-
enhancing
technologies
—
differential
privacy
,
homomorphic
encryption
basics
Random
number
generation
and
entropy
source
validation
4 / 6
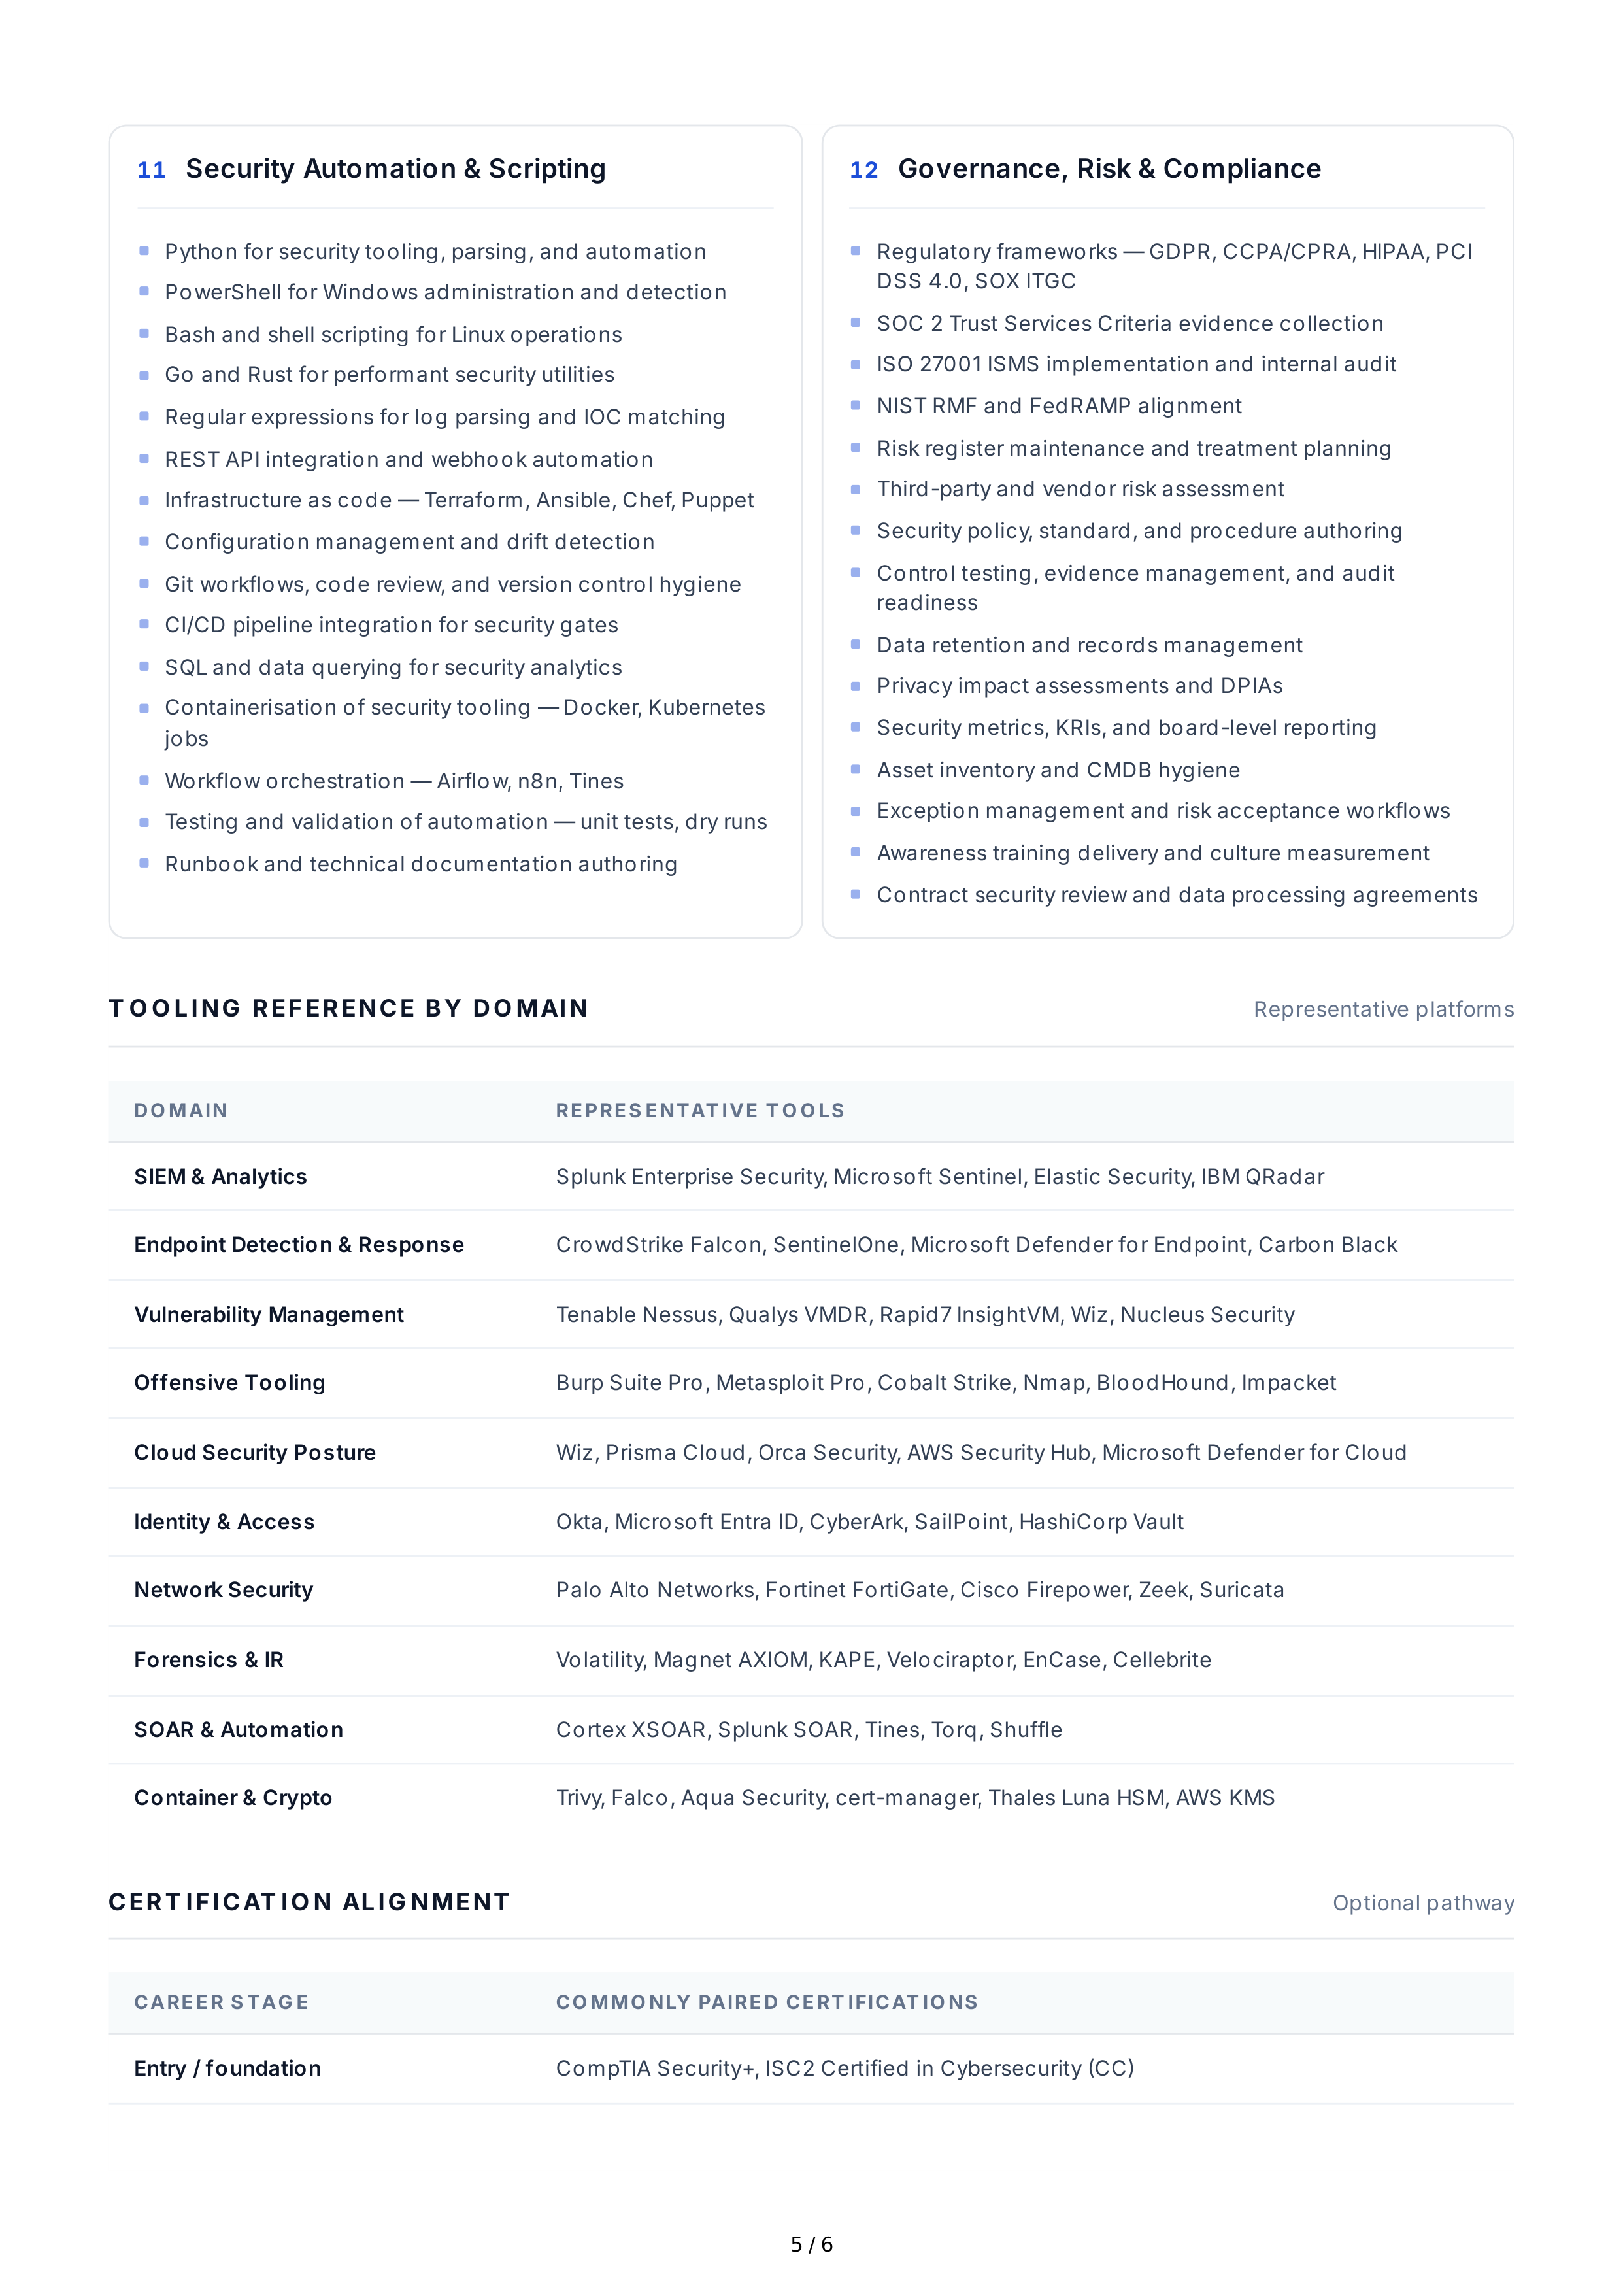
11
Security
Automation
&
Scripting
12
Governance
,
Risk
&
Compliance
T O O L ING
REFERENCE
BY
DO MAIN
Representative
platforms
DO MAIN
REPRES ENTAT IVE
T O O LS
SIEM
&
Analytics
Splunk
Enterprise
Security
,
Microsoft
Sentinel
,
Elastic
Security
,
IBM
QRadar
Endpoint
Detection
&
Response
CrowdStrike
Falcon
,
SentinelOne
,
Microsoft
Defender
for
Endpoint
,
Carbon
Black
Vulnerability
Management
Tenable
Nessus
,
Qualys
VMDR
,
Rapid
7
InsightVM
,
Wiz
,
Nucleus
Security
Offensive
Tooling
Burp
Suite
Pro
,
Metasploit
Pro
,
Cobalt
Strike
,
Nmap
,
BloodHound
,
Impacket
Cloud
Security
Posture
Wiz
,
Prisma
Cloud
,
Orca
Security
,
AWS
Security
Hub
,
Microsoft
Defender
for
Cloud
Identity
&
Access
Okta
,
Microsoft
Entra
ID
,
CyberArk
,
SailPoint
,
HashiCorp
Vault
Network
Security
Palo
Alto
Networks
,
Fortinet
FortiGate
,
Cisco
Firepower
,
Zeek
,
Suricata
Forensics
&
IR
Volatility
,
Magnet
AXIOM
,
KAPE
,
Velociraptor
,
EnCase
,
Cellebrite
SOAR
&
Automation
Cortex
XSOAR
,
Splunk
SOAR
,
Tines
,
Torq
,
Shuffle
Container
&
Crypto
Trivy
,
Falco
,
Aqua
Security
,
cert
-
manager
,
Thales
Luna
HSM
,
AWS
KMS
CERT IFICAT IO N
AL IG NMENT
Optional
pathway
CAREER
S TAG E
CO MMO NLY
PAIRED
CERT IFICAT IO NS
Entry
/
foundation
CompTIA
Security
+,
ISC
2
Certified
in
Cybersecurity
(
CC
)
Python
for
security
tooling
,
parsing
,
and
automation
PowerShell
for
Windows
administration
and
detection
Bash
and
shell
scripting
for
Linux
operations
Go
and
Rust
for
performant
security
utilities
Regular
expressions
for
log
parsing
and
IOC
matching
REST
API
integration
and
webhook
automation
Infrastructure
as
code
—
Terraform
,
Ansible
,
Chef
,
Puppet
Configuration
management
and
drift
detection
Git
workflows
,
code
review
,
and
version
control
hygiene
CI
/
CD
pipeline
integration
for
security
gates
SQL
and
data
querying
for
security
analytics
Containerisation
of
security
tooling
—
Docker
,
Kubernetes
jobs
Workflow
orchestration
—
Airflow
,
n
8
n
,
Tines
Testing
and
validation
of
automation
—
unit
tests
,
dry
runs
Runbook
and
technical
documentation
authoring
Regulatory
frameworks
—
GDPR
,
CCPA
/
CPRA
,
HIPAA
,
PCI
DSS
4.0,
SOX
ITGC
SOC
2
Trust
Services
Criteria
evidence
collection
ISO
27001
ISMS
implementation
and
internal
audit
NIST
RMF
and
FedRAMP
alignment
Risk
register
maintenance
and
treatment
planning
Third
-
party
and
vendor
risk
assessment
Security
policy
,
standard
,
and
procedure
authoring
Control
testing
,
evidence
management
,
and
audit
readiness
Data
retention
and
records
management
Privacy
impact
assessments
and
DPIAs
Security
metrics
,
KRIs
,
and
board
-
level
reporting
Asset
inventory
and
CMDB
hygiene
Exception
management
and
risk
acceptance
workflows
Awareness
training
delivery
and
culture
measurement
Contract
security
review
and
data
processing
agreements
5 / 6
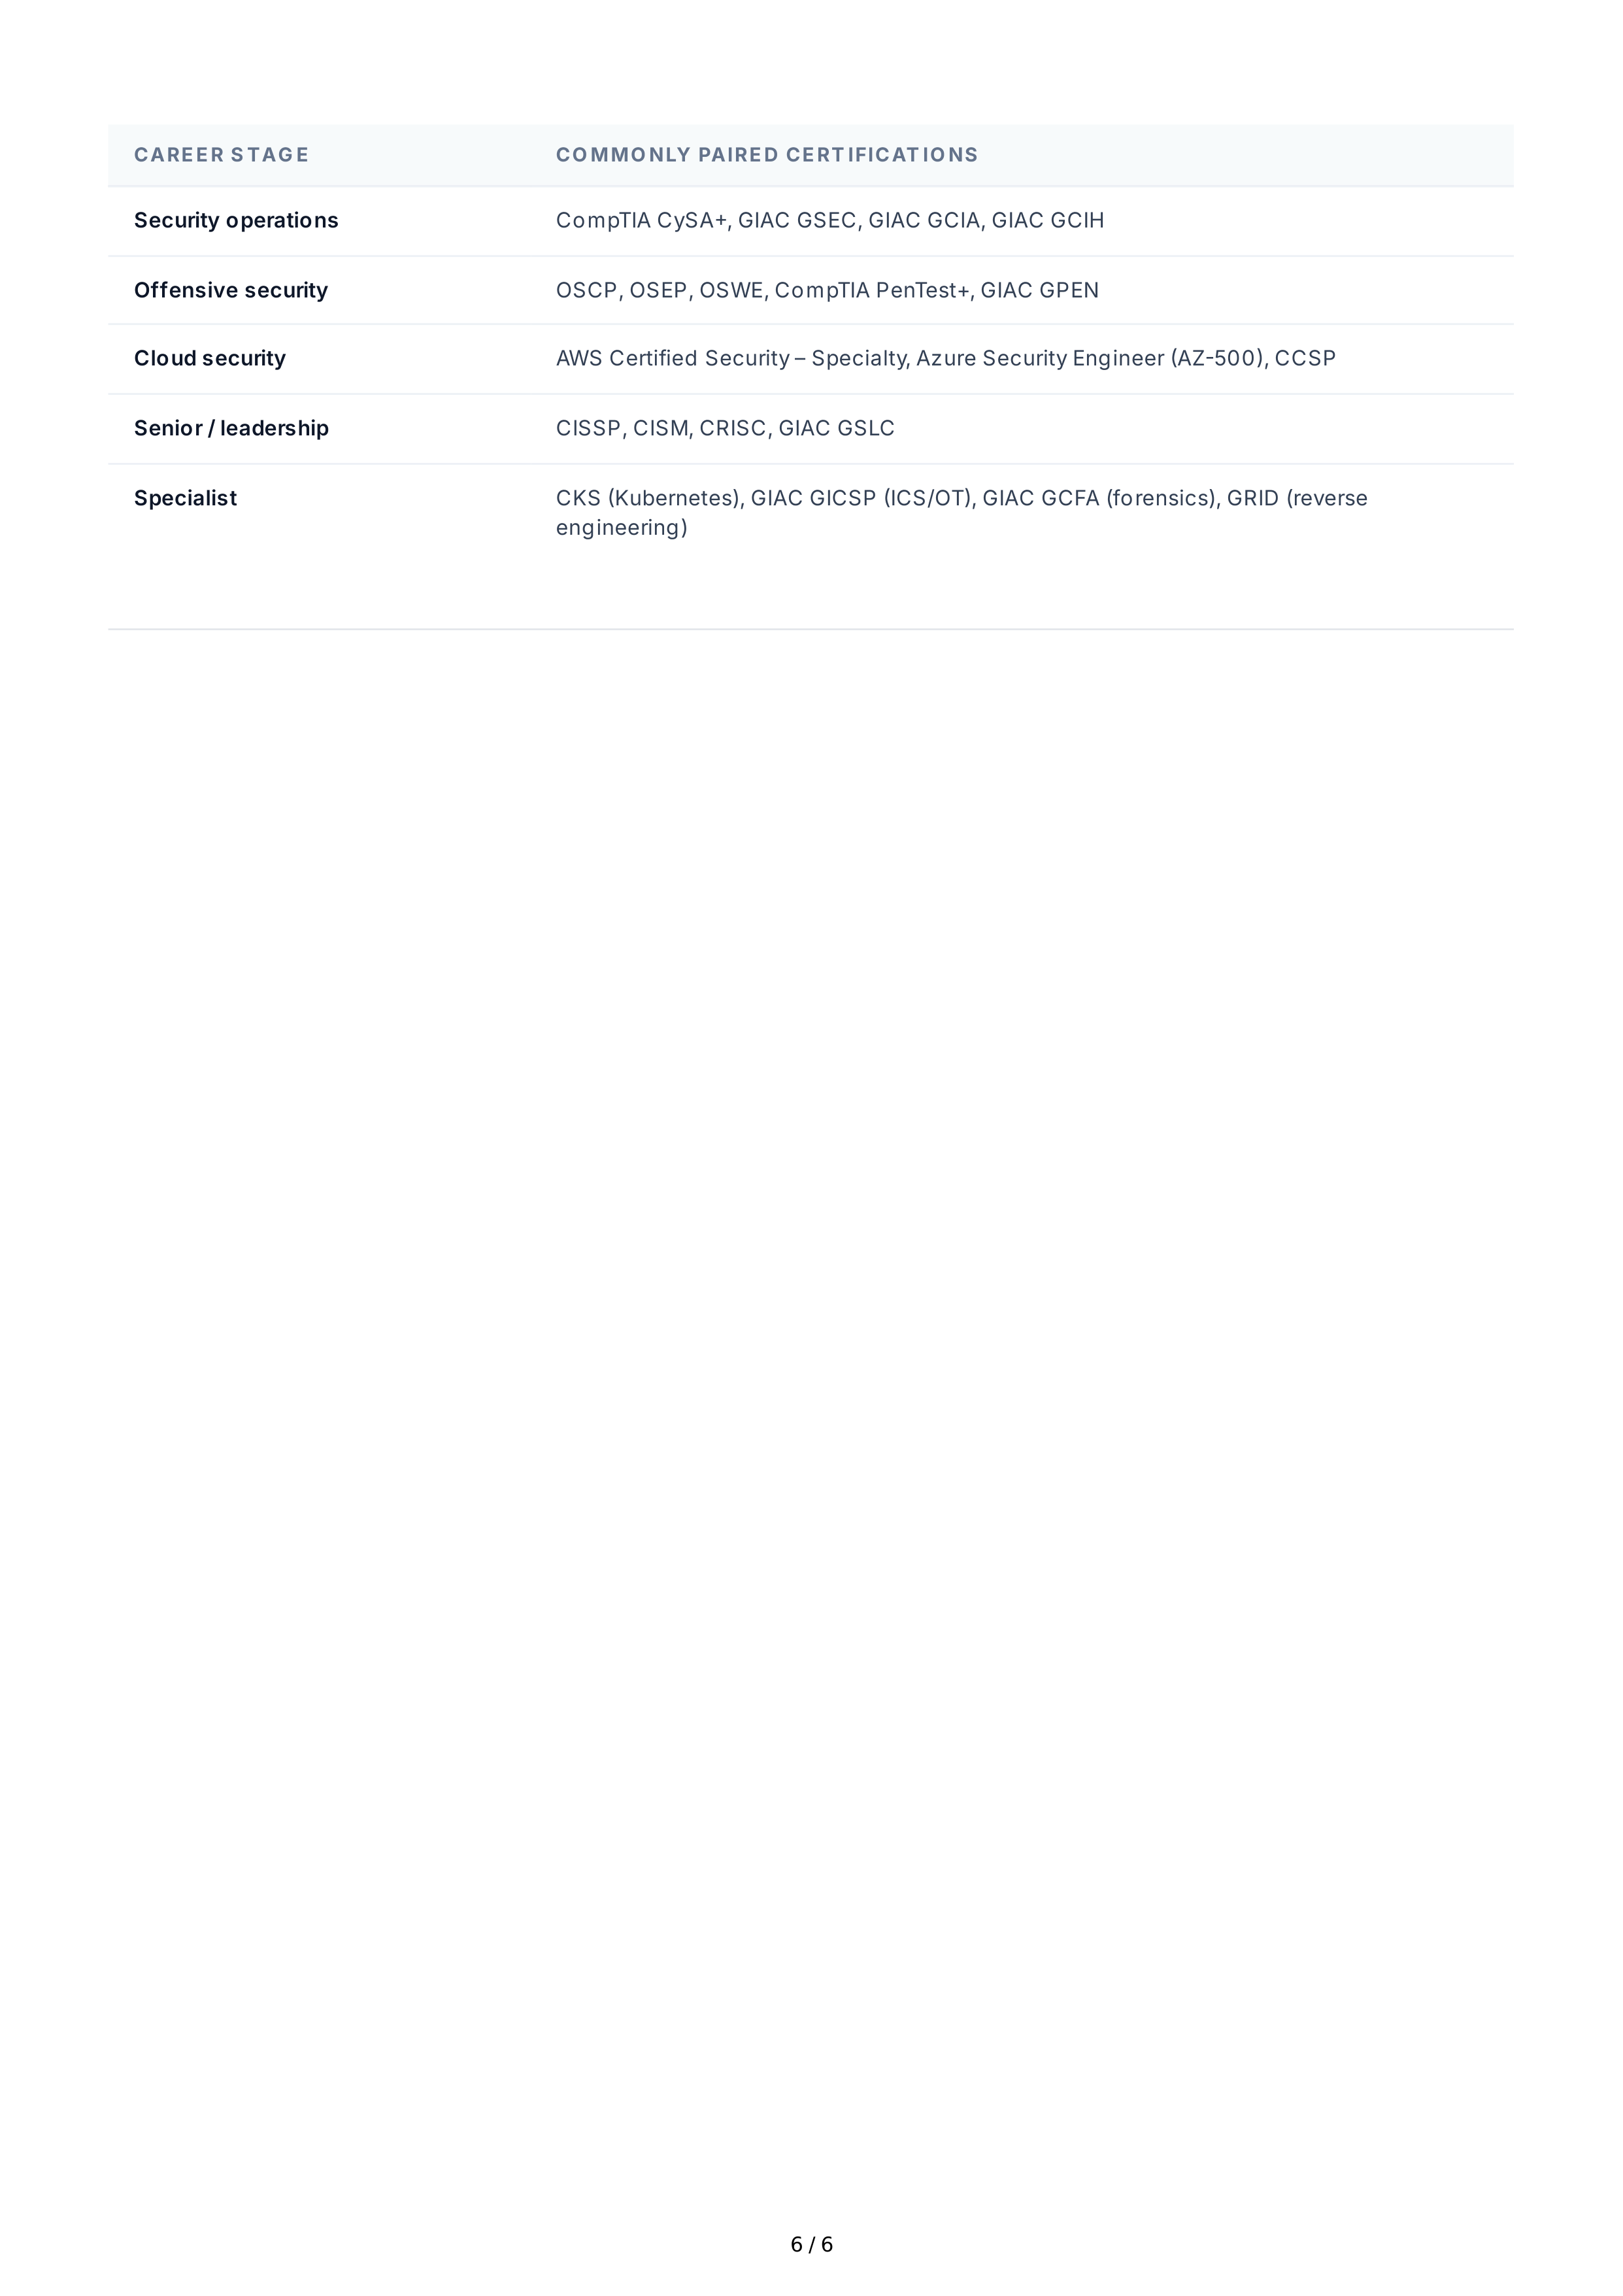
CAREER
S TAG E
CO MMO NLY
PAIRED
CERT IFICAT IO NS
Security
operations
CompTIA
CySA
+,
GIAC
GSEC
,
GIAC
GCIA
,
GIAC
GCIH
Offensive
security
OSCP
,
OSEP
,
OSWE
,
CompTIA
PenTest
+,
GIAC
GPEN
Cloud
security
AWS
Certified
Security
–
Specialty
,
Azure
Security
Engineer
(
AZ
-500),
CCSP
Senior
/
leadership
CISSP
,
CISM
,
CRISC
,
GIAC
GSLC
Specialist
CKS
(
Kubernetes
),
GIAC
GICSP
(
ICS
/
OT
),
GIAC
GCFA
(
forensics
),
GRID
(
reverse
engineering
)
6 / 6