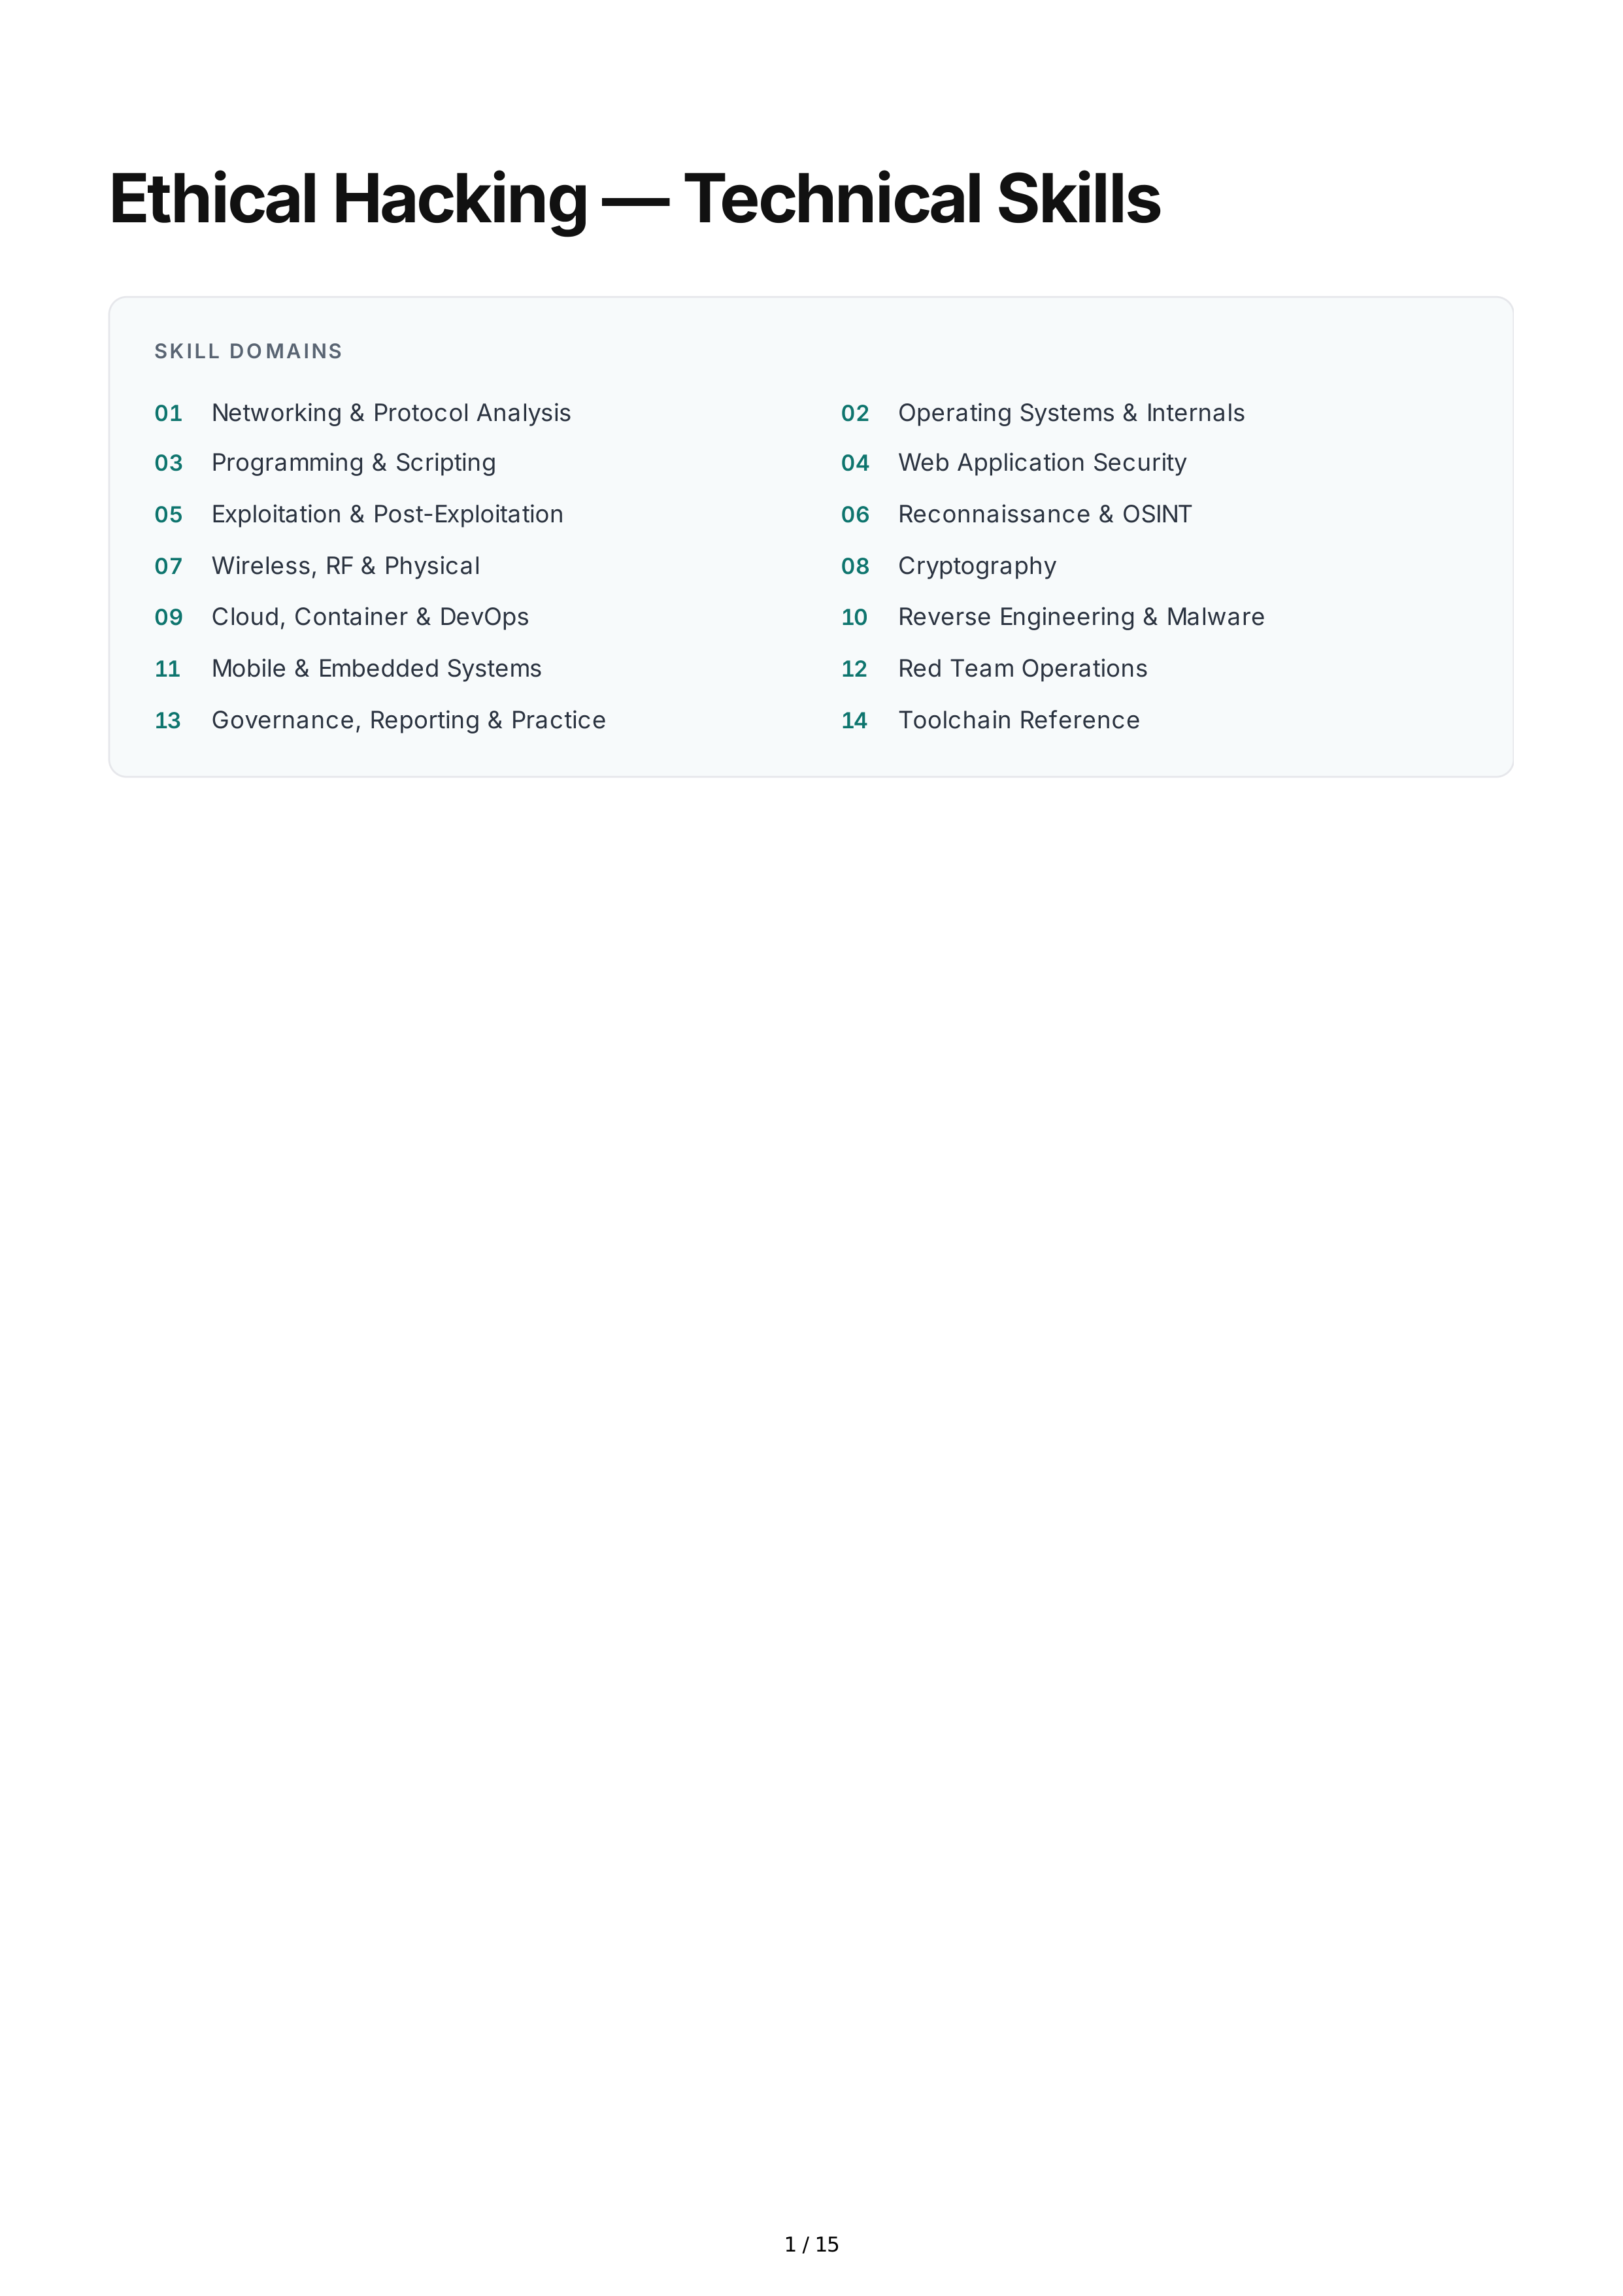
Ethical
Hacking
—
Technical
Skills
SKILL
DO MAINS
01
Networking
&
Protocol
Analysis
02
Operating
Systems
&
Internals
03
Programming
&
Scripting
04
Web
Application
Security
05
Exploitation
&
Post
-
Exploitation
06
Reconnaissance
&
OSINT
07
Wireless
,
RF
&
Physical
08
Cryptography
09
Cloud
,
Container
&
DevOps
10
Reverse
Engineering
&
Malware
11
Mobile
&
Embedded
Systems
12
Red
Team
Operations
13
Governance
,
Reporting
&
Practice
14
Toolchain
Reference
1 / 15
01
Networking
&
Protocol
Analysis
The
foundation
of
every
offensive
engagement
—
packets
first
,
exploits
second
.
TCP
/
IP
stack
fundamentals
Subnetting
,
CIDR
notation
,
routing
tables
,
NAT
,
and
the
OSI
model
applied
to
real
captured
traffic
.
Packet
capture
and
analysis
Wireshark
and
tcpdump
,
BPF
filter
syntax
,
TCP
stream
reassembly
,
and
TLS
decryption
using
session
key
logs
.
Protocol
dissection
Working
knowledge
of
DNS
,
DHCP
,
HTTP
/1.1
and
HTTP
/2,
TLS
,
SMB
,
Kerberos
,
LDAP
,
RDP
and
SNMP
at
the
byte
level
.
Network
scanning
and
enumeration
Nmap
host
discovery
,
SYN
/
UDP
/
ACK
scans
,
service
and
version
detection
,
operating
system
fingerprinting
,
NSE
scripting
.
Man
-
in
-
the
-
middle
techniques
ARP
cache
poisoning
,
LLMNR
/
NBT
-
NS
/
mDNS
poisoning
with
Responder
,
and
traffic
interception
and
rewriting
with
Bettercap
.
Segmentation
and
firewall
testing
VLAN
hopping
, 802.1
Q
trunk
abuse
,
ACL
bypass
,
and
validating
internal
east
-
west
filtering
rules
.
IPv
6
attack
surface
Router
advertisement
flooding
,
SLAAC
spoofing
,
DHCPv
6
takeover
,
and
dual
-
stack
gaps
where
IPv
4
is
filtered
but
IPv
6
is
not
.
IDS
/
IPS
and
firewall
evasion
Packet
fragmentation
,
source
-
port
manipulation
,
decoy
scans
,
timing
templates
,
and
encryption
of
command
channels
.
DNS
security
Zone
transfer
abuse
,
cache
poisoning
concepts
,
DNS
tunnelling
for
covert
exfiltration
,
and
resolver
misconfiguration
.
Tunnelling
and
pivoting
SSH
and
SOCKS
proxies
,
chisel
,
dnscat
2,
ICMP
tunnels
,
and
routing
traffic
through
compromised
internal
hosts
.
2 / 15
02
Operating
Systems
&
Internals
Comfort
at
the
command
line
is
assumed
;
understanding
why
the
command
works
is
the
skill
.
Linux
internals
File
permissions
,
SUID
/
SGID
binaries
,
capabilities
,
systemd
units
,
cron
and
timers
,
PAM
configuration
,
and
package
integrity
.
Windows
internals
Registry
hives
,
service
control
manager
,
WMI
,
token
privileges
,
access
tokens
,
and
process
and
thread
architecture
.
Active
Directory
architecture
Domains
,
forests
,
trusts
,
Group
Policy
,
Kerberos
ticketing
,
LDAP
queries
,
and
delegation
models
.
Linux
privilege
escalation
Enumeration
with
LinPEAS
,
GTFOBins
abuse
,
writable
service
files
,
misconfigured
sudo
rules
,
and
kernel
exploitation
.
Windows
privilege
escalation
Unquoted
service
paths
,
SeImpersonate
and
SeBackup
abuse
,
UAC
bypass
,
DLL
hijacking
,
and
token
impersonation
.
Shell
proficiency
Bash
and
PowerShell
fluency
including
piping
,
job
control
,
remote
execution
,
and
living
-
off
-
the
-
land
binaries
.
Persistence
mechanisms
Scheduled
tasks
,
registry
run
keys
,
service
creation
,
SSH
authorised
keys
,
and
how
defenders
detect
each
.
Hardening
knowledge
CIS
benchmark
configuration
,
patch
management
,
least
-
privilege
design
,
and
application
allow
-
listing
.
3 / 15
03
Programming
&
Scripting
You
cannot
automate
,
modify
or
weaponise
what
you
cannot
read
.
Python
Tooling
and
automation
with
requests
,
Scapy
,
Impacket
and
raw
socket
programming
;
parsing
output
from
third
-
party
tools
.
Bash
and
PowerShell
scripting
Task
automation
,
log
parsing
,
bulk
operations
,
and
remote
execution
across
large
host
sets
.
C
and
C
++
Memory
layout
,
pointer
arithmetic
,
stack
frames
,
and
writing
proof
-
of
-
concept
exploit
code
.
x
86/
x
64
and
ARM
assembly
Reading
disassembly
,
understanding
calling
conventions
,
and
locating
controllable
buffers
during
exploit
development
.
JavaScript
DOM
behaviour
,
prototype
pollution
,
event
handling
,
and
browser
-
based
payload
construction
.
SQL
Query
construction
,
joins
,
subqueries
,
and
the
syntax
required
for
injection
and
database
enumeration
.
Go
and
Ruby
Building
custom
tooling
,
cross
-
platform
implants
,
and
Metasploit
modules
.
Regex
and
data
parsing
Extracting
credentials
,
tokens
,
secrets
and
indicators
of
compromise
from
large
unstructured
data
sets
.
4 / 15
04
Web
Application
Security
The
largest
share
of
real
engagement
findings
lives
in
the
application
layer
.
OWASP
Top
10
fluency
Practical
exploitation
and
mitigation
awareness
across
every
category
,
not
merely
recognition
of
the
names
.
SQL
injection
Union
-
based
,
error
-
based
,
blind
boolean
and
time
-
based
techniques
,
plus
confident
sqlmap
usage
and
manual
verification
.
Cross
-
site
scripting
Reflected
,
stored
and
DOM
-
based
XSS
,
CSP
analysis
,
filter
and
WAF
bypasses
,
and
session
theft
impact
.
Access
control
flaws
IDOR
,
broken
object
-
level
authorisation
,
forced
browsing
,
and
vertical
and
horizontal
privilege
escalation
.
Server
-
side
request
forgery
Internal
service
access
,
cloud
metadata
endpoint
abuse
,
blind
SSRF
detection
,
and
protocol
smuggling
.
File
inclusion
and
upload
attacks
LFI
,
RFI
,
path
traversal
,
polyglot
payloads
,
MIME
confusion
,
and
web
shell
deployment
.
Authentication
and
session
attacks
JWT
manipulation
,
OAuth
misconfiguration
,
MFA
bypass
,
session
fixation
,
and
credential
stuffing
resistance
testing
.
Insecure
deserialization
Java
gadget
chains
, .
NET
ViewState
,
PHP
object
injection
,
and
Python
pickle
abuse
.
API
security
testing
REST
and
GraphQL
enumeration
,
schema
introspection
,
mass
assignment
,
rate
-
limit
abuse
,
and
versioning
gaps
.
Business
logic
exploitation
Workflow
bypass
,
price
and
quantity
manipulation
,
coupon
abuse
,
and
race
conditions
.
Server
-
side
template
injection
Detection
and
exploitation
across
Jinja
2,
Twig
,
Freemarker
and
Velocity
engines
.
Client
-
side
and
browser
security
CORS
misconfiguration
,
postMessage
abuse
,
clickjacking
,
and
content
sniffing
issues
.
Web
tooling
mastery
Burp
Suite
(
Proxy
,
Repeater
,
Intruder
,
Collaborator
),
OWASP
ZAP
,
ffuf
,
feroxbuster
,
and
Nuclei
templating
.
5 / 15
05
Exploitation
&
Post
-
Exploitation
From
initial
foothold
to
demonstrating
business
impact
.
Metasploit
framework
Module
selection
and
configuration
,
payload
generation
with
msfvenom
,
Meterpreter
post
modules
,
and
session
management
.
Buffer
overflow
exploitation
Stack
smashing
,
offset
discovery
,
shellcode
injection
,
bad
-
character
analysis
,
and
NOP
sleds
.
Modern
exploit
mitigations
ASLR
,
DEP
/
NX
,
stack
canaries
,
CFG
and
SafeSEH
,
plus
bypass
techniques
including
ROP
chain
construction
.
Password
attacks
Hashcat
and
John
the
Ripper
,
rule
-
based
and
mask
attacks
,
Kerberos
cracking
modes
,
and
password
spraying
strategy
.
Active
Directory
attacks
Kerberoasting
,
AS
-
REP
roasting
,
DCSync
,
Golden
and
Silver
tickets
,
unconstrained
and
constrained
delegation
abuse
.
Credential
relay
and
reuse
NTLM
relay
with
ntlmrelayx
,
Pass
-
the
-
Hash
,
Pass
-
the
-
Ticket
,
and
over
-
pass
-
the
-
hash
techniques
.
Lateral
movement
PsExec
,
WMI
,
WinRM
,
SMB
admin
shares
,
RDP
session
hijacking
,
and
internal
pivoting
.
Command
and
control
Cobalt
Strike
,
Sliver
and
Mythic
;
beacon
sleep
and
jitter
configuration
,
malleable
profiles
,
and
redirector
chains
.
Payload
evasion
Obfuscation
,
in
-
memory
execution
,
AMSI
and
ETW
bypass
fundamentals
,
and
EDR
behavioural
testing
.
Data
exfiltration
Covert
channels
,
staged
and
throttled
transfer
,
and
awareness
of
DLP
controls
during
objective
execution
.
Exploit
research
workflow
CVE
analysis
,
vendor
patch
diffing
,
and
safe
weaponisation
of
public
advisories
in
lab
conditions
.
6 / 15
06
Reconnaissance
&
OSINT
The
best
operators
spend
more
time
here
than
in
the
exploit
console
.
Passive
reconnaissance
Shodan
,
Censys
,
certificate
transparency
via
crt
.
sh
,
WHOIS
records
,
and
historical
DNS
data
.
Search
engine
intelligence
Advanced
Google
dorking
,
Bing
and
GitHub
code
search
for
leaked
credentials
and
exposed
configuration
.
Subdomain
and
asset
enumeration
Amass
,
Subfinder
,
Assetfinder
,
HTTPX
,
and
permutation
scanning
to
surface
forgotten
or
staging
hosts
.
Breach
and
credential
intelligence
Have
I
Been
Pwned
,
DeHashed
,
and
combolist
analysis
to
inform
password
spraying
within
scope
.
Metadata
harvesting
Document
metadata
,
EXIF
extraction
from
published
images
,
and
email
header
analysis
for
infrastructure
clues
.
Social
engineering
reconnaissance
Organisational
charting
,
employee
and
role
enumeration
,
and
building
credible
pretext
material
.
Attack
surface
management
Continuous
asset
discovery
,
shadow
IT
identification
,
and
exposure
prioritisation
across
subsidiaries
.
Infrastructure
fingerprinting
WAF
detection
,
CDN
identification
,
framework
and
version
profiling
,
and
origin
server
discovery
.
7 / 15
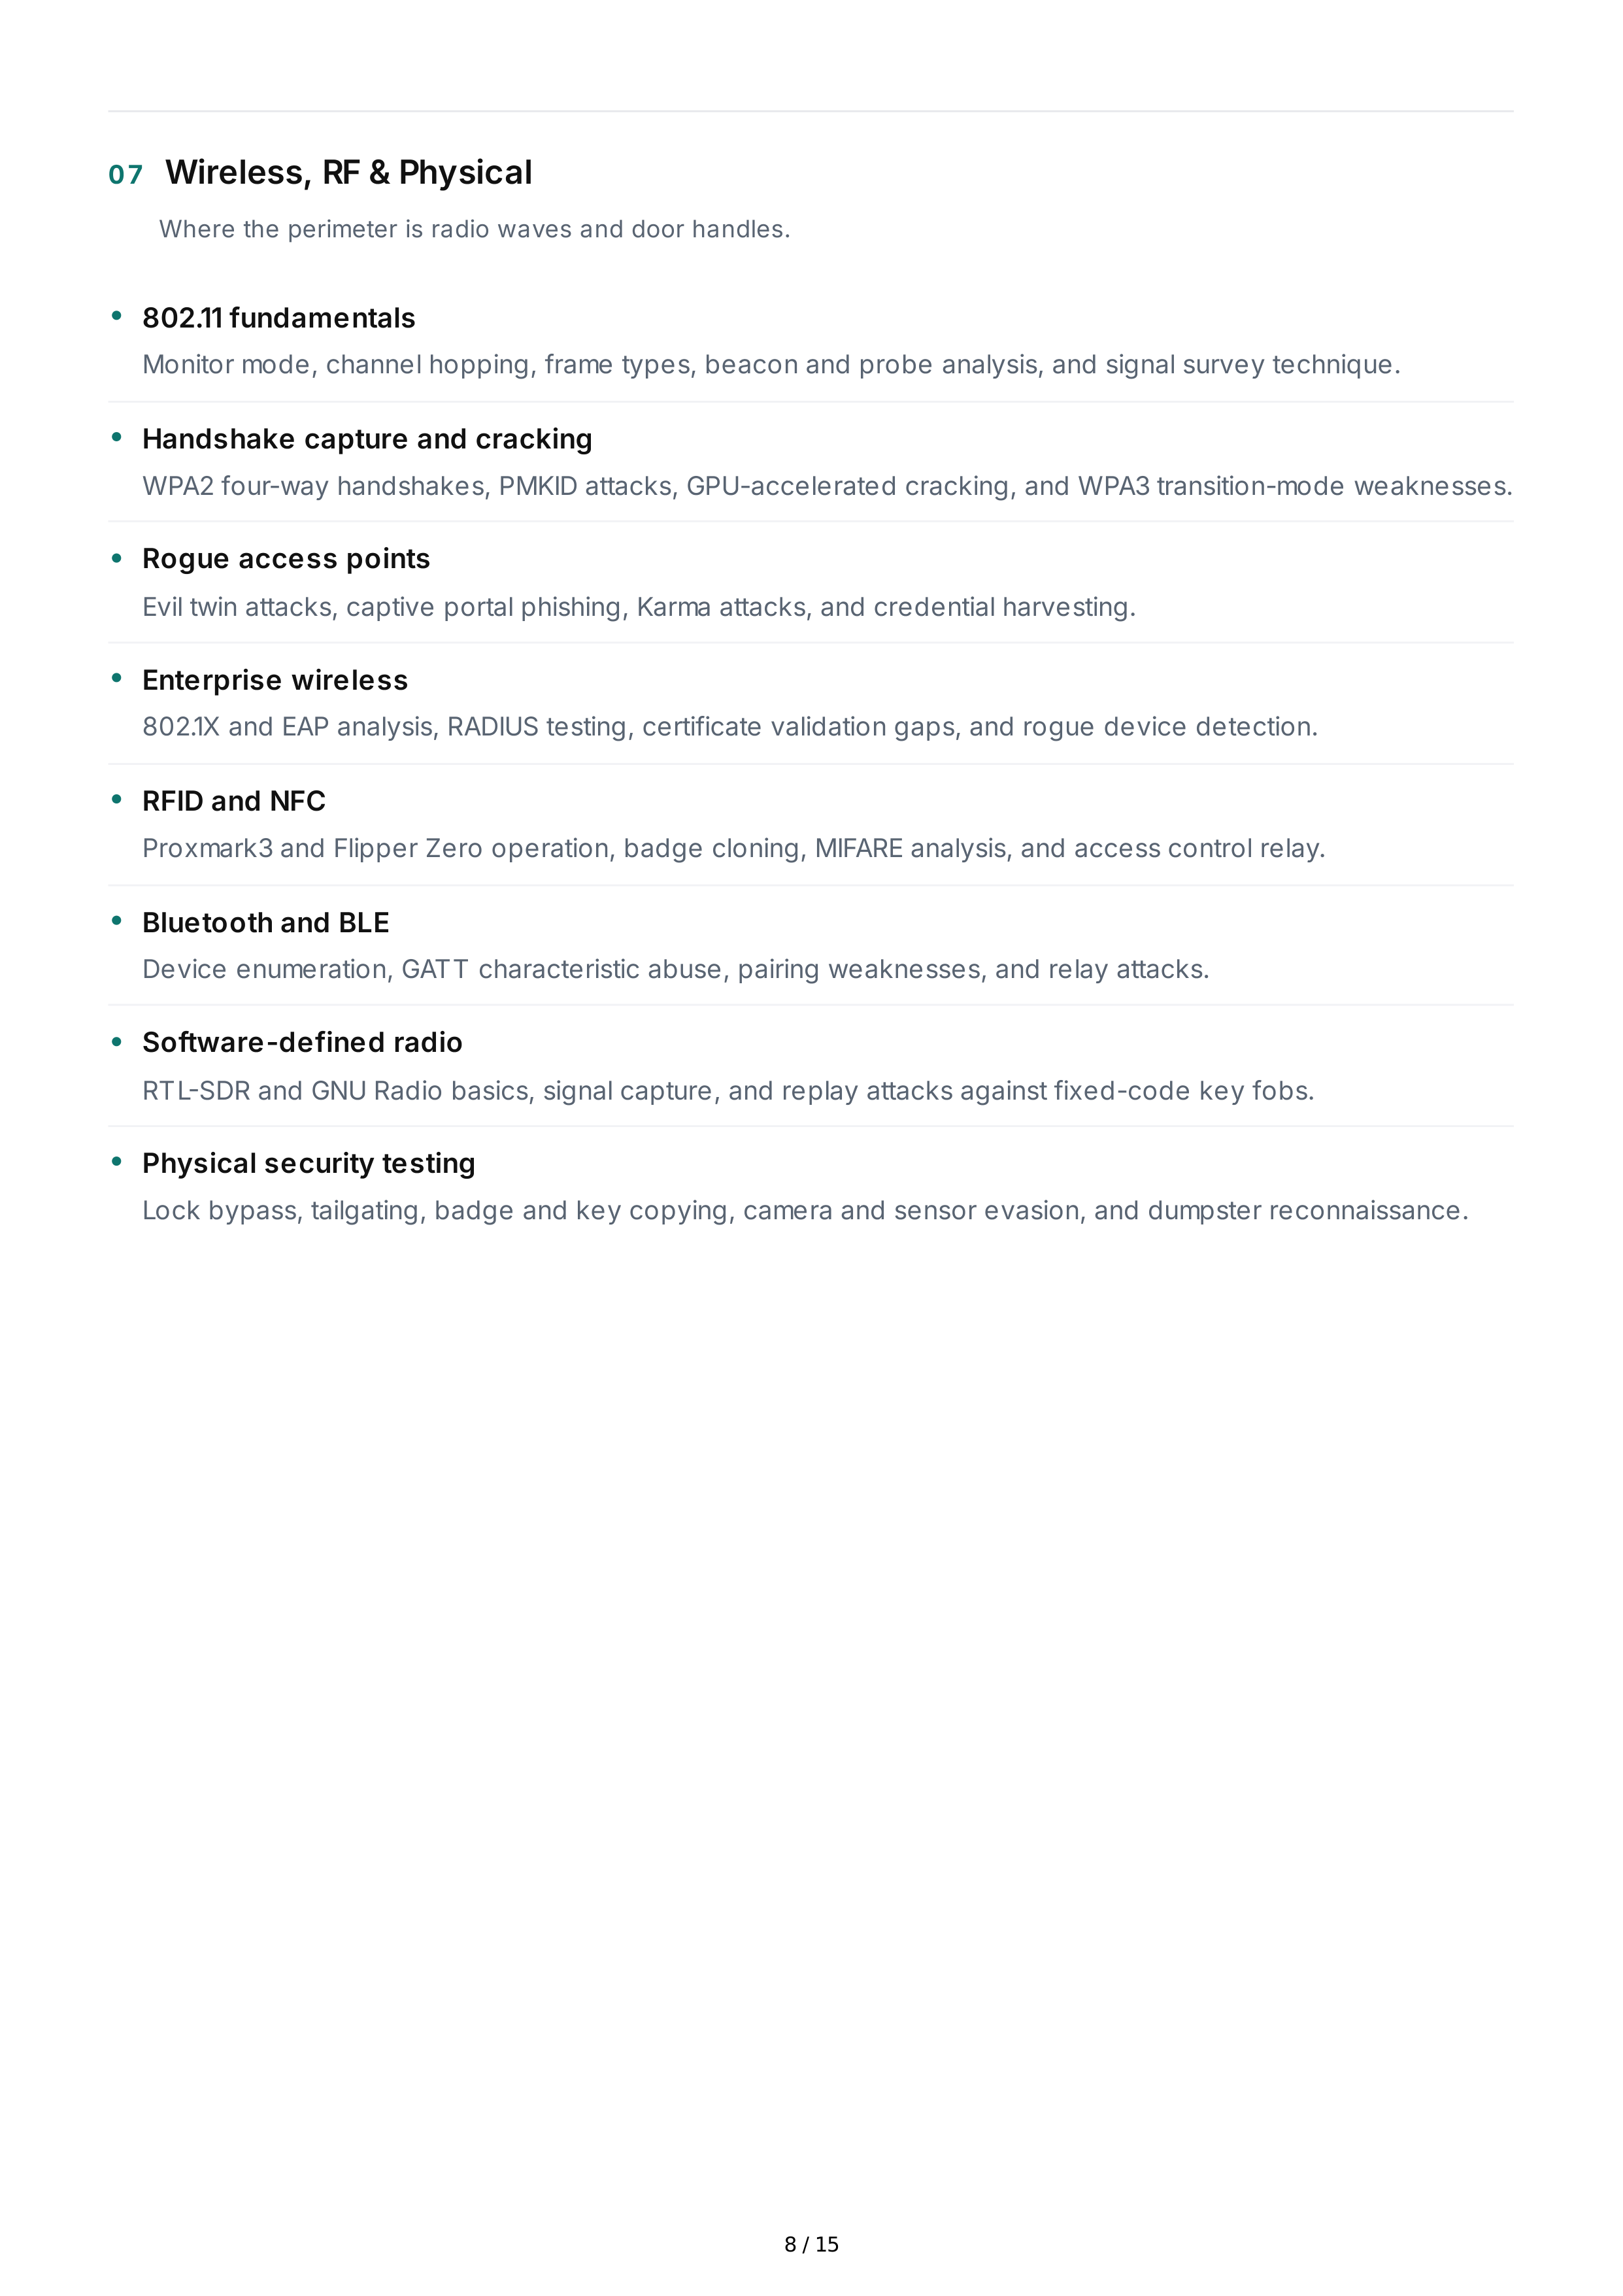
07
Wireless
,
RF
&
Physical
Where
the
perimeter
is
radio
waves
and
door
handles
.
802.11
fundamentals
Monitor
mode
,
channel
hopping
,
frame
types
,
beacon
and
probe
analysis
,
and
signal
survey
technique
.
Handshake
capture
and
cracking
WPA
2
four
-
way
handshakes
,
PMKID
attacks
,
GPU
-
accelerated
cracking
,
and
WPA
3
transition
-
mode
weaknesses
.
Rogue
access
points
Evil
twin
attacks
,
captive
portal
phishing
,
Karma
attacks
,
and
credential
harvesting
.
Enterprise
wireless
802.1
X
and
EAP
analysis
,
RADIUS
testing
,
certificate
validation
gaps
,
and
rogue
device
detection
.
RFID
and
NFC
Proxmark
3
and
Flipper
Zero
operation
,
badge
cloning
,
MIFARE
analysis
,
and
access
control
relay
.
Bluetooth
and
BLE
Device
enumeration
,
GATT
characteristic
abuse
,
pairing
weaknesses
,
and
relay
attacks
.
Software
-
defined
radio
RTL
-
SDR
and
GNU
Radio
basics
,
signal
capture
,
and
replay
attacks
against
fixed
-
code
key
fobs
.
Physical
security
testing
Lock
bypass
,
tailgating
,
badge
and
key
copying
,
camera
and
sensor
evasion
,
and
dumpster
reconnaissance
.
8 / 15
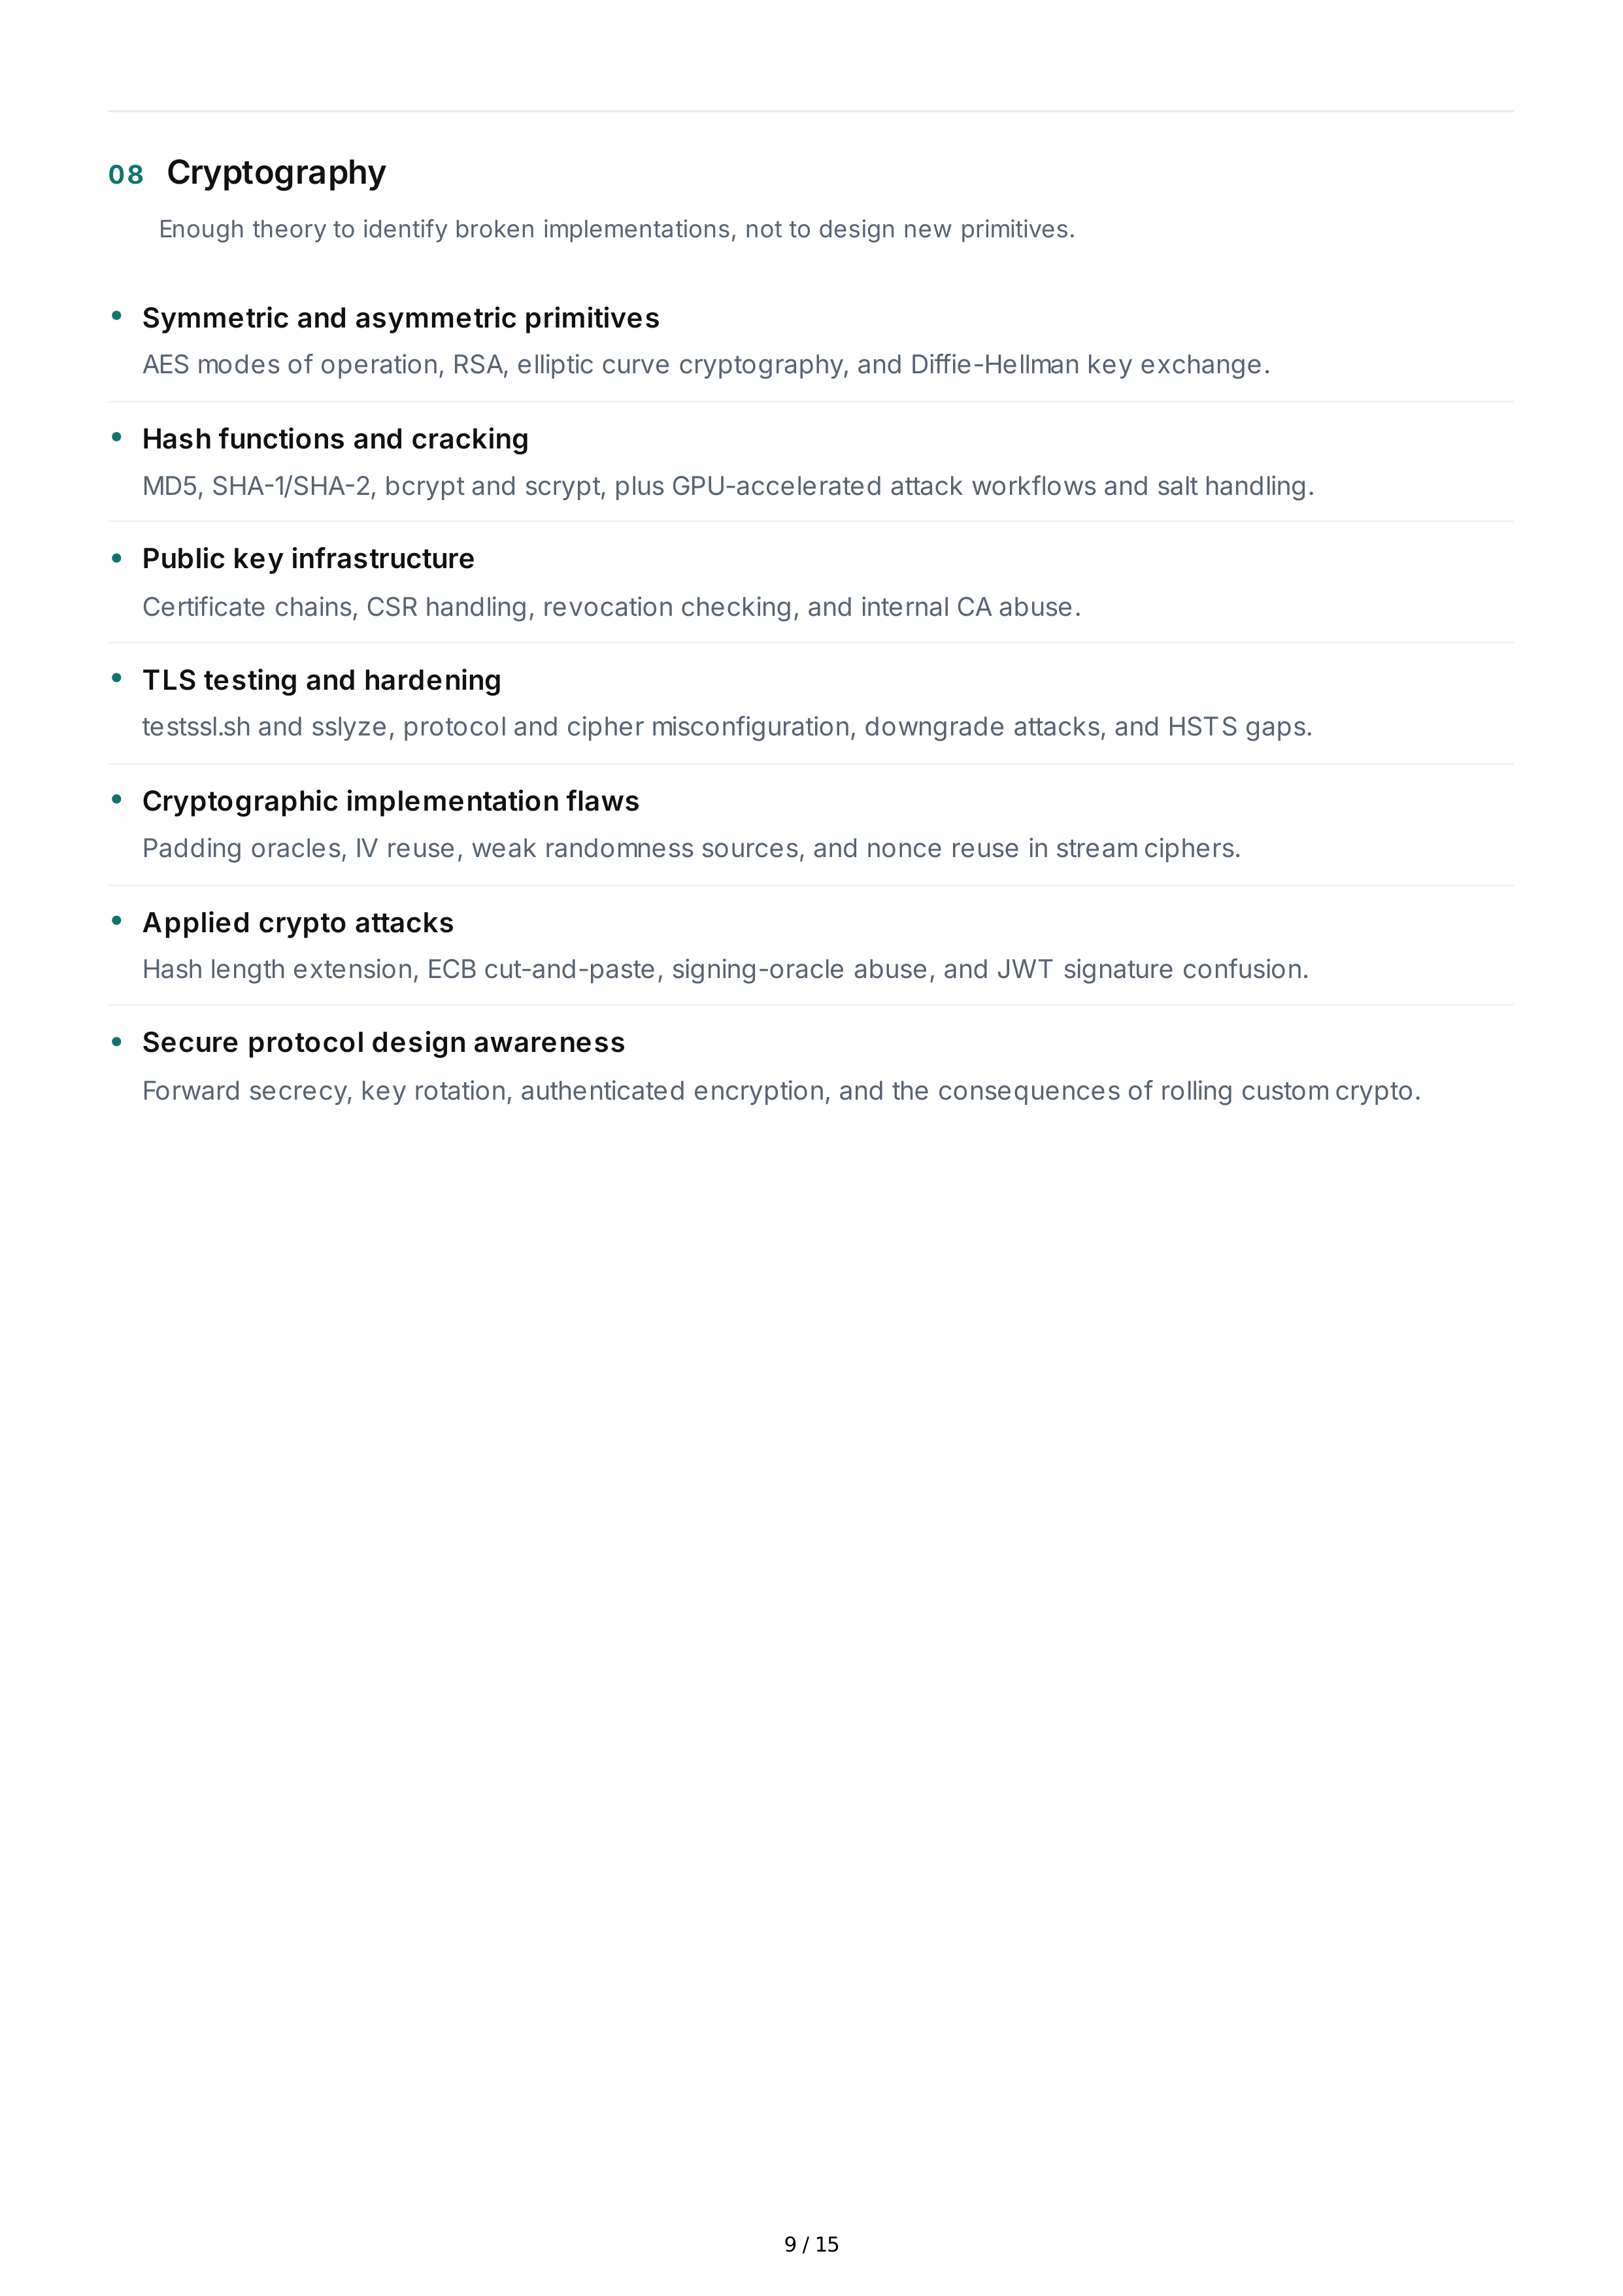
08
Cryptography
Enough
theory
to
identify
broken
implementations
,
not
to
design
new
primitives
.
Symmetric
and
asymmetric
primitives
AES
modes
of
operation
,
RSA
,
elliptic
curve
cryptography
,
and
Diffie
-
Hellman
key
exchange
.
Hash
functions
and
cracking
MD
5,
SHA
-1/
SHA
-2,
bcrypt
and
scrypt
,
plus
GPU
-
accelerated
attack
workflows
and
salt
handling
.
Public
key
infrastructure
Certificate
chains
,
CSR
handling
,
revocation
checking
,
and
internal
CA
abuse
.
TLS
testing
and
hardening
testssl
.
sh
and
sslyze
,
protocol
and
cipher
misconfiguration
,
downgrade
attacks
,
and
HSTS
gaps
.
Cryptographic
implementation
flaws
Padding
oracles
,
IV
reuse
,
weak
randomness
sources
,
and
nonce
reuse
in
stream
ciphers
.
Applied
crypto
attacks
Hash
length
extension
,
ECB
cut
-
and
-
paste
,
signing
-
oracle
abuse
,
and
JWT
signature
confusion
.
Secure
protocol
design
awareness
Forward
secrecy
,
key
rotation
,
authenticated
encryption
,
and
the
consequences
of
rolling
custom
crypto
.
9 / 15
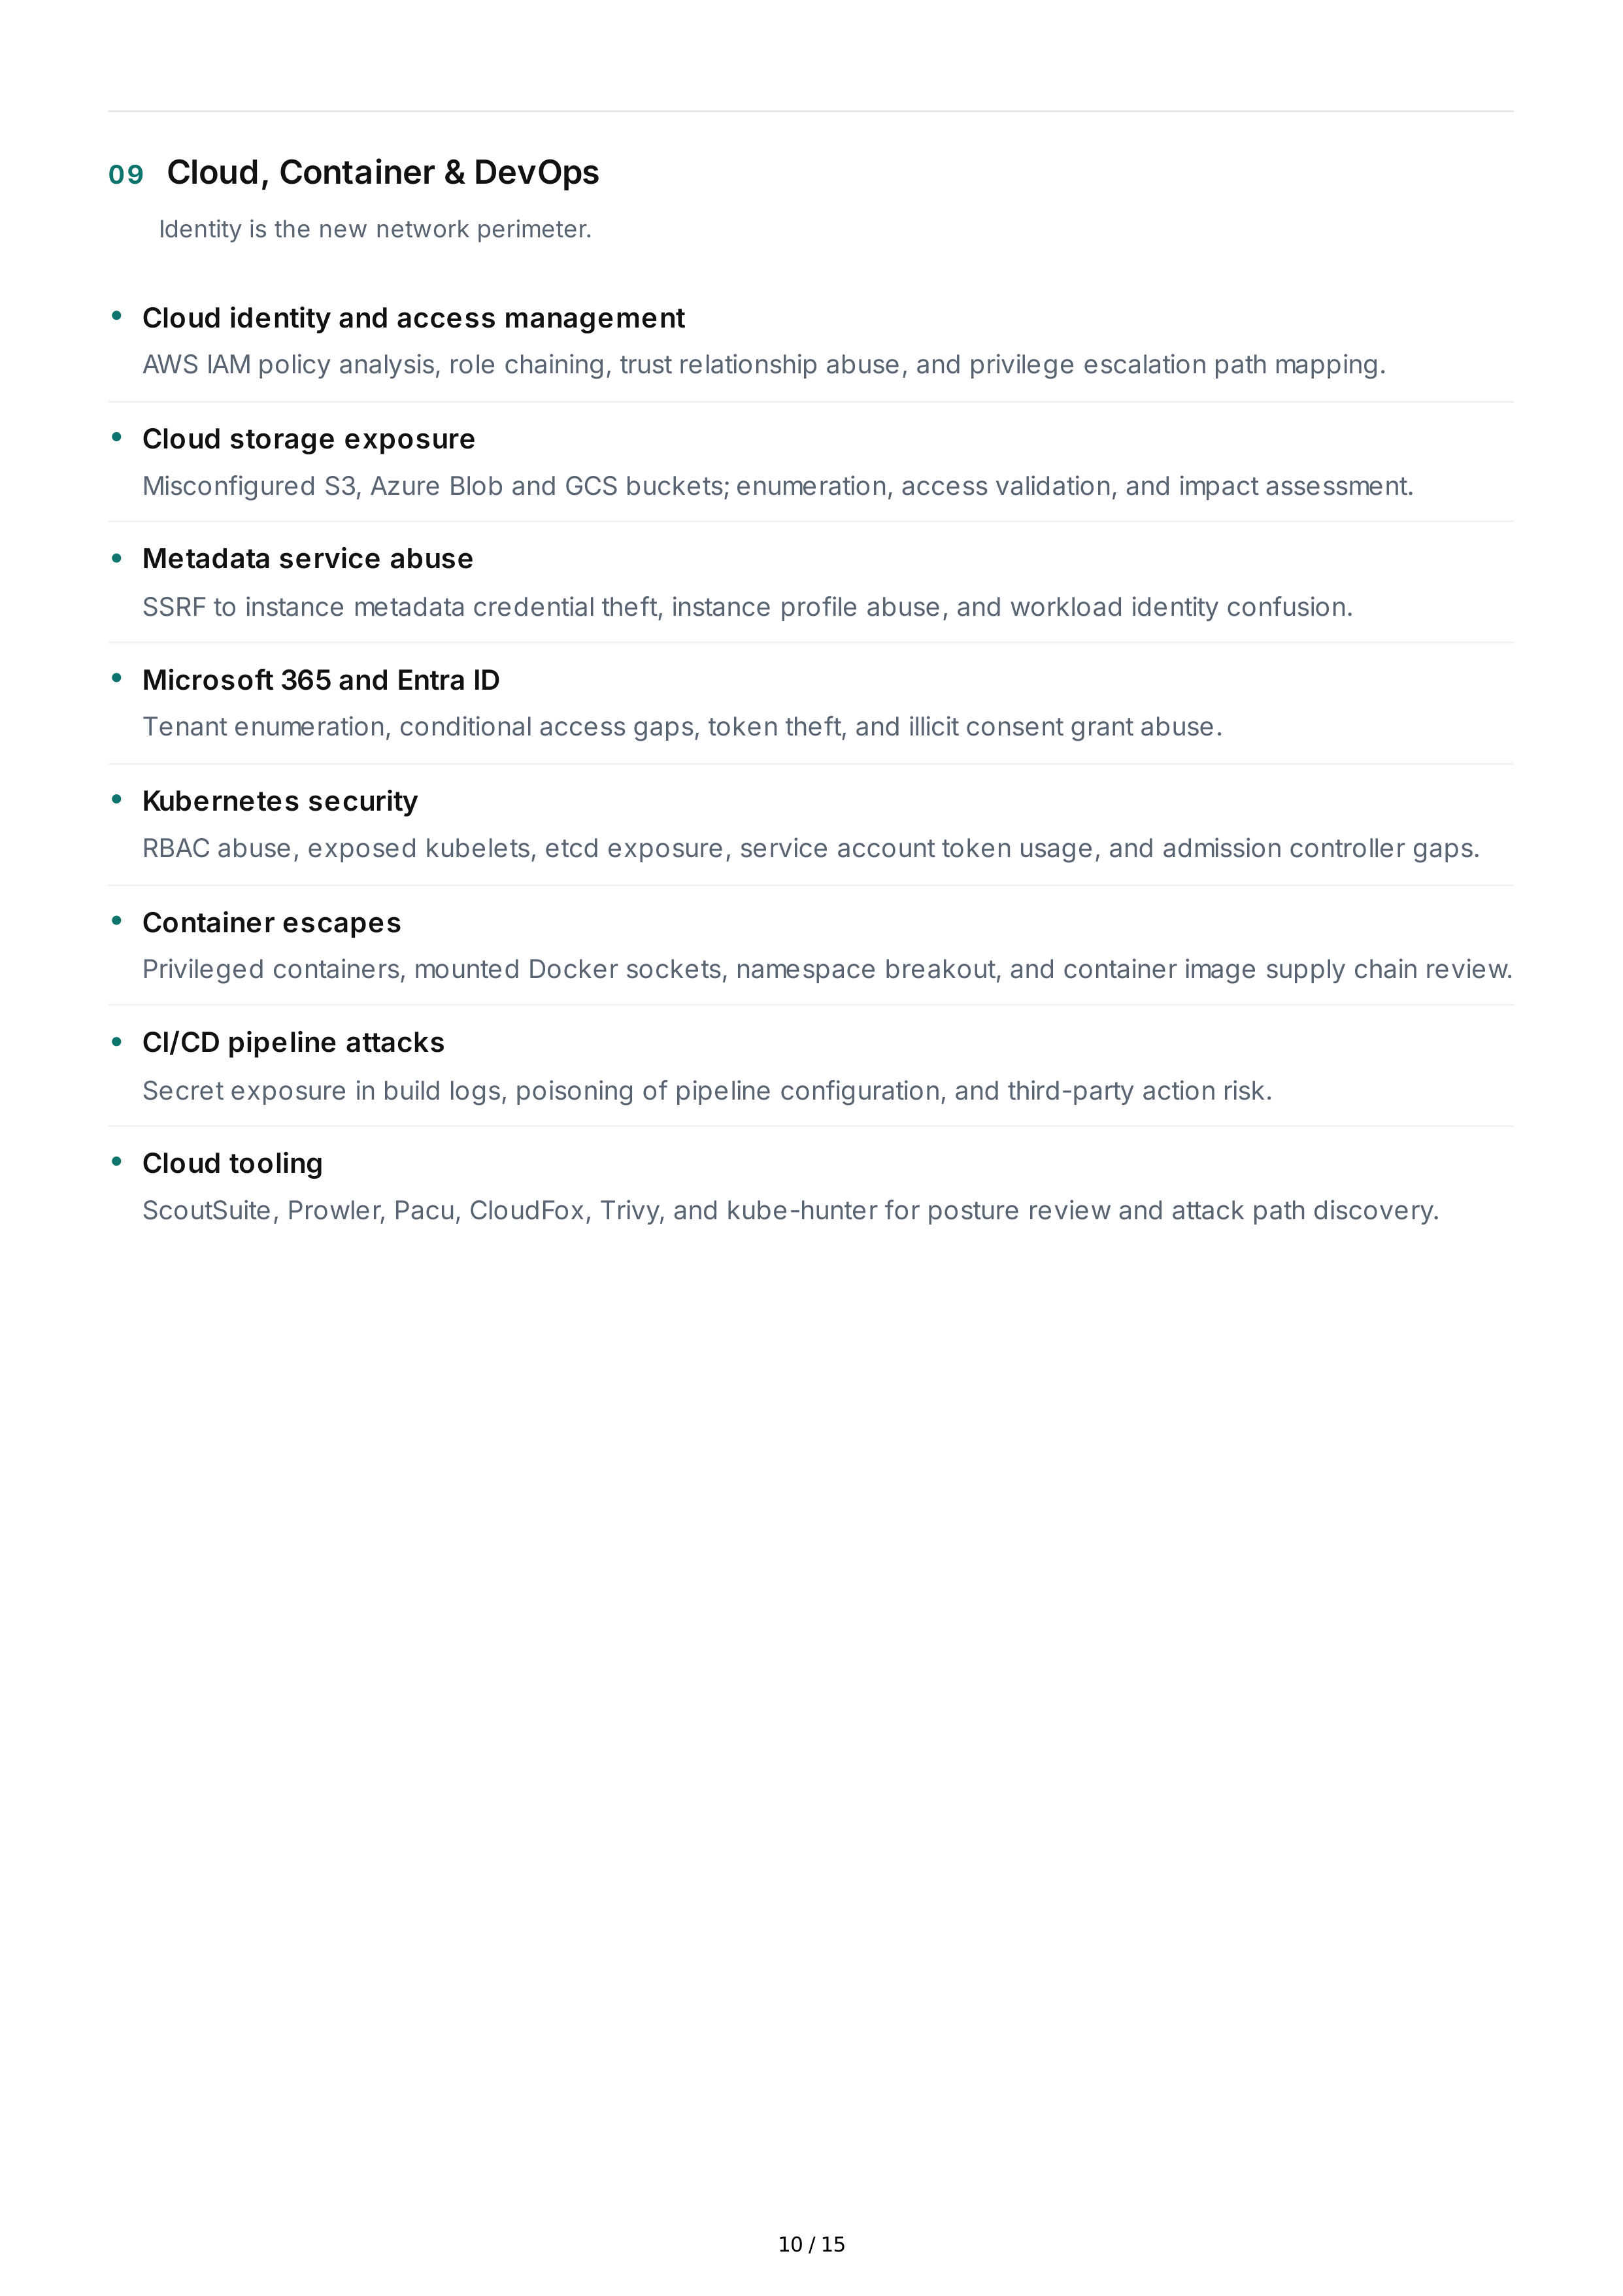
09
Cloud
,
Container
&
DevOps
Identity
is
the
new
network
perimeter
.
Cloud
identity
and
access
management
AWS
IAM
policy
analysis
,
role
chaining
,
trust
relationship
abuse
,
and
privilege
escalation
path
mapping
.
Cloud
storage
exposure
Misconfigured
S
3,
Azure
Blob
and
GCS
buckets
;
enumeration
,
access
validation
,
and
impact
assessment
.
Metadata
service
abuse
SSRF
to
instance
metadata
credential
theft
,
instance
profile
abuse
,
and
workload
identity
confusion
.
Microsoft
365
and
Entra
ID
Tenant
enumeration
,
conditional
access
gaps
,
token
theft
,
and
illicit
consent
grant
abuse
.
Kubernetes
security
RBAC
abuse
,
exposed
kubelets
,
etcd
exposure
,
service
account
token
usage
,
and
admission
controller
gaps
.
Container
escapes
Privileged
containers
,
mounted
Docker
sockets
,
namespace
breakout
,
and
container
image
supply
chain
review
.
CI
/
CD
pipeline
attacks
Secret
exposure
in
build
logs
,
poisoning
of
pipeline
configuration
,
and
third
-
party
action
risk
.
Cloud
tooling
ScoutSuite
,
Prowler
,
Pacu
,
CloudFox
,
Trivy
,
and
kube
-
hunter
for
posture
review
and
attack
path
discovery
.
10 / 15
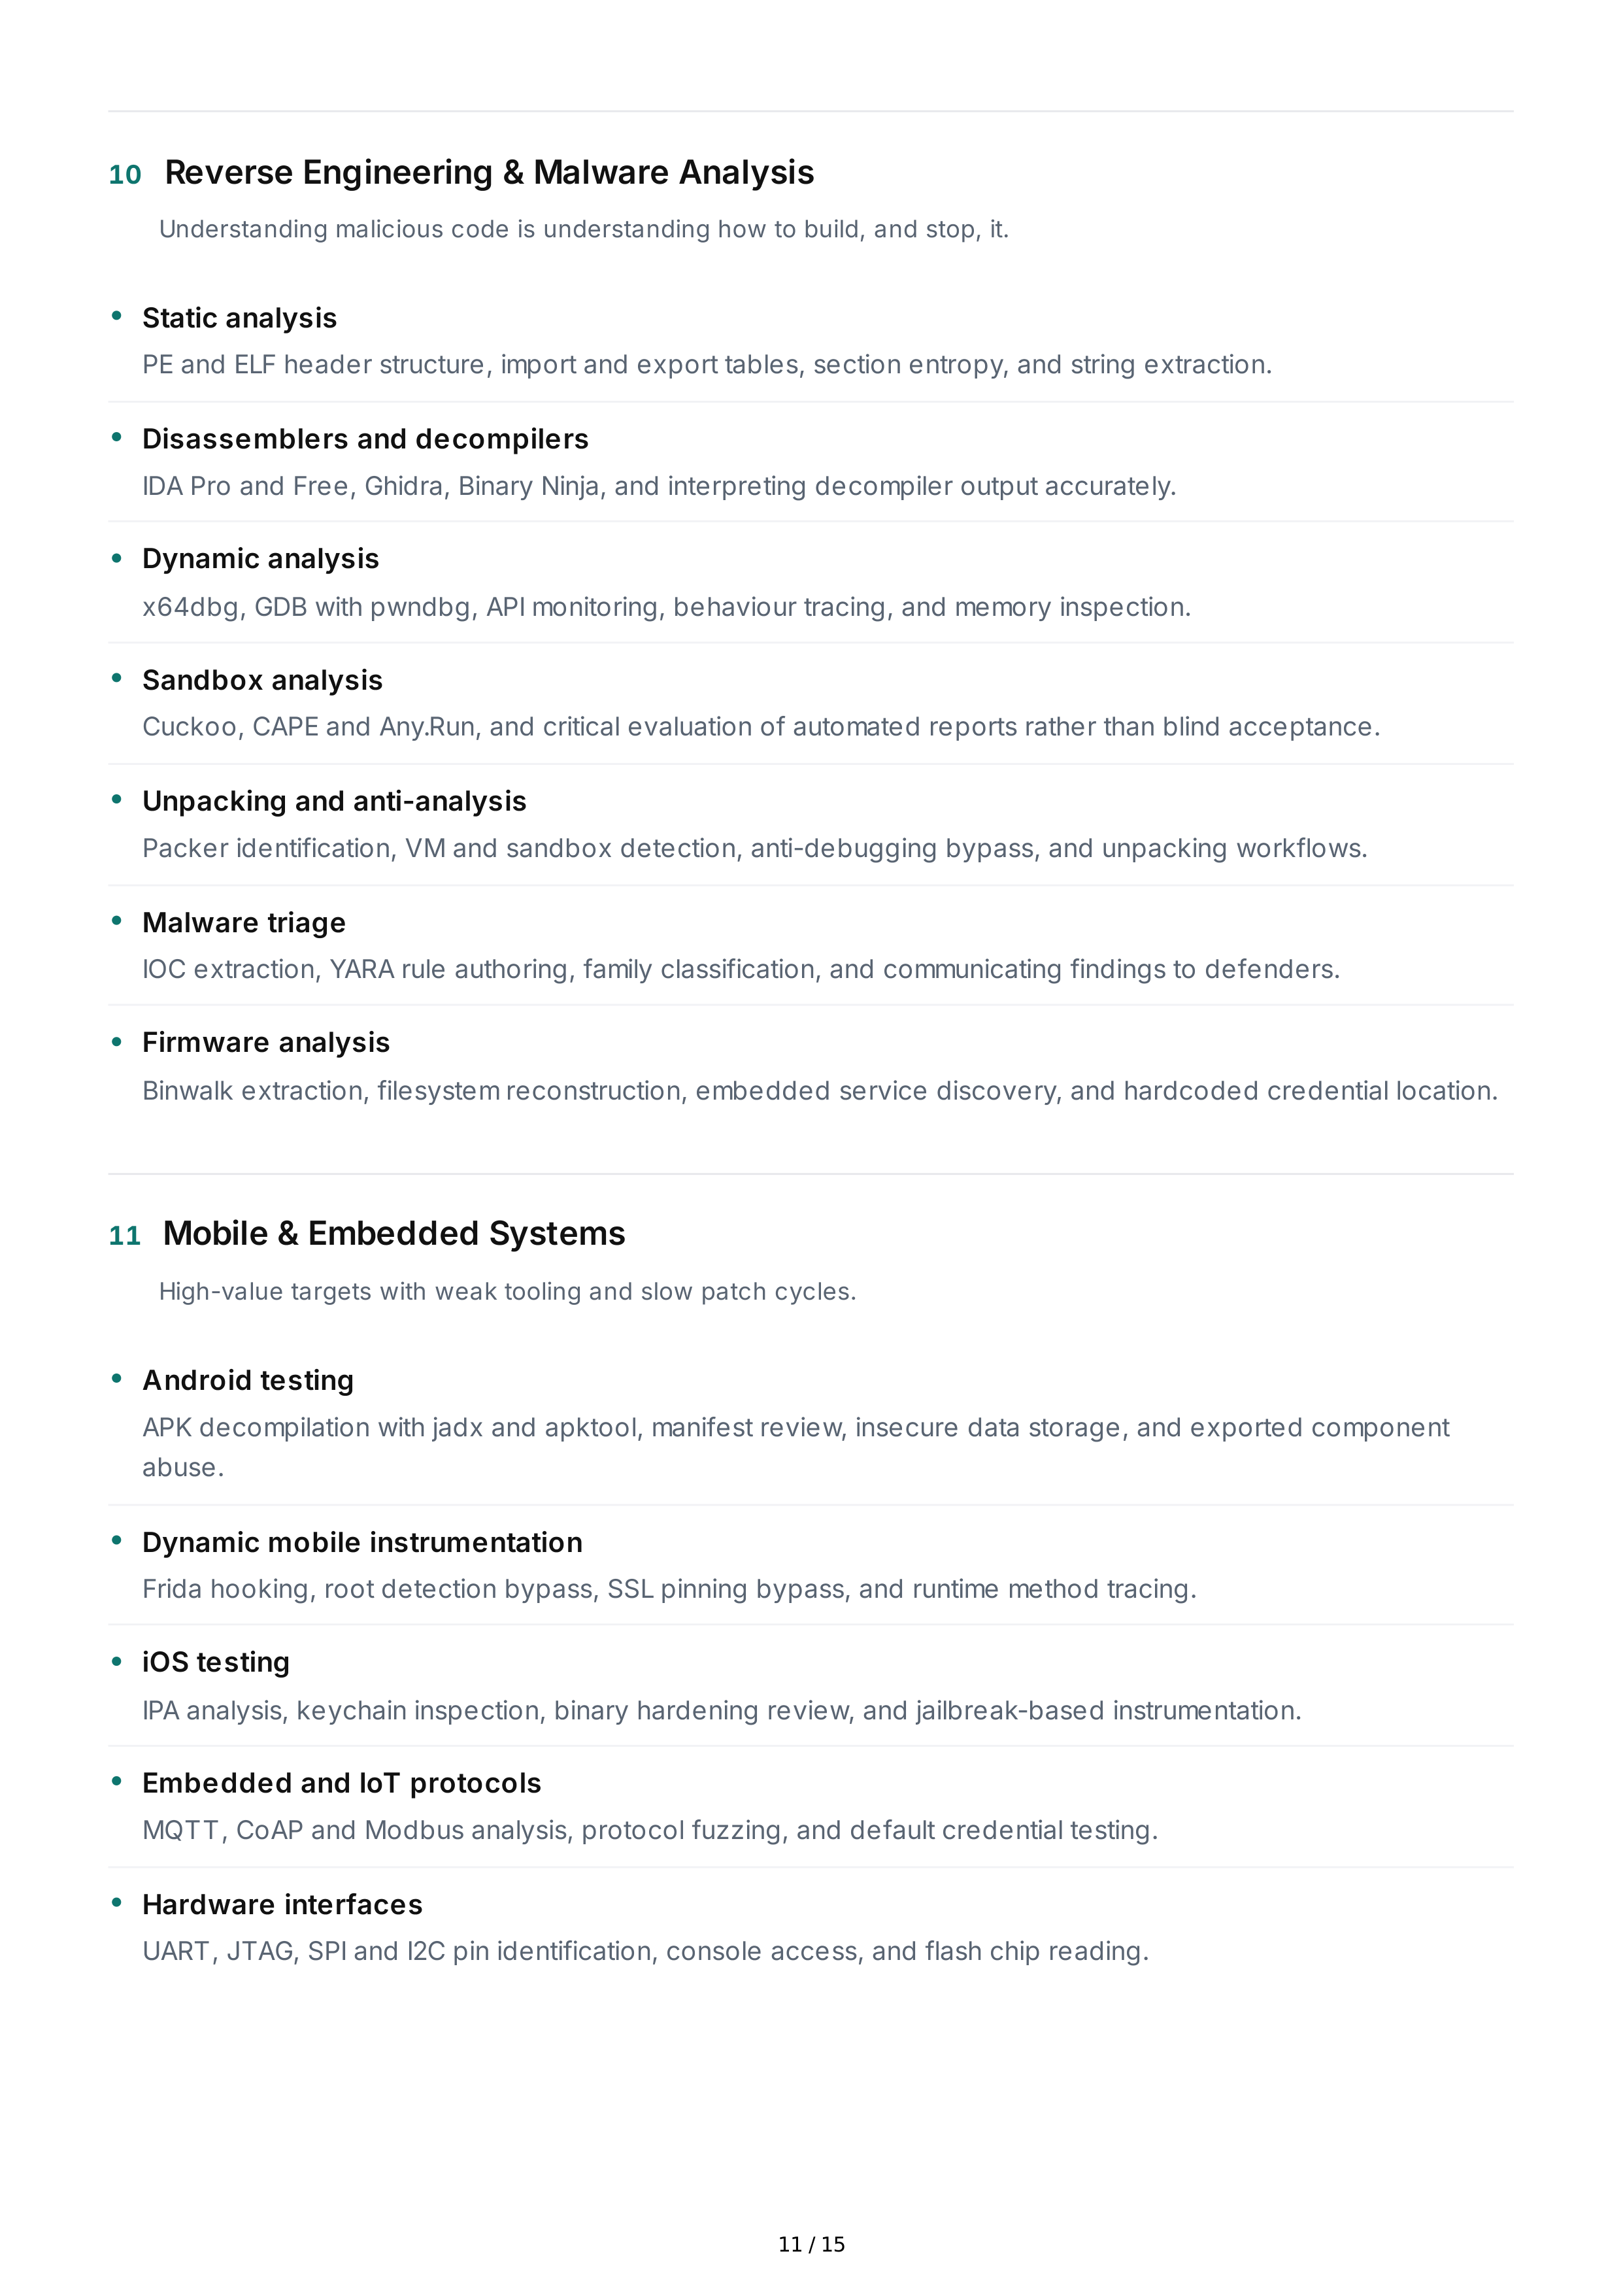
10
Reverse
Engineering
&
Malware
Analysis
Understanding
malicious
code
is
understanding
how
to
build
,
and
stop
,
it
.
11
Mobile
&
Embedded
Systems
High
-
value
targets
with
weak
tooling
and
slow
patch
cycles
.
Static
analysis
PE
and
ELF
header
structure
,
import
and
export
tables
,
section
entropy
,
and
string
extraction
.
Disassemblers
and
decompilers
IDA
Pro
and
Free
,
Ghidra
,
Binary
Ninja
,
and
interpreting
decompiler
output
accurately
.
Dynamic
analysis
x
64
dbg
,
GDB
with
pwndbg
,
API
monitoring
,
behaviour
tracing
,
and
memory
inspection
.
Sandbox
analysis
Cuckoo
,
CAPE
and
Any
.
Run
,
and
critical
evaluation
of
automated
reports
rather
than
blind
acceptance
.
Unpacking
and
anti
-
analysis
Packer
identification
,
VM
and
sandbox
detection
,
anti
-
debugging
bypass
,
and
unpacking
workflows
.
Malware
triage
IOC
extraction
,
YARA
rule
authoring
,
family
classification
,
and
communicating
findings
to
defenders
.
Firmware
analysis
Binwalk
extraction
,
filesystem
reconstruction
,
embedded
service
discovery
,
and
hardcoded
credential
location
.
Android
testing
APK
decompilation
with
jadx
and
apktool
,
manifest
review
,
insecure
data
storage
,
and
exported
component
abuse
.
Dynamic
mobile
instrumentation
Frida
hooking
,
root
detection
bypass
,
SSL
pinning
bypass
,
and
runtime
method
tracing
.
iOS
testing
IPA
analysis
,
keychain
inspection
,
binary
hardening
review
,
and
jailbreak
-
based
instrumentation
.
Embedded
and
IoT
protocols
MQTT
,
CoAP
and
Modbus
analysis
,
protocol
fuzzing
,
and
default
credential
testing
.
Hardware
interfaces
UART
,
JTAG
,
SPI
and
I
2
C
pin
identification
,
console
access
,
and
flash
chip
reading
.
11 / 15
12
Red
Team
Operations
Goal
-
oriented
,
adversary
-
emulating
work
rather
than
scan
-
and
-
report
.
Engagement
planning
Scoping
,
rules
of
engagement
,
deconfliction
procedures
,
and
defining
measurable
objectives
with
the
client
.
Threat
modelling
and
adversary
emulation
MITRE
ATT
&
CK
mapping
,
threat
actor
selection
,
and
realistic
scenario
design
.
Infrastructure
build
Redirectors
,
domain
categorisation
,
phishing
infrastructure
,
TLS
configuration
,
and
long
-
haul
operational
resilience
.
Operator
OPSEC
Infrastructure
separation
,
logging
discipline
,
artefact
hygiene
,
and
attribution
reduction
.
Social
engineering
campaigns
Phishing
,
pretexting
,
vishing
,
and
payload
delivery
design
with
measured
,
ethical
boundaries
.
Assumed
-
breach
testing
Starting
from
a
defined
foothold
and
pursuing
named
objectives
across
the
internal
estate
.
Purple
team
collaboration
Detection
engineering
feedback
loops
,
control
validation
,
and
joint
tuning
with
the
blue
team
.
12 / 15
13
Governance
,
Reporting
&
Professional
Practice
An
unreported
finding
is
an
unfixed
finding
.
Vulnerability
scoring
CVSS
v
3.1
and
v
4.0
vectors
,
contextual
risk
rating
,
and
business
impact
framing
.
Technical
report
writing
Clear
findings
,
reproducible
steps
,
sanitised
evidence
,
and
specific
remediation
guidance
.
Executive
communication
Translating
technical
risk
into
business
language
for
non
-
technical
stakeholders
and
boards
.
Framework
familiarity
PTES
,
the
OWASP
Testing
Guide
,
NIST
SP
800-115,
and
MITRE
ATT
&
CK
.
Compliance
context
PCI
DSS
,
ISO
27001,
SOC
2,
and
data
protection
obligations
when
handling
client
systems
and
evidence
.
Legal
and
ethical
boundaries
Written
authorisation
,
strict
scope
adherence
,
safe
data
handling
,
and
responsible
disclosure
.
Retesting
and
remediation
validation
Verifying
fixes
without
regressing
production
systems
,
and
documenting
residual
risk
.
13 / 15
14
Toolchain
Reference
Tools
change
;
the
underlying
technique
does
not
.
This
maps
the
standard
working
set
by
category
.
COMMON
T OOLS
BY
ENGAGEMENT
PHASE
CAT EGORY
REPRESENTAT IVE
T OOLS
Recon
&
OSINT
Amass
,
Subfinder
,
theHarvester
,
Shodan
,
Maltego
,
Recon
-
ng
Scanning
&
enumeration
Nmap
,
Masscan
,
Nessus
,
Nuclei
,
Gobuster
,
Enum
4
linux
Web
exploitation
Burp
Suite
Professional
,
OWASP
ZAP
,
sqlmap
,
ffuf
,
Caido
Exploitation
Metasploit
,
SearchSploit
,
pwntools
,
BeEF
,
ysoserial
Credential
attacks
Hashcat
,
John
the
Ripper
,
Hydra
,
Responder
,
Impacket
Active
Directory
BloodHound
,
SharpHound
,
Mimikatz
,
Rubeus
,
Certipy
Post
-
exploitation
&
C
2
Cobalt
Strike
,
Sliver
,
Mythic
,
Empire
,
Chisel
Wireless
&
RF
Aircrack
-
ng
,
Kismet
,
Wifite
,
Proxmark
3,
GNU
Radio
Cloud
&
containers
ScoutSuite
,
Prowler
,
Pacu
,
Trivy
,
kube
-
hunter
Reverse
engineering
Ghidra
,
IDA
Pro
,
x
64
dbg
,
Frida
,
dnSpy
Network
analysis
Wireshark
,
tcpdump
,
Bettercap
,
Zeek
,
tshark
15
Proficiency
Tiers
The
same
skill
list
maps
onto
four
levels
.
Hiring
and
certification
decisions
usually
hinge
on
which
tier
a
candidate
can
evidence
.
EXPECT ED
DEPT H
BY
LEVEL
T IER
WHAT
IT
LOOKS
LIKE
REPRESENTAT IVE
SKILLS
Foundational
Comfort
at
the
command
line
,
understands
how
protocols
behave
,
can
follow
a
documented
methodology
.
TCP
/
IP
,
Linux
and
Windows
CLI
,
Nmap
,
Wireshark
basics
,
OWASP
Top
10
theory
Intermediate
Runs
web
application
tests
unaided
,
reproduces
common
findings
,
scripts
repetitive
work
.
Burp
Suite
,
common
privilege
escalation
,
Metasploit
,
Python
and
Bash
tooling
,
basic
AD
enumeration
Advanced
Chains
multiple
weaknesses
into
a
business
-
impacting
outcome
and
evades
modern
controls
.
AD
attack
chains
,
custom
exploit
development
,
EDR
evasion
,
cloud
attack
paths
,
C
2
infrastructure
Expert
Produces
original
research
or
tooling
,
leads
engagements
,
and
improves
defensive
capability
.
Novel
exploit
research
,
tool
authoring
,
red
team
leadership
,
detection
engineering
collaboration
14 / 15
16
Certification
Alignment
Where
the
skills
above
are
formally
assessed
.
OSCP
Offensive
Security
Certified
Professional
—
practical
exam
covering
exploitation
,
Active
Directory
and
reporting
.
PNPT
Practical
Network
Penetration
Tester
—
AD
-
focused
with
a
live
client
debrief
component
.
CPTS
Certified
Penetration
Testing
Specialist
—
broad
network
,
web
and
cloud
curriculum
with
exam
.
CRTO
Certified
Red
Team
Operations
—
Cobalt
Strike
tradecraft
and
red
team
infrastructure
.
OSWE
Offensive
Security
Web
Expert
—
white
-
box
source
code
review
and
web
exploitation
.
OSEP
Experienced
Penetration
Tester
—
evasion
,
Active
Directory
and
client
-
side
attack
chains
.
GPEN
GIAC
Penetration
Tester
—
vendor
certification
aligned
to
the
SANS
SEC
560
curriculum
.
CEH
Certified
Ethical
Hacker
—
foundational
theory
and
tooling
overview
for
newcomers
.
15 / 15