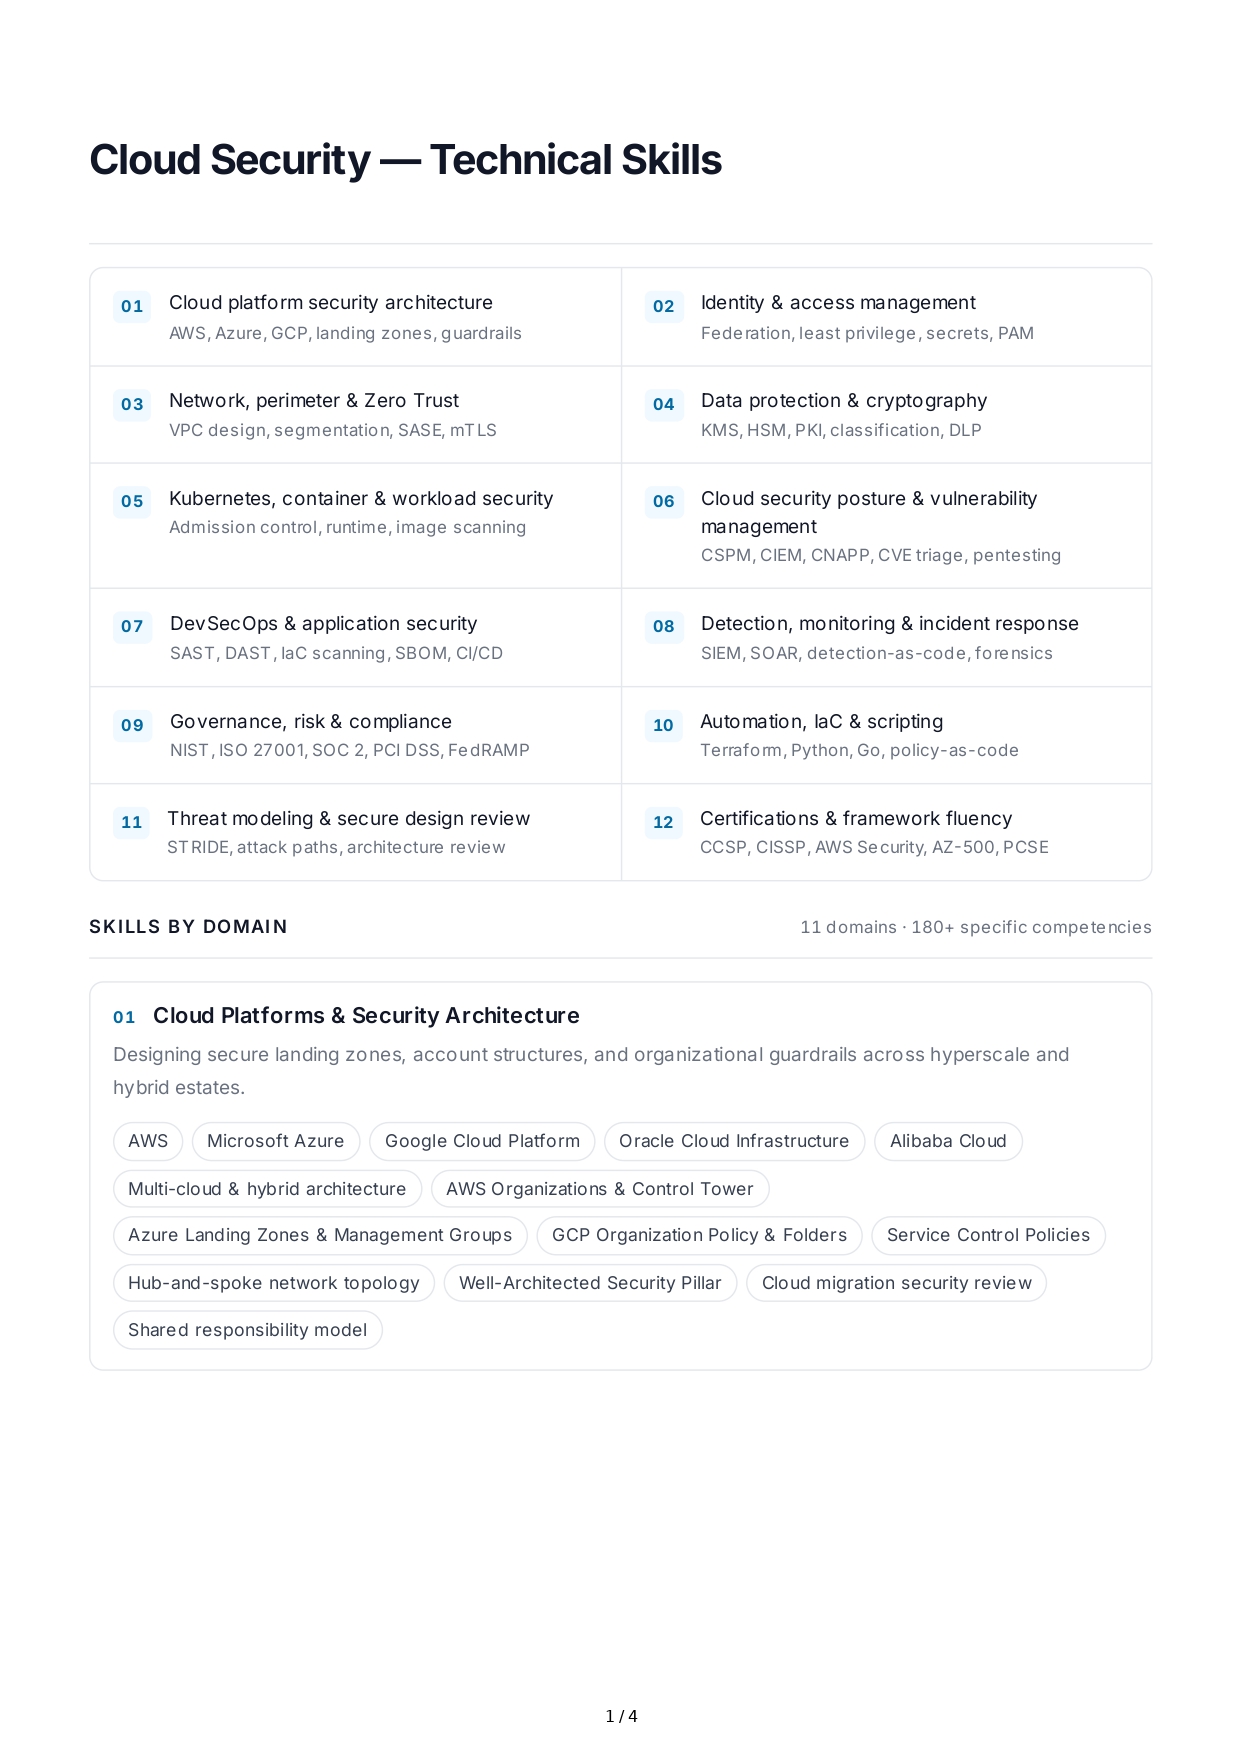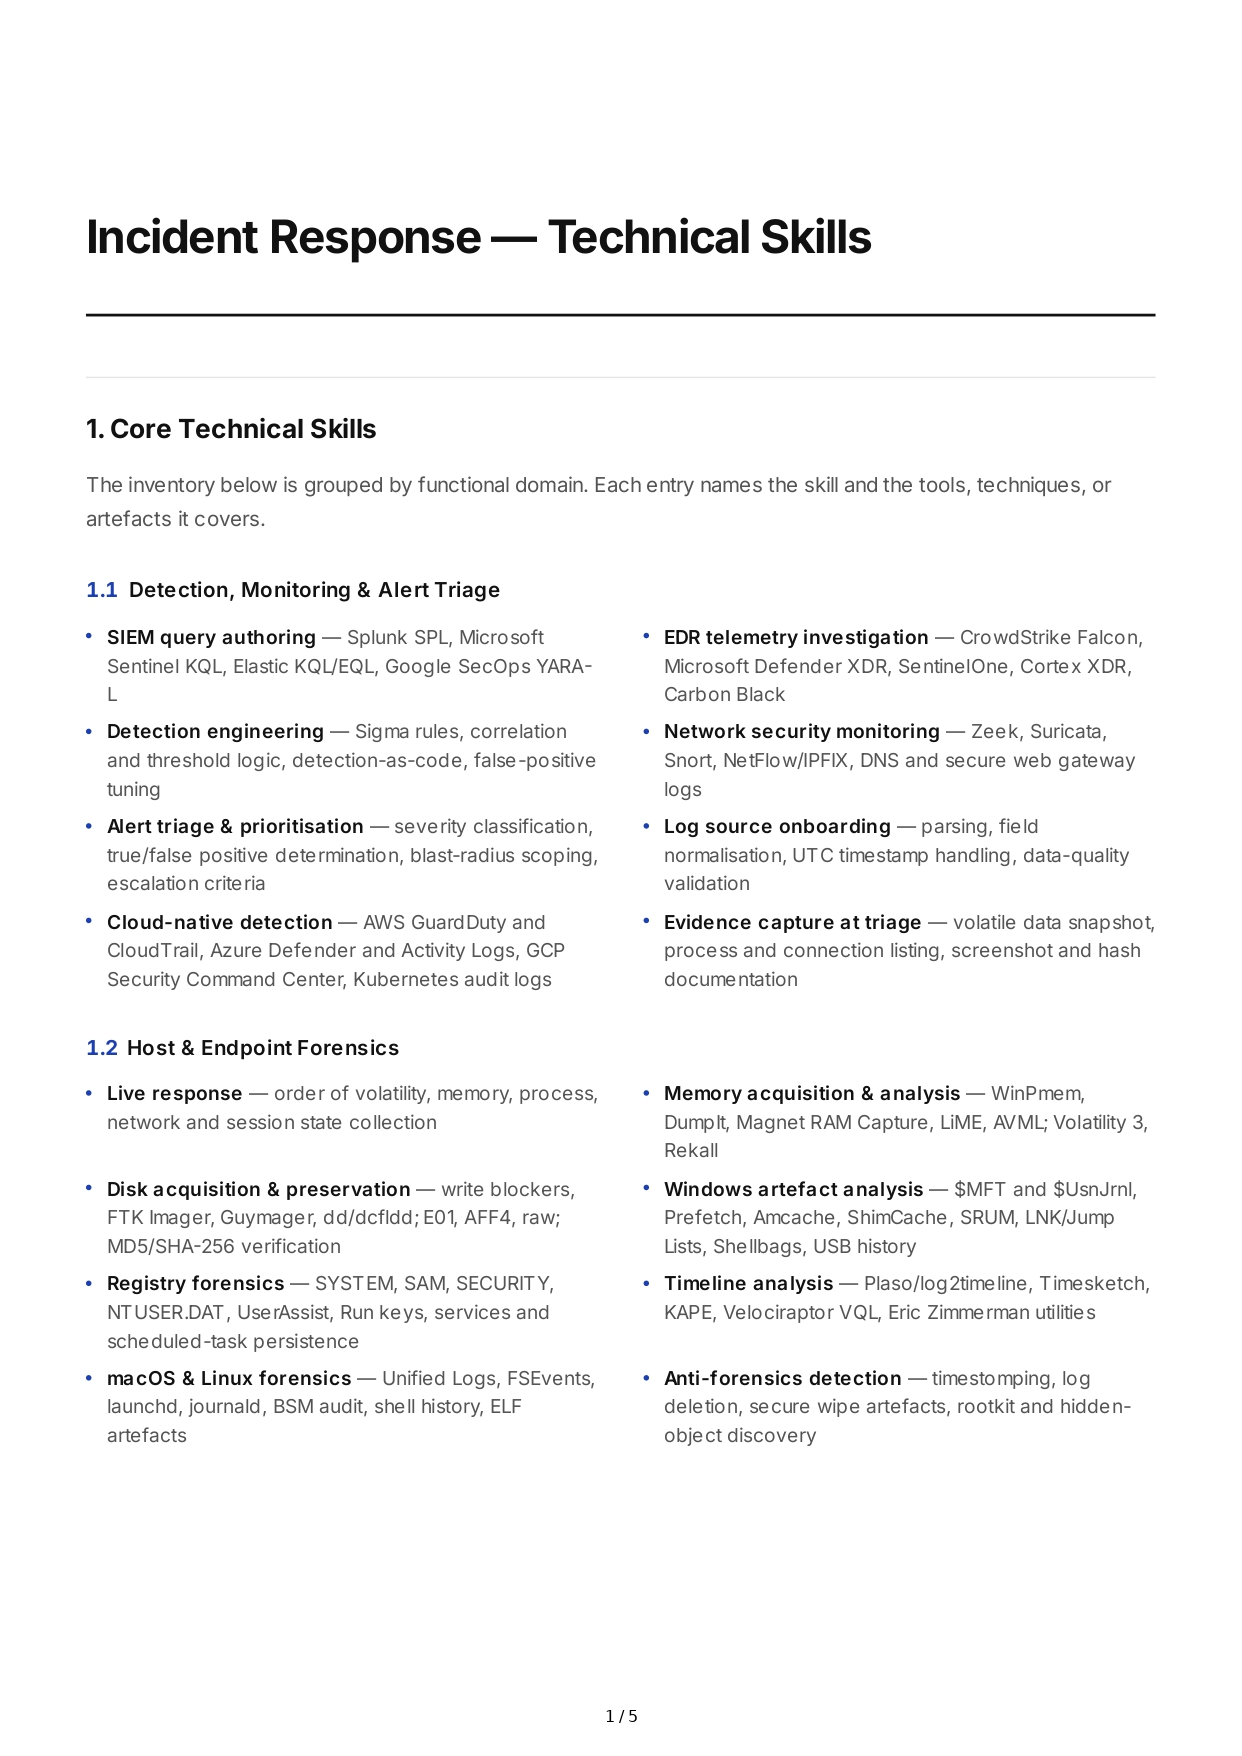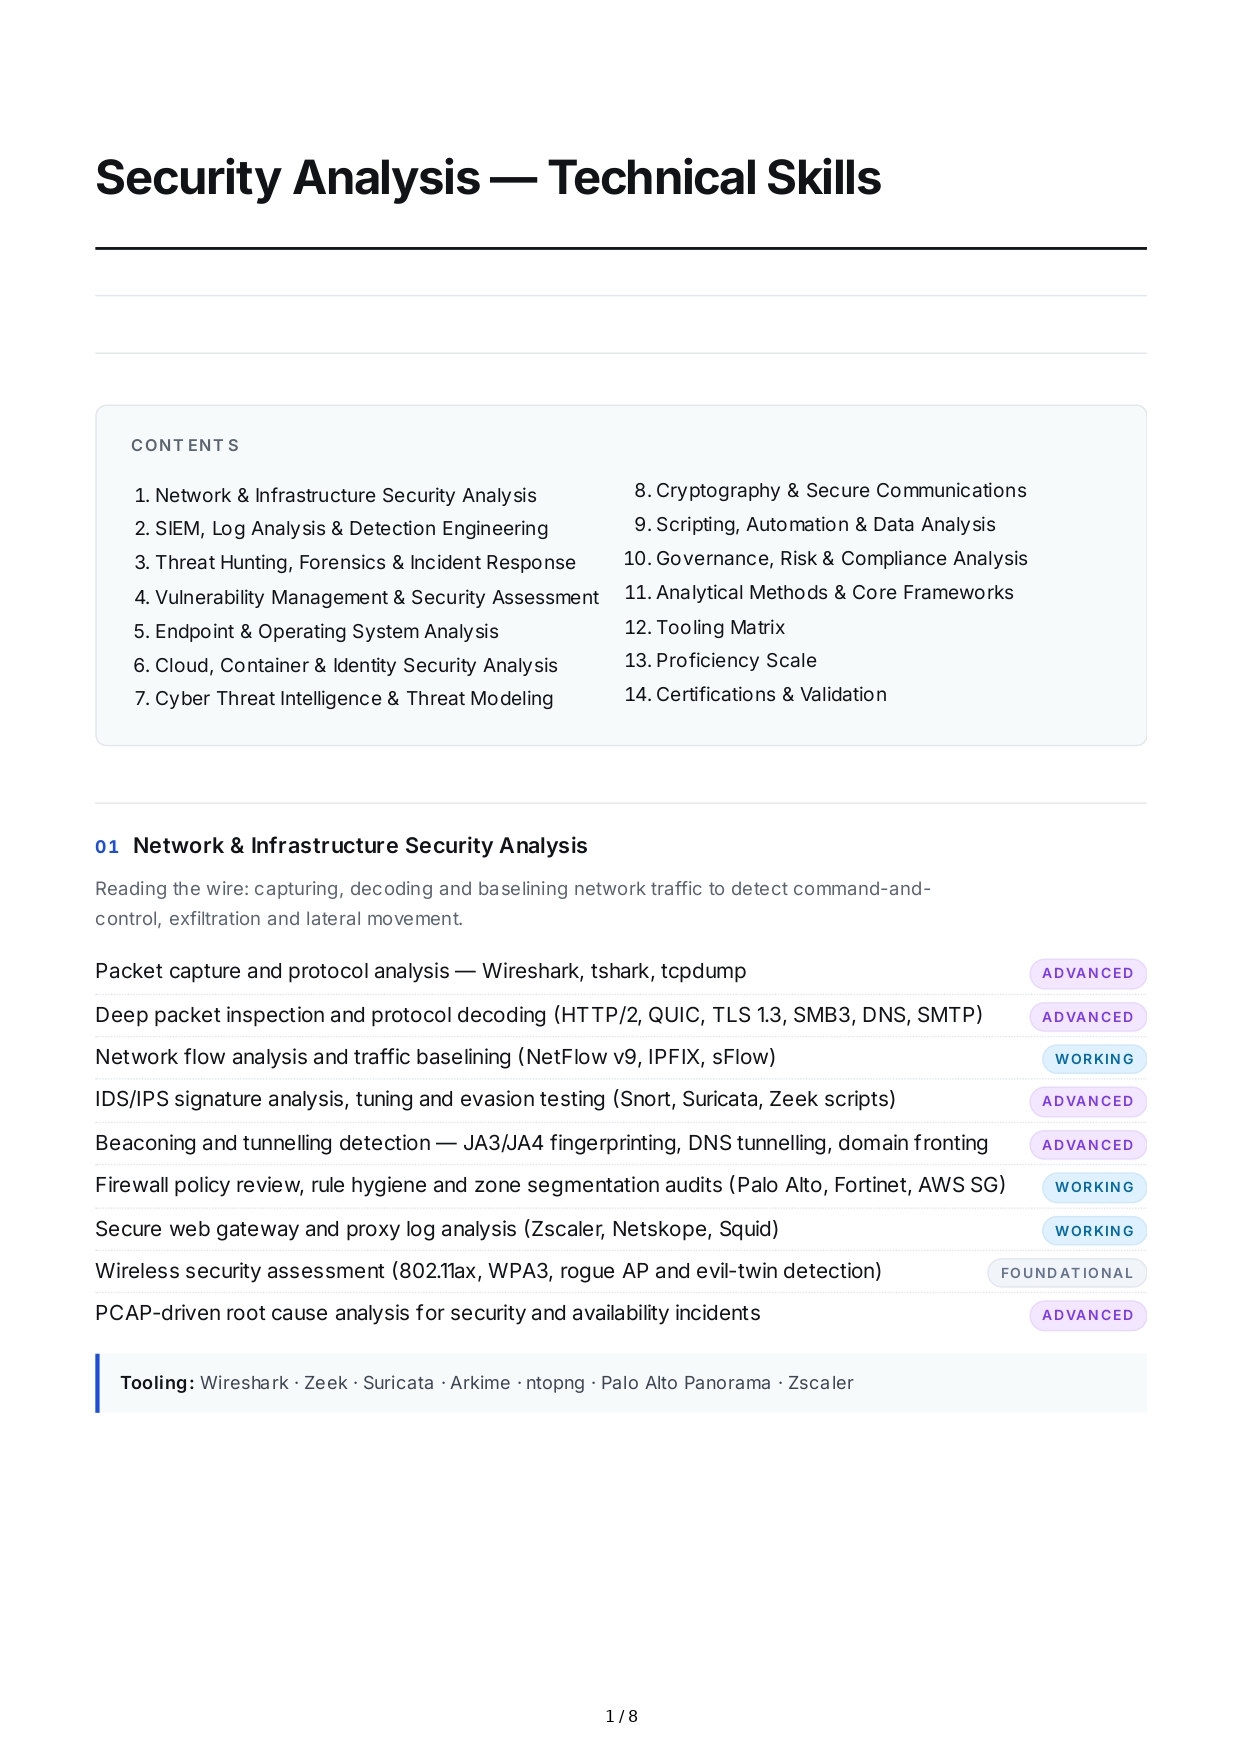
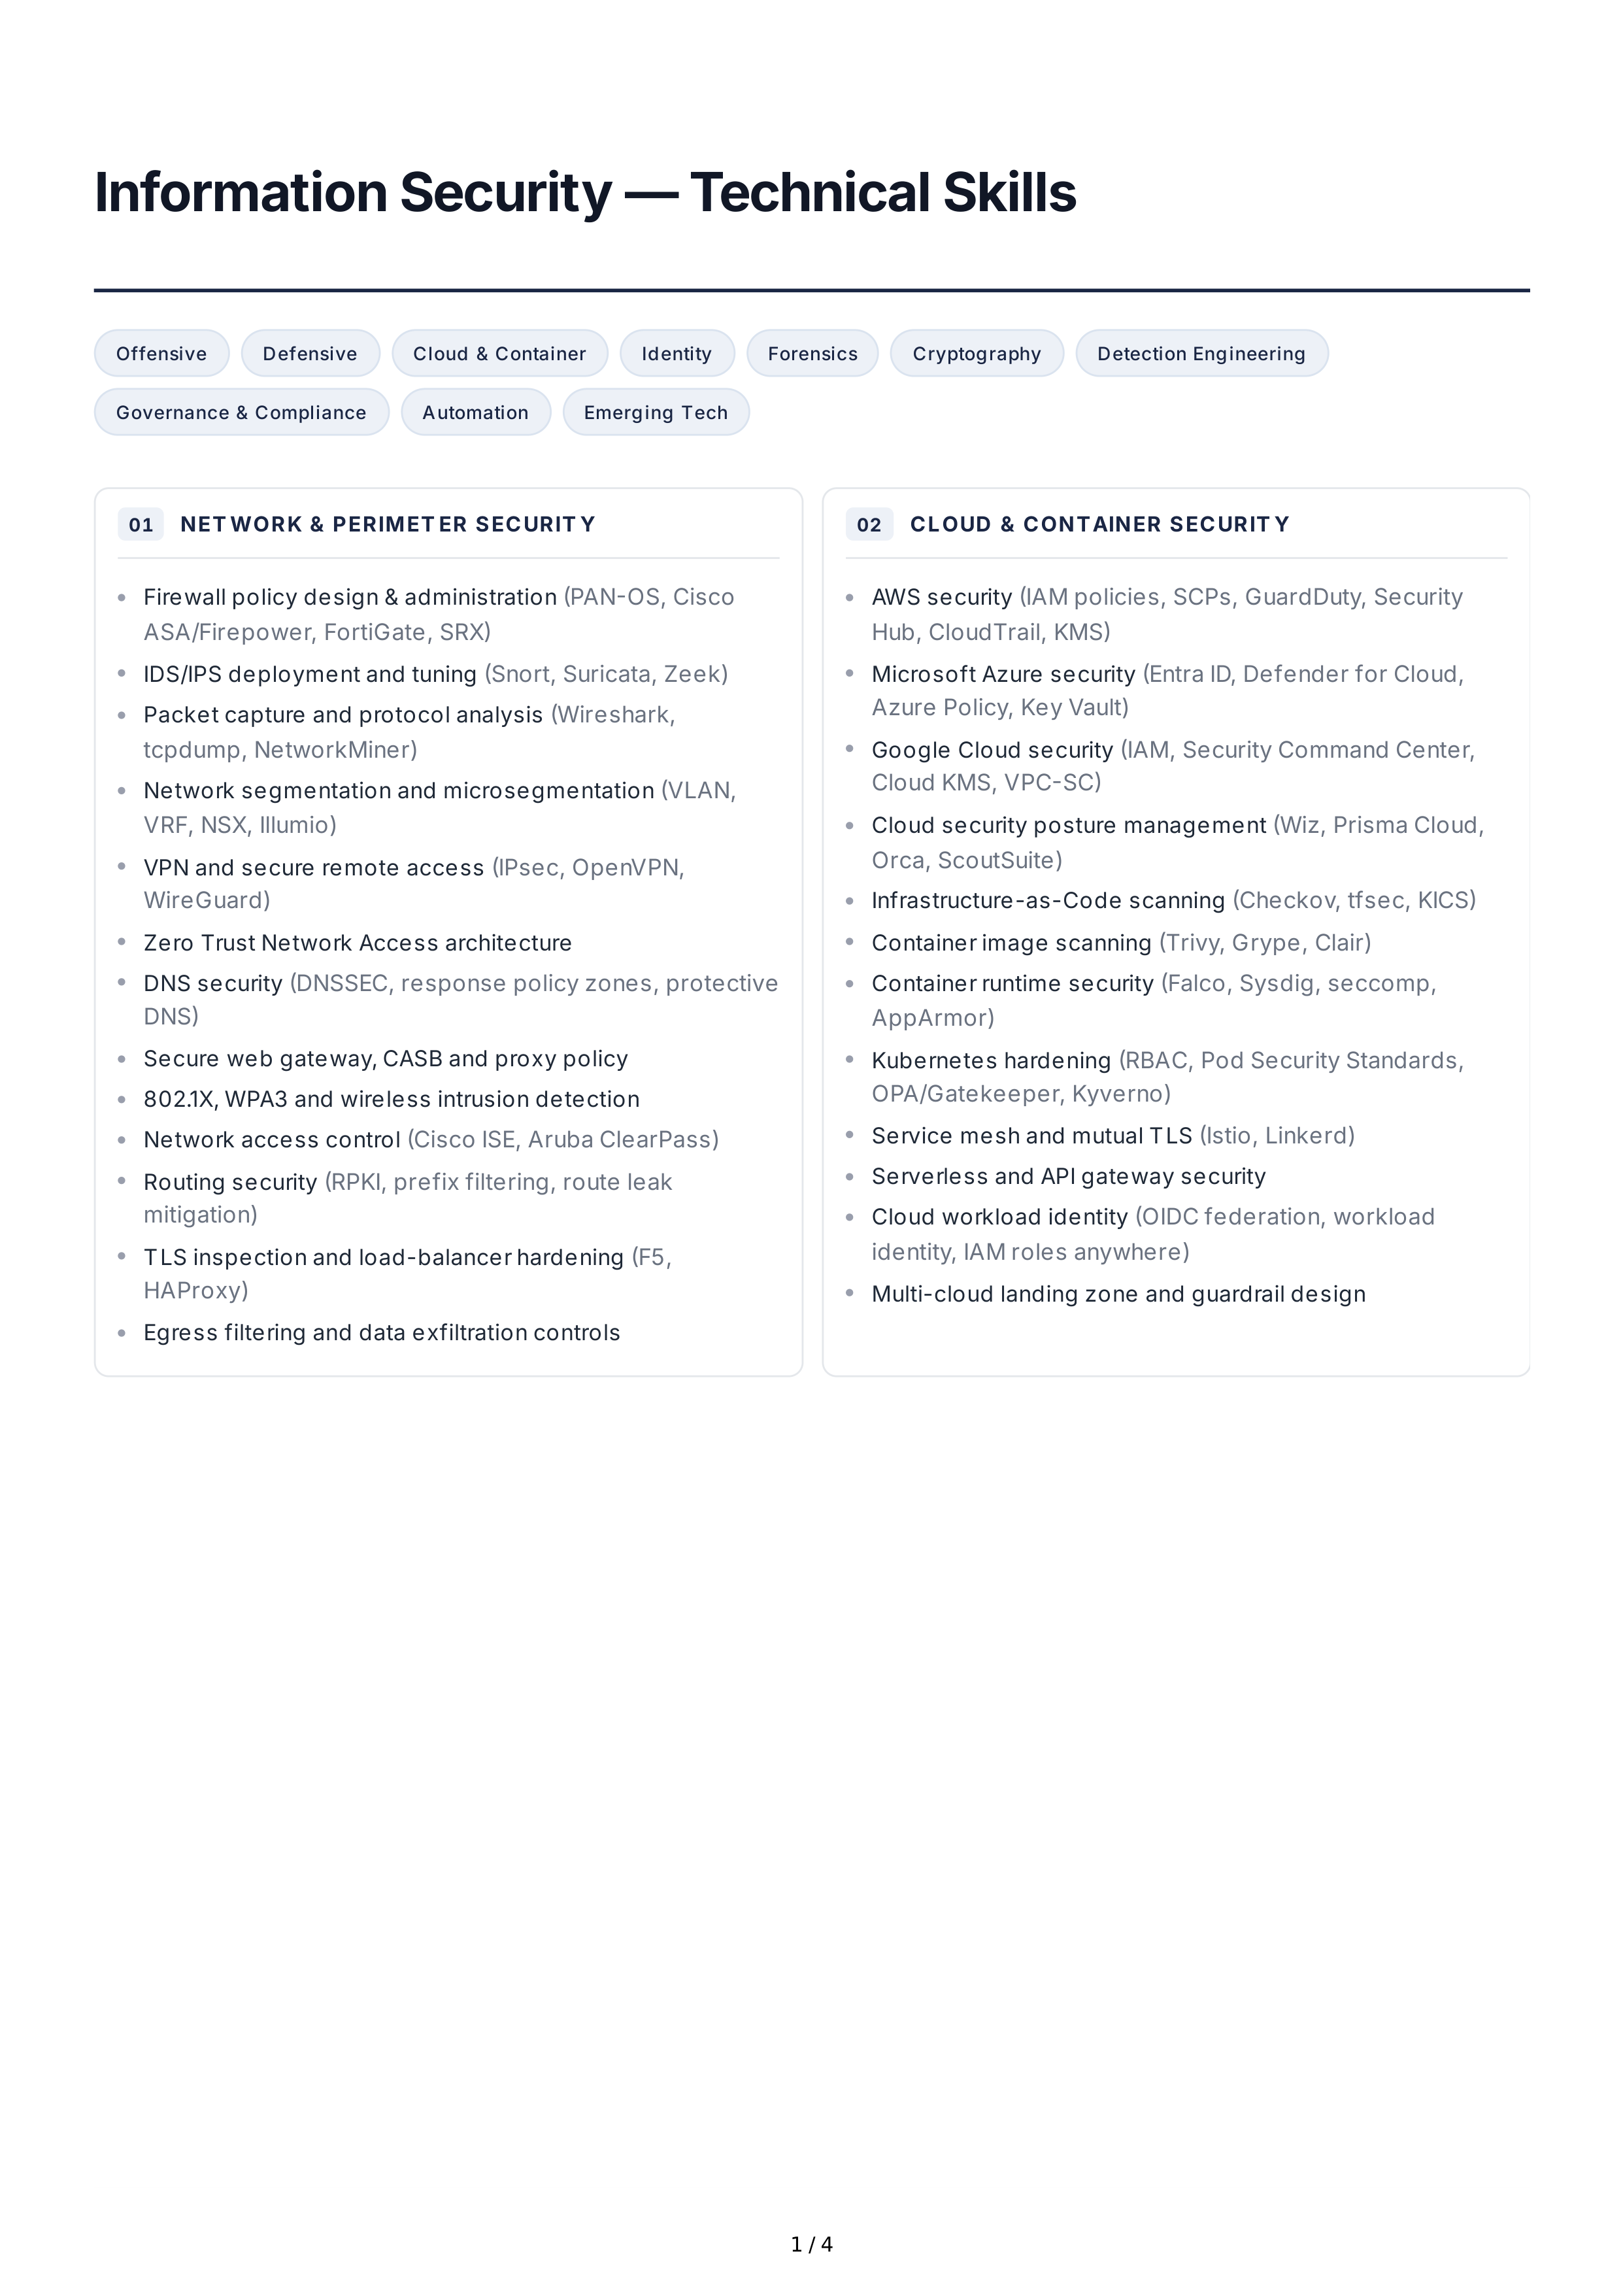
Information
Security
—
Technical
Skills
Offensive
Defensive
Cloud
&
Container
Identity
Forensics
Cryptography
Detection
Engineering
Governance
&
Compliance
Automation
Emerging
Tech
01
NET WORK
&
PERIMET ER
SECURIT Y
02
CLOUD
&
CONTAINER
SECURIT Y
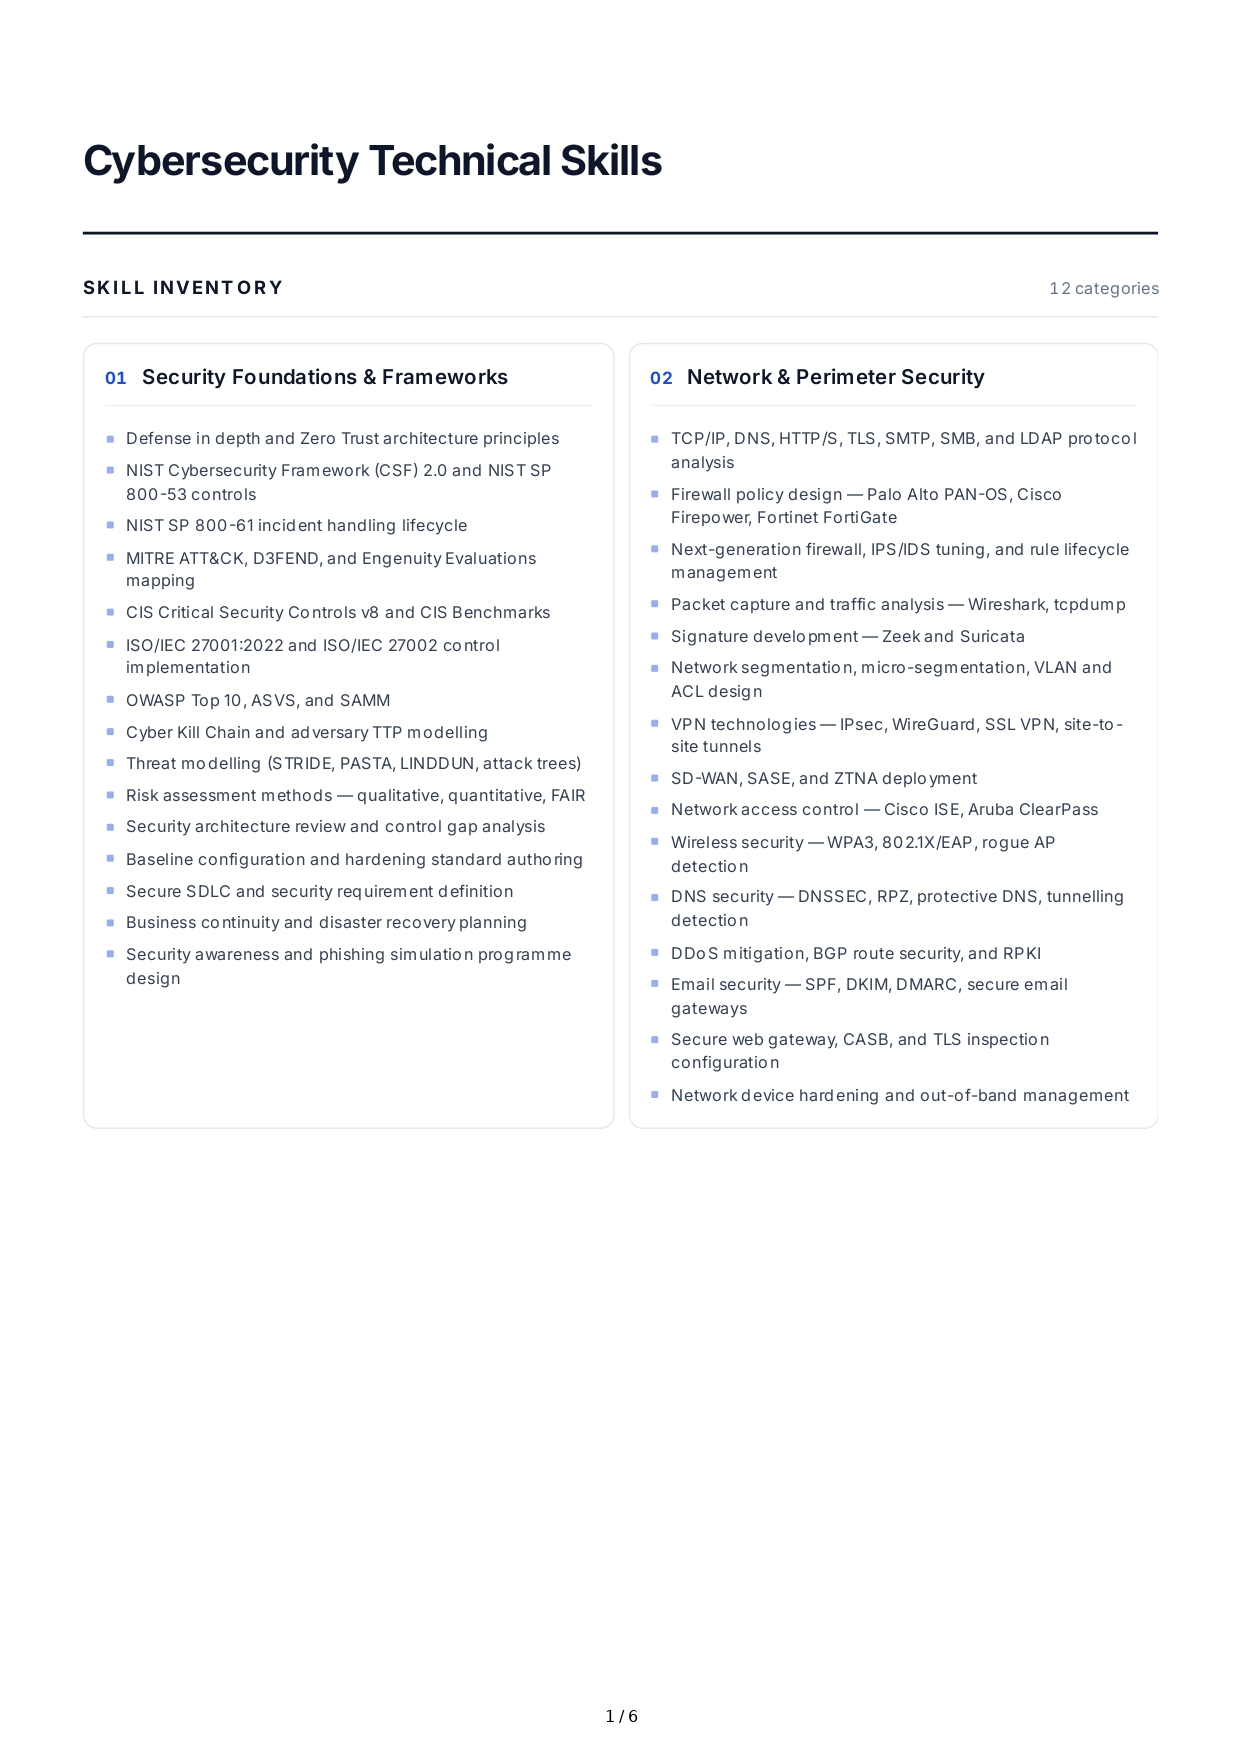
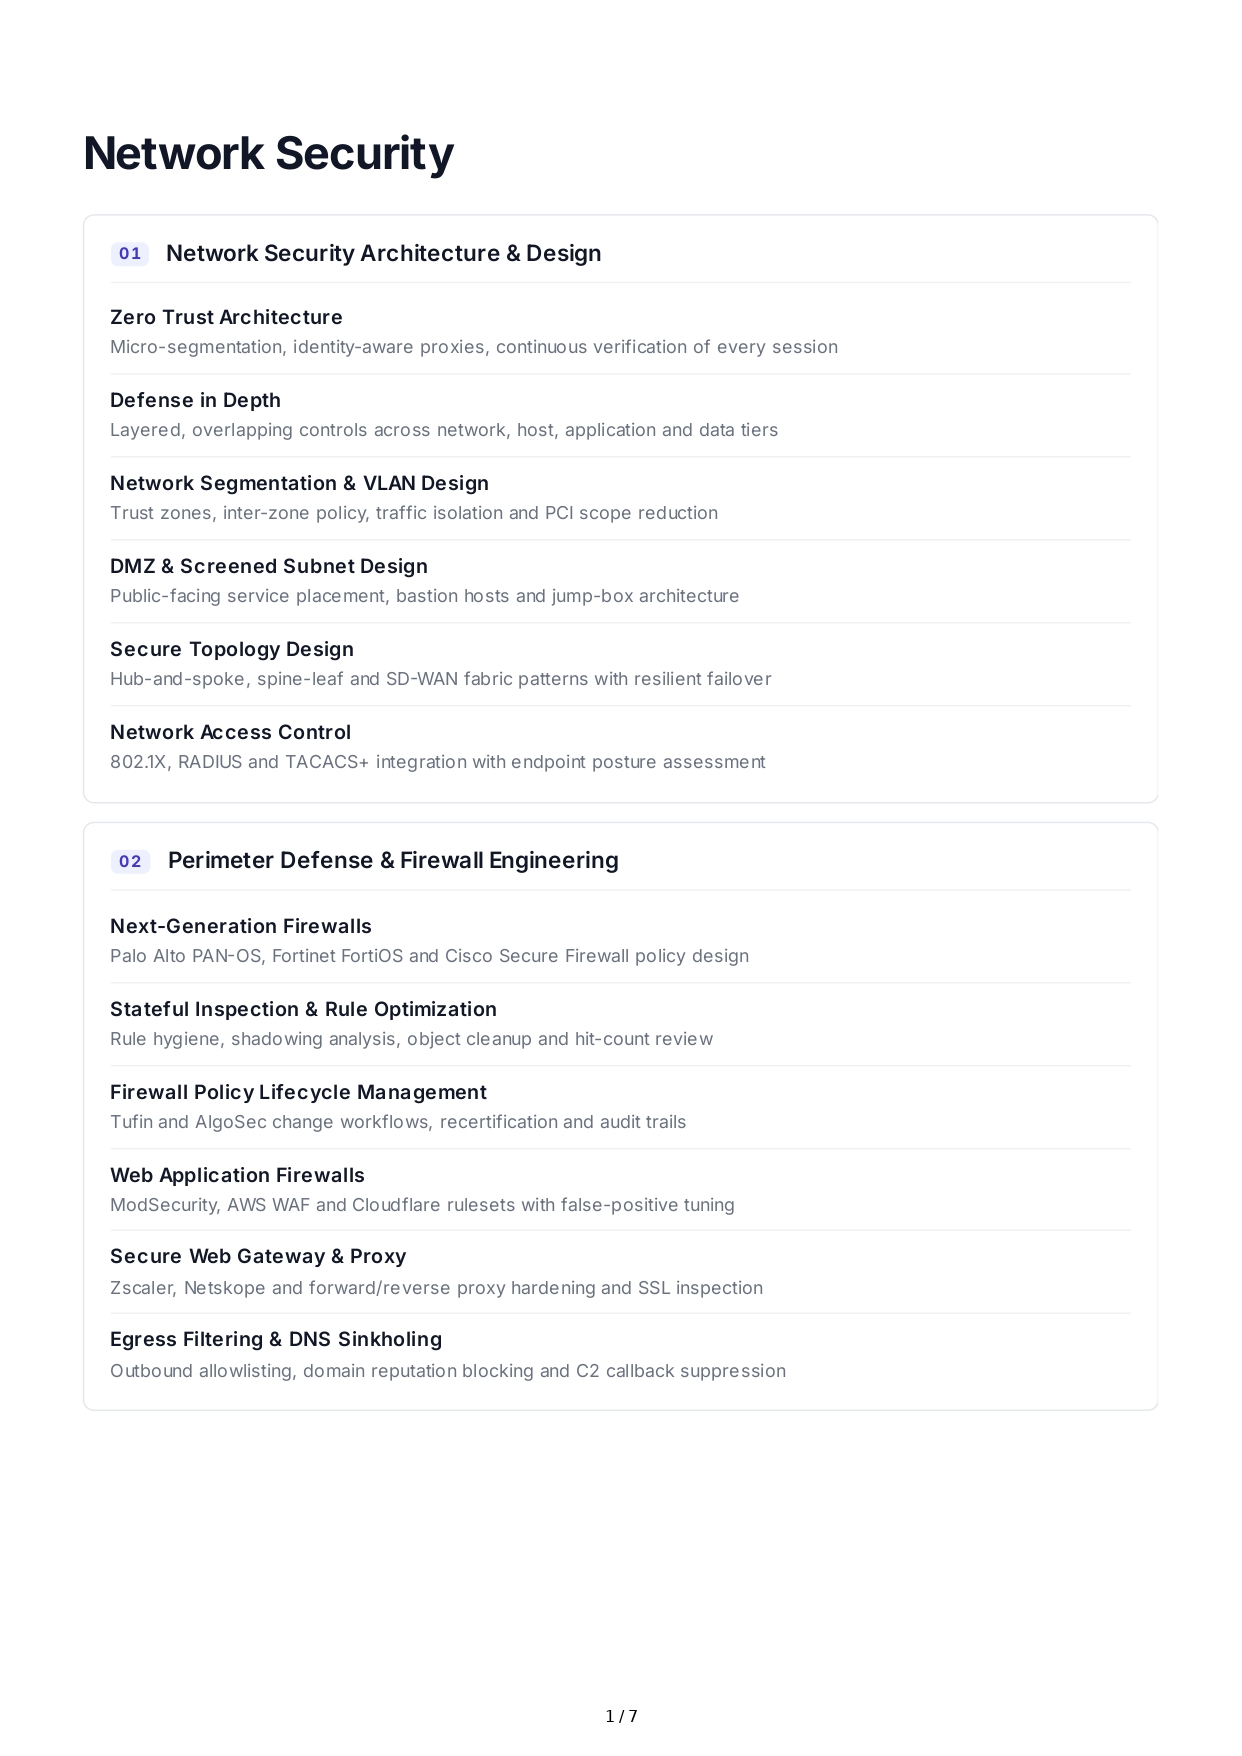
Firewall
policy
design
&
administration
(
PAN
-
OS
,
Cisco
ASA
/
Firepower
,
FortiGate
,
SRX
)
IDS
/
IPS
deployment
and
tuning
(
Snort
,
Suricata
,
Zeek
)
Packet
capture
and
protocol
analysis
(
Wireshark
,
tcpdump
,
NetworkMiner
)
Network
segmentation
and
microsegmentation
(
VLAN
,
VRF
,
NSX
,
Illumio
)
VPN
and
secure
remote
access
(
IPsec
,
OpenVPN
,
WireGuard
)
Zero
Trust
Network
Access
architecture
DNS
security
(
DNSSEC
,
response
policy
zones
,
protective
DNS
)
Secure
web
gateway
,
CASB
and
proxy
policy
802.1
X
,
WPA
3
and
wireless
intrusion
detection
Network
access
control
(
Cisco
ISE
,
Aruba
ClearPass
)
Routing
security
(
RPKI
,
prefix
filtering
,
route
leak
mitigation
)
TLS
inspection
and
load
-
balancer
hardening
(
F
5,
HAProxy
)
Egress
filtering
and
data
exfiltration
controls
AWS
security
(
IAM
policies
,
SCPs
,
GuardDuty
,
Security
Hub
,
CloudTrail
,
KMS
)
Microsoft
Azure
security
(
Entra
ID
,
Defender
for
Cloud
,
Azure
Policy
,
Key
Vault
)
Google
Cloud
security
(
IAM
,
Security
Command
Center
,
Cloud
KMS
,
VPC
-
SC
)
Cloud
security
posture
management
(
Wiz
,
Prisma
Cloud
,
Orca
,
ScoutSuite
)
Infrastructure
-
as
-
Code
scanning
(
Checkov
,
tfsec
,
KICS
)
Container
image
scanning
(
Trivy
,
Grype
,
Clair
)
Container
runtime
security
(
Falco
,
Sysdig
,
seccomp
,
AppArmor
)
Kubernetes
hardening
(
RBAC
,
Pod
Security
Standards
,
OPA
/
Gatekeeper
,
Kyverno
)
Service
mesh
and
mutual
TLS
(
Istio
,
Linkerd
)
Serverless
and
API
gateway
security
Cloud
workload
identity
(
OIDC
federation
,
workload
identity
,
IAM
roles
anywhere
)
Multi
-
cloud
landing
zone
and
guardrail
design
1 / 4
03
APPLICAT ION
&
PRODUCT
SECURIT Y
04
IDENT IT Y
,
ACCESS
&
SECRET S
05
ENDPOINT
,
MALWARE
&
FORENSICS
06
CRYPT OGRAPHY
&
KEY
MANAGEMENT
OWASP
Top
10
and
API
Top
10
mitigation
Secure
code
review
(
Java
,
C
#,
Python
,
JavaScript
/
TypeScript
,
Go
)
Static
analysis
(
Semgrep
,
CodeQL
,
SonarQube
,
Checkmarx
)
Dynamic
analysis
(
Burp
Suite
,
OWASP
ZAP
,
Acunetix
)
Software
composition
analysis
(
Snyk
,
Dependabot
,
OWASP
Dependency
-
Check
)
Manual
web
application
penetration
testing
API
security
testing
(
REST
,
GraphQL
,
gRPC
,
WebSocket
)
Threat
modeling
(
STRIDE
,
PASTA
,
LINDDUN
,
OWASP
Threat
Dragon
)
Secure
SDLC
and
security
champions
programs
Cryptographic
implementation
review
Mobile
application
security
(
MASVS
,
MobSF
,
Frida
)
Fuzzing
and
property
-
based
testing
(
AFL
++,
libFuzzer
,
Jazzer
)
WAF
rule
authoring
and
virtual
patching
(
ModSecurity
,
AWS
WAF
,
Cloudflare
)
Bug
bounty
triage
and
coordinated
disclosure
Authentication
protocols
(
SAML
2.0,
OAuth
2.0,
OIDC
,
Kerberos
,
RADIUS
)
SSO
and
federation
(
Okta
,
Entra
ID
,
Ping
,
Keycloak
)
Phishing
-
resistant
MFA
(
FIDO
2/
WebAuthn
,
passkeys
,
smart
cards
)
Privileged
access
management
(
CyberArk
,
BeyondTrust
,
Delinea
)
Identity
governance
and
administration
(
SailPoint
,
Saviynt
)
RBAC
,
ABAC
and
relationship
-
based
policy
design
Active
Directory
hardening
and
tiered
administration
Secrets
management
(
HashiCorp
Vault
,
AWS
Secrets
Manager
,
SOPS
)
Certificate
lifecycle
and
machine
identity
(
Venafi
,
cert
-
manager
,
ACME
)
Session
management
and
token
hardening
(
JWT
validation
,
refresh
rotation
)
Just
-
in
-
time
and
zero
-
standing
-
privilege
access
Customer
identity
and
consent
management
EDR
/
XDR
operations
(
CrowdStrike
Falcon
,
SentinelOne
,
Defender
XDR
,
Carbon
Black
)
Endpoint
hardening
baselines
(
CIS
Benchmarks
,
STIGs
,
Group
Policy
,
Intune
)
Disk
and
memory
forensics
(
Volatility
,
FTK
,
Axiom
,
Autopsy
,
EnCase
)
Malware
static
analysis
(
Ghidra
,
IDA
Pro
,
PEStudio
,
FLOSS
)
Malware
dynamic
analysis
and
sandboxing
(
CAPE
,
Joe
Sandbox
,
Any
.
Run
)
Live
response
and
triage
collection
(
Velociraptor
,
KAPE
,
Redline
)
Host
-
based
detection
telemetry
(
Sysmon
,
auditd
,
eBPF
,
ETW
)
Filesystem
artifact
analysis
(
MFT
,
registry
,
prefetch
,
shimcache
,
USN
journal
)
macOS
,
Linux
and
mobile
endpoint
forensics
Anti
-
forensics
detection
and
timeline
reconstruction
Chain
of
custody
and
evidence
handling
Root
-
cause
analysis
and
post
-
incident
reporting
Symmetric
and
asymmetric
cryptography
(
AES
-
GCM
,
ChaCha
20,
RSA
,
ECC
)
Hashing
and
integrity
primitives
(
SHA
-2/3,
HMAC
,
Argon
2,
bcrypt
)
TLS
configuration
and
hardening
(
cipher
suites
,
HSTS
,
certificate
transparency
)
PKI
design
and
operation
(
CA
hierarchies
,
CRL
/
OCSP
,
ACME
)
Hardware
security
modules
and
secure
enclaves
Key
lifecycle
,
rotation
and
escrow
strategy
Digital
signatures
and
code
signing
Supply
-
chain
attestation
(
Sigstore
,
in
-
toto
,
SLSA
provenance
)
Post
-
quantum
readiness
(
ML
-
KEM
,
ML
-
DSA
,
hybrid
key
exchange
)
Confidential
computing
and
data
-
in
-
use
protection
Cryptographic
implementation
flaw
analysis
2 / 4
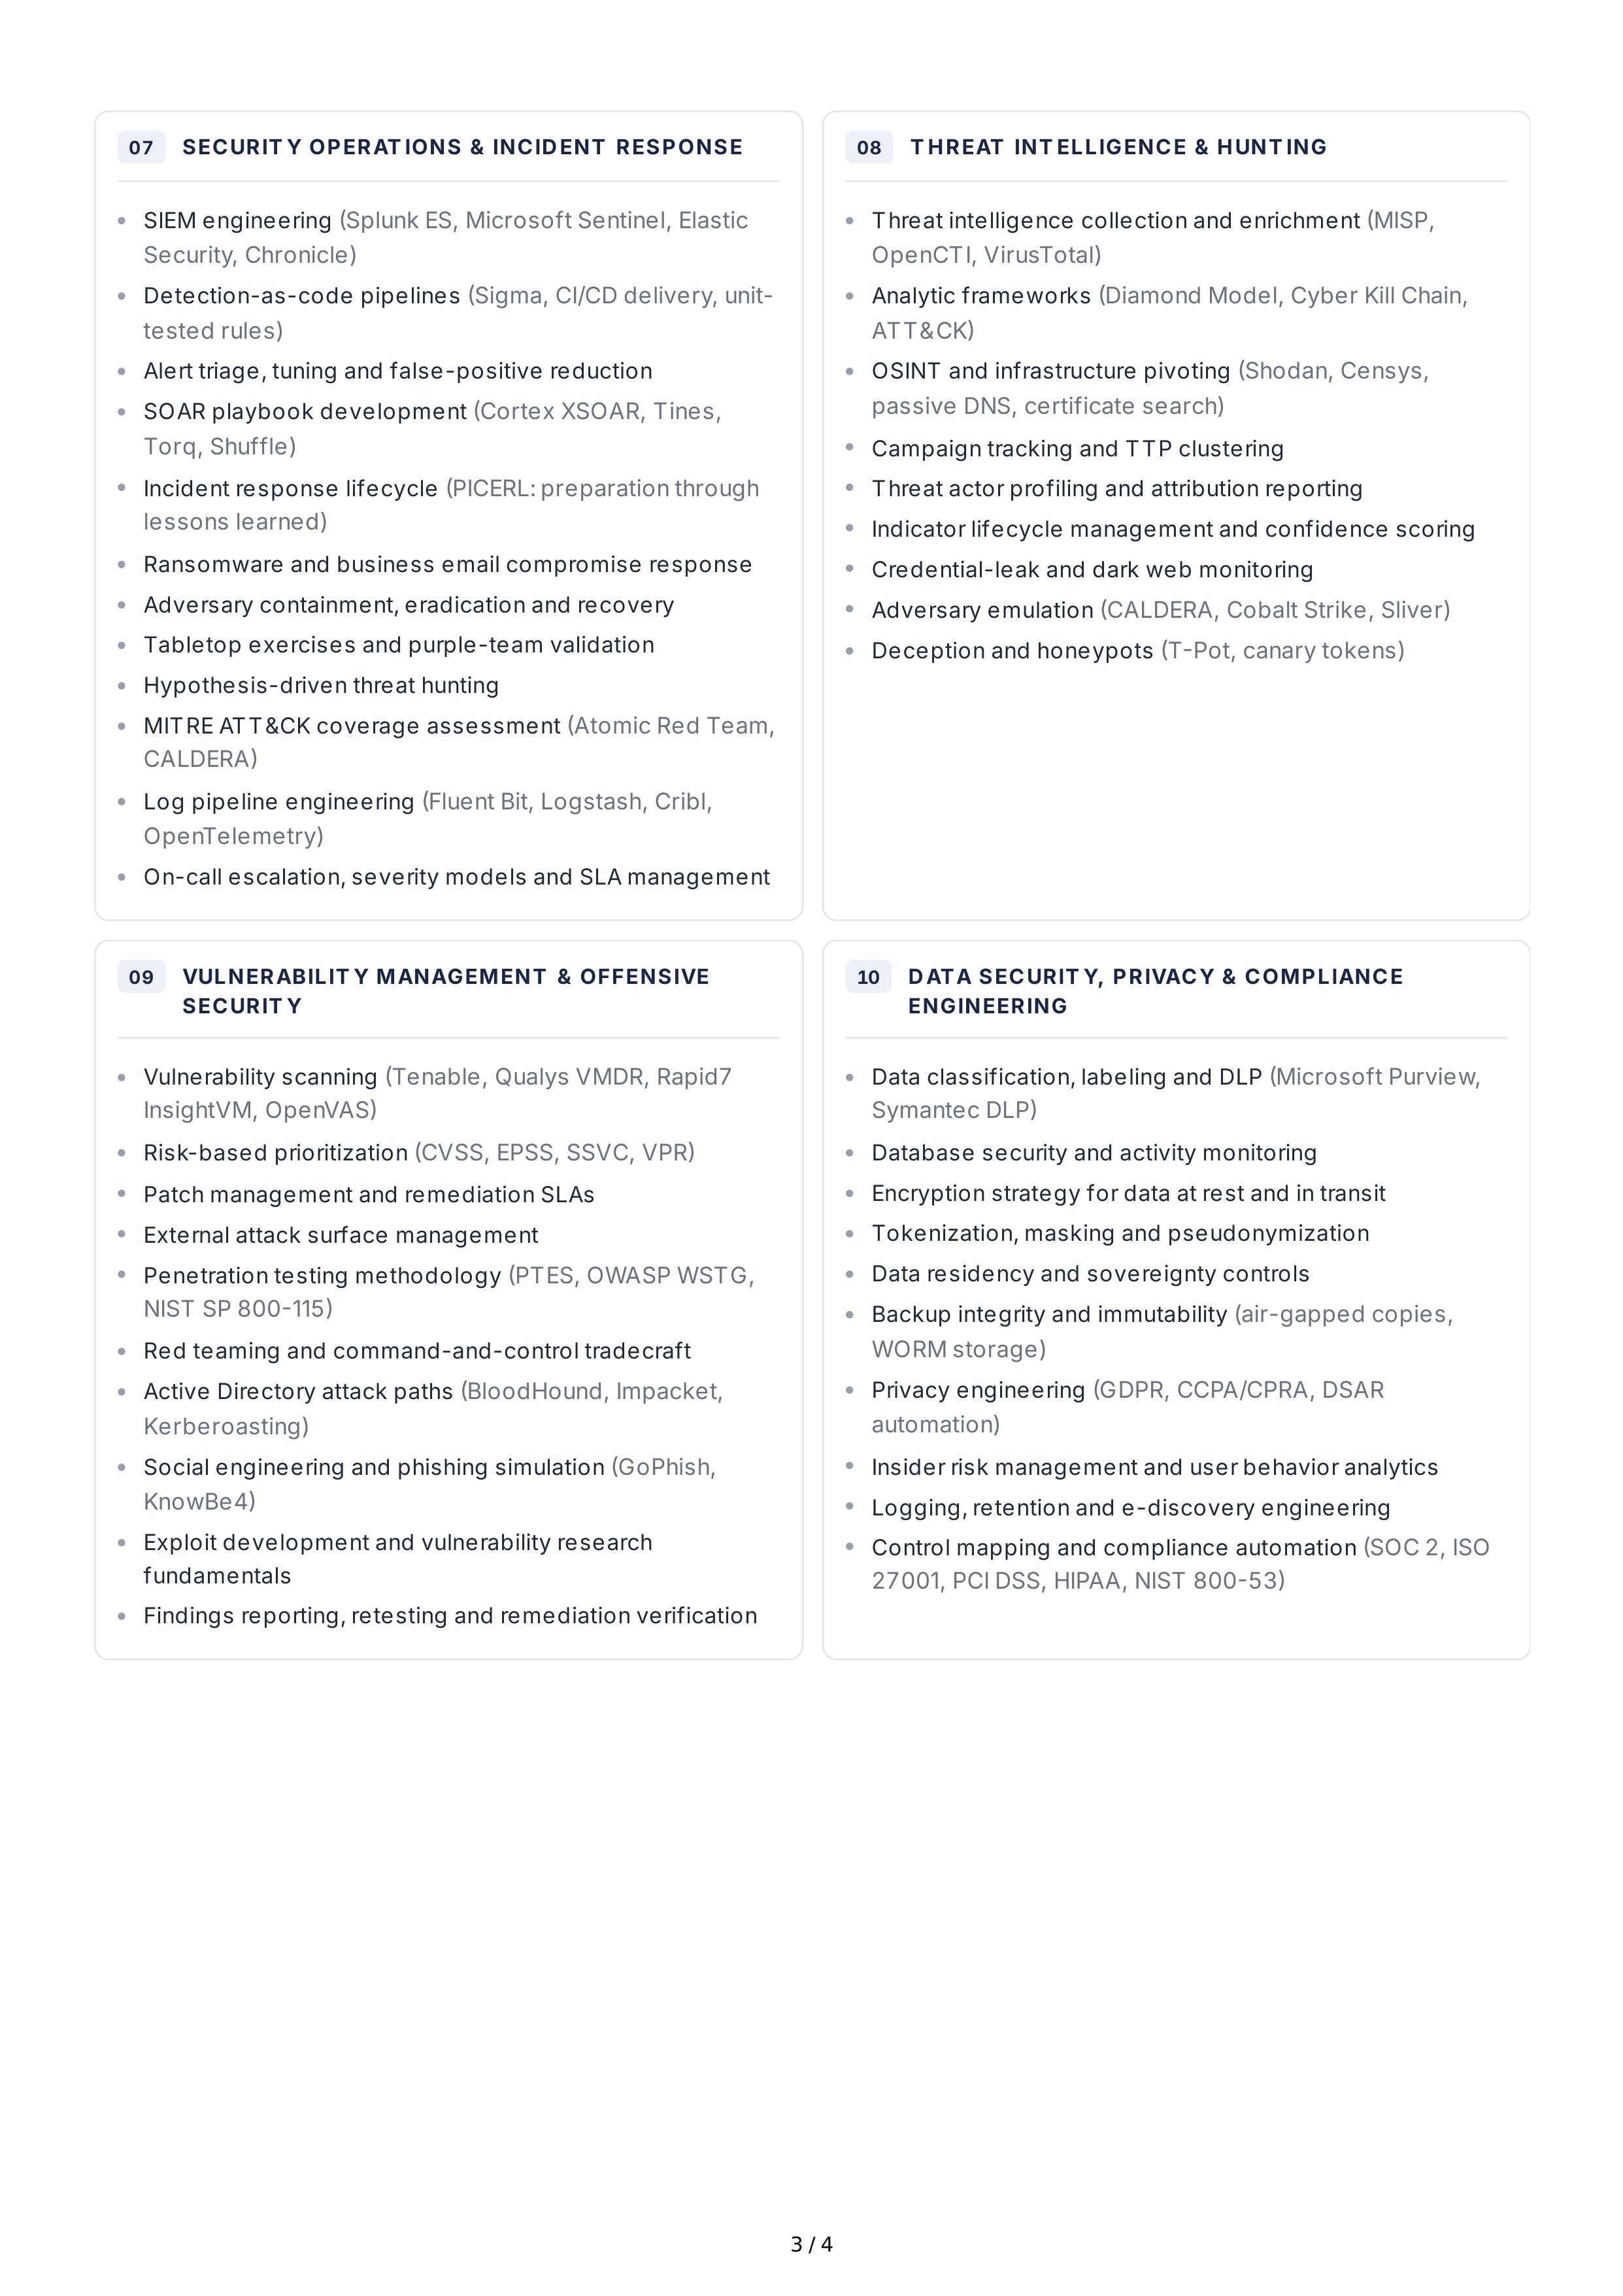
07
SECURIT Y
OPERAT IONS
&
INCIDENT
RESPONSE
08
T HREAT
INT ELLIGENCE
&
HUNT ING
09
VULNERABILIT Y
MANAGEMENT
&
OFFENSIVE
SECURIT Y
10
DATA
SECURIT Y
,
PRIVACY
&
COMPLIANCE
ENGINEERING
SIEM
engineering
(
Splunk
ES
,
Microsoft
Sentinel
,
Elastic
Security
,
Chronicle
)
Detection
-
as
-
code
pipelines
(
Sigma
,
CI
/
CD
delivery
,
unit
-
tested
rules
)
Alert
triage
,
tuning
and
false
-
positive
reduction
SOAR
playbook
development
(
Cortex
XSOAR
,
Tines
,
Torq
,
Shuffle
)
Incident
response
lifecycle
(
PICERL
:
preparation
through
lessons
learned
)
Ransomware
and
business
email
compromise
response
Adversary
containment
,
eradication
and
recovery
Tabletop
exercises
and
purple
-
team
validation
Hypothesis
-
driven
threat
hunting
MITRE
ATT
&
CK
coverage
assessment
(
Atomic
Red
Team
,
CALDERA
)
Log
pipeline
engineering
(
Fluent
Bit
,
Logstash
,
Cribl
,
OpenTelemetry
)
On
-
call
escalation
,
severity
models
and
SLA
management
Threat
intelligence
collection
and
enrichment
(
MISP
,
OpenCTI
,
VirusTotal
)
Analytic
frameworks
(
Diamond
Model
,
Cyber
Kill
Chain
,
ATT
&
CK
)
OSINT
and
infrastructure
pivoting
(
Shodan
,
Censys
,
passive
DNS
,
certificate
search
)
Campaign
tracking
and
TTP
clustering
Threat
actor
profiling
and
attribution
reporting
Indicator
lifecycle
management
and
confidence
scoring
Credential
-
leak
and
dark
web
monitoring
Adversary
emulation
(
CALDERA
,
Cobalt
Strike
,
Sliver
)
Deception
and
honeypots
(
T
-
Pot
,
canary
tokens
)
Vulnerability
scanning
(
Tenable
,
Qualys
VMDR
,
Rapid
7
InsightVM
,
OpenVAS
)
Risk
-
based
prioritization
(
CVSS
,
EPSS
,
SSVC
,
VPR
)
Patch
management
and
remediation
SLAs
External
attack
surface
management
Penetration
testing
methodology
(
PTES
,
OWASP
WSTG
,
NIST
SP
800-115)
Red
teaming
and
command
-
and
-
control
tradecraft
Active
Directory
attack
paths
(
BloodHound
,
Impacket
,
Kerberoasting
)
Social
engineering
and
phishing
simulation
(
GoPhish
,
KnowBe
4)
Exploit
development
and
vulnerability
research
fundamentals
Findings
reporting
,
retesting
and
remediation
verification
Data
classification
,
labeling
and
DLP
(
Microsoft
Purview
,
Symantec
DLP
)
Database
security
and
activity
monitoring
Encryption
strategy
for
data
at
rest
and
in
transit
Tokenization
,
masking
and
pseudonymization
Data
residency
and
sovereignty
controls
Backup
integrity
and
immutability
(
air
-
gapped
copies
,
WORM
storage
)
Privacy
engineering
(
GDPR
,
CCPA
/
CPRA
,
DSAR
automation
)
Insider
risk
management
and
user
behavior
analytics
Logging
,
retention
and
e
-
discovery
engineering
Control
mapping
and
compliance
automation
(
SOC
2,
ISO
27001,
PCI
DSS
,
HIPAA
,
NIST
800-53)
3 / 4
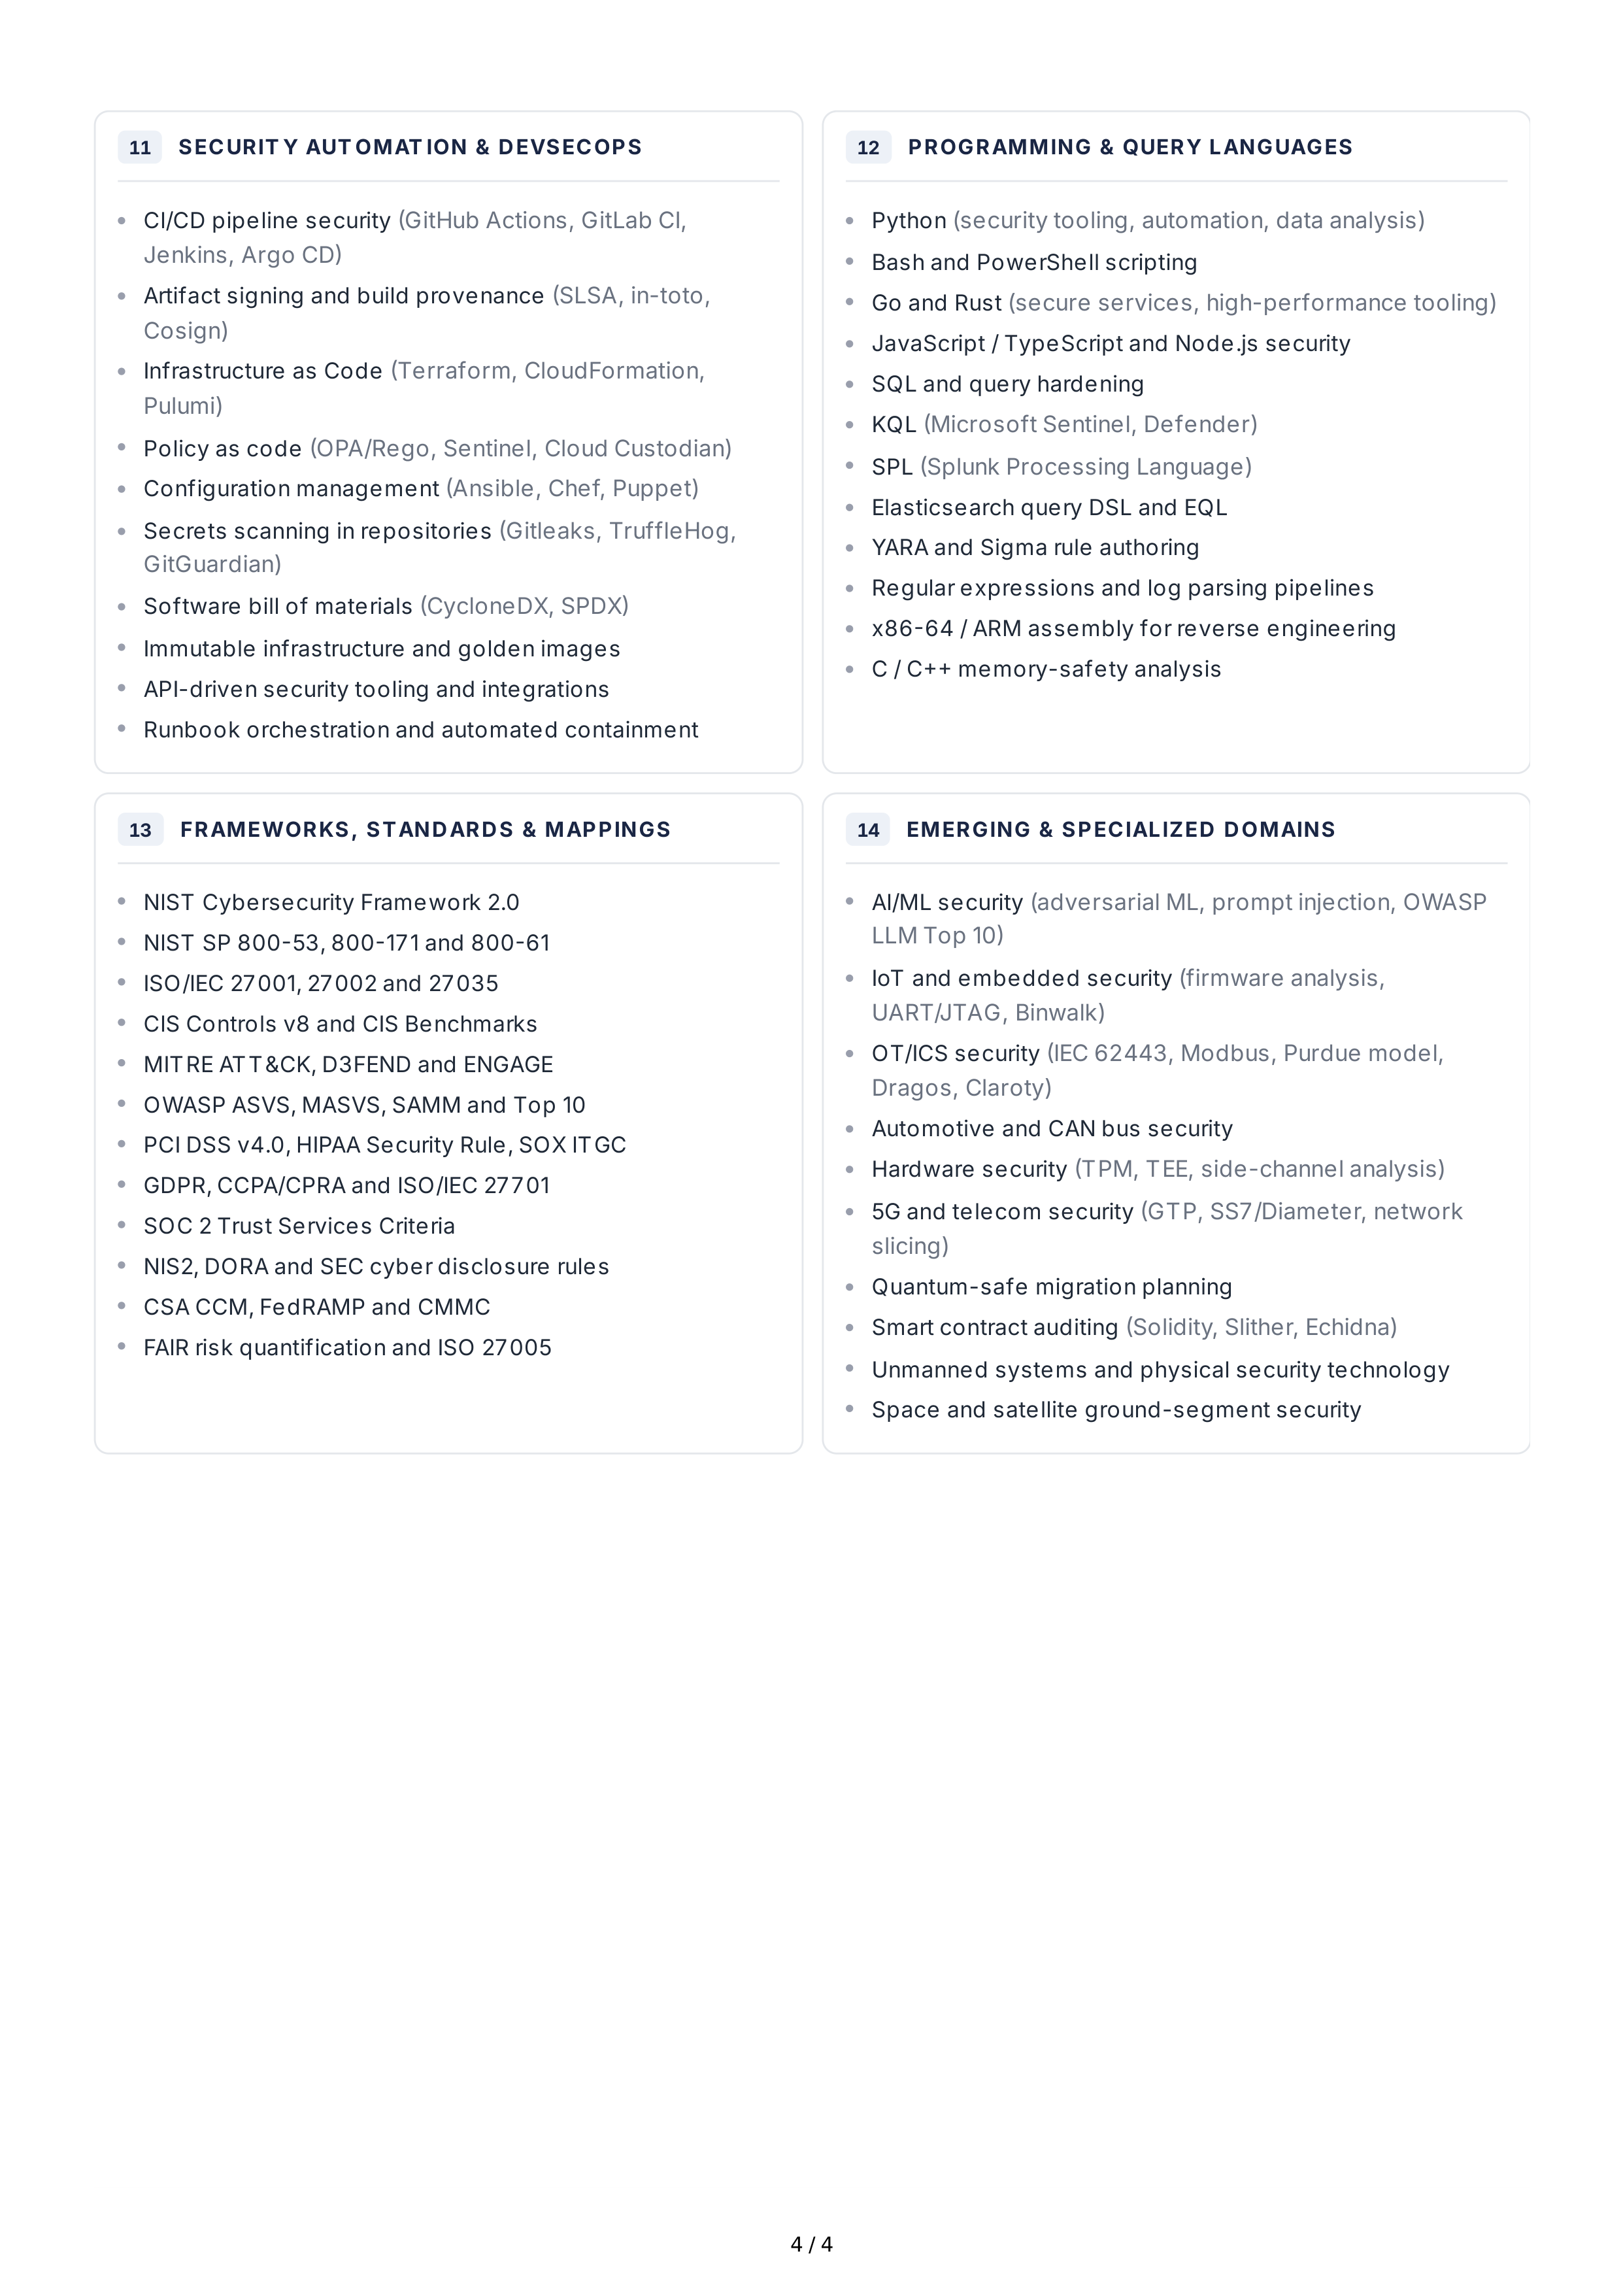
11
SECURIT Y
AUT OMAT ION
&
DEVSECOPS
12
PROGRAMMING
&
QUERY
LANGUAGES
13
FRAMEWORKS
,
STANDARDS
&
MAPPINGS
14
EMERGING
&
SPECIALIZED
DOMAINS
CI
/
CD
pipeline
security
(
GitHub
Actions
,
GitLab
CI
,
Jenkins
,
Argo
CD
)
Artifact
signing
and
build
provenance
(
SLSA
,
in
-
toto
,
Cosign
)
Infrastructure
as
Code
(
Terraform
,
CloudFormation
,
Pulumi
)
Policy
as
code
(
OPA
/
Rego
,
Sentinel
,
Cloud
Custodian
)
Configuration
management
(
Ansible
,
Chef
,
Puppet
)
Secrets
scanning
in
repositories
(
Gitleaks
,
TruffleHog
,
GitGuardian
)
Software
bill
of
materials
(
CycloneDX
,
SPDX
)
Immutable
infrastructure
and
golden
images
API
-
driven
security
tooling
and
integrations
Runbook
orchestration
and
automated
containment
Python
(
security
tooling
,
automation
,
data
analysis
)
Bash
and
PowerShell
scripting
Go
and
Rust
(
secure
services
,
high
-
performance
tooling
)
JavaScript
/
TypeScript
and
Node
.
js
security
SQL
and
query
hardening
KQL
(
Microsoft
Sentinel
,
Defender
)
SPL
(
Splunk
Processing
Language
)
Elasticsearch
query
DSL
and
EQL
YARA
and
Sigma
rule
authoring
Regular
expressions
and
log
parsing
pipelines
x
86-64 /
ARM
assembly
for
reverse
engineering
C
/
C
++
memory
-
safety
analysis
NIST
Cybersecurity
Framework
2.0
NIST
SP
800-53, 800-171
and
800-61
ISO
/
IEC
27001, 27002
and
27035
CIS
Controls
v
8
and
CIS
Benchmarks
MITRE
ATT
&
CK
,
D
3
FEND
and
ENGAGE
OWASP
ASVS
,
MASVS
,
SAMM
and
Top
10
PCI
DSS
v
4.0,
HIPAA
Security
Rule
,
SOX
ITGC
GDPR
,
CCPA
/
CPRA
and
ISO
/
IEC
27701
SOC
2
Trust
Services
Criteria
NIS
2,
DORA
and
SEC
cyber
disclosure
rules
CSA
CCM
,
FedRAMP
and
CMMC
FAIR
risk
quantification
and
ISO
27005
AI
/
ML
security
(
adversarial
ML
,
prompt
injection
,
OWASP
LLM
Top
10)
IoT
and
embedded
security
(
firmware
analysis
,
UART
/
JTAG
,
Binwalk
)
OT
/
ICS
security
(
IEC
62443,
Modbus
,
Purdue
model
,
Dragos
,
Claroty
)
Automotive
and
CAN
bus
security
Hardware
security
(
TPM
,
TEE
,
side
-
channel
analysis
)
5
G
and
telecom
security
(
GTP
,
SS
7/
Diameter
,
network
slicing
)
Quantum
-
safe
migration
planning
Smart
contract
auditing
(
Solidity
,
Slither
,
Echidna
)
Unmanned
systems
and
physical
security
technology
Space
and
satellite
ground
-
segment
security
4 / 4