Network
Security
Network
Security
Architecture
&
Design
Zero
Trust
Architecture
Micro
-
segmentation
,
identity
-
aware
proxies
,
continuous
verification
of
every
session
Defense
in
Depth
Layered
,
overlapping
controls
across
network
,
host
,
application
and
data
tiers
Network
Segmentation
&
VLAN
Design
Trust
zones
,
inter
-
zone
policy
,
traffic
isolation
and
PCI
scope
reduction
DMZ
&
Screened
Subnet
Design
Public
-
facing
service
placement
,
bastion
hosts
and
jump
-
box
architecture
Secure
Topology
Design
Hub
-
and
-
spoke
,
spine
-
leaf
and
SD
-
WAN
fabric
patterns
with
resilient
failover
Network
Access
Control
802.1
X
,
RADIUS
and
TACACS
+
integration
with
endpoint
posture
assessment
Perimeter
Defense
&
Firewall
Engineering
Next
-
Generation
Firewalls
Palo
Alto
PAN
-
OS
,
Fortinet
FortiOS
and
Cisco
Secure
Firewall
policy
design
Stateful
Inspection
&
Rule
Optimization
Rule
hygiene
,
shadowing
analysis
,
object
cleanup
and
hit
-
count
review
Firewall
Policy
Lifecycle
Management
Tufin
and
AlgoSec
change
workflows
,
recertification
and
audit
trails
Web
Application
Firewalls
ModSecurity
,
AWS
WAF
and
Cloudflare
rulesets
with
false
-
positive
tuning
Secure
Web
Gateway
&
Proxy
Zscaler
,
Netskope
and
forward
/
reverse
proxy
hardening
and
SSL
inspection
Egress
Filtering
&
DNS
Sinkholing
Outbound
allowlisting
,
domain
reputation
blocking
and
C
2
callback
suppression
01
02
1 / 7
Network
Monitoring
,
IDS
/
IPS
&
Traffic
Analysis
IDS
/
IPS
Engineering
Snort
,
Suricata
and
Zeek
rule
authoring
,
tuning
and
false
-
positive
reduction
Network
Traffic
Analysis
NDR
platforms
,
traffic
baselining
and
behavioural
anomaly
detection
Full
Packet
Capture
&
PCAP
Forensics
Wireshark
and
tcpdump
analysis
,
stream
reassembly
,
PCAP
triage
at
scale
Flow
Analytics
NetFlow
,
IPFIX
and
sFlow
collection
,
retention
design
and
reporting
Encrypted
Traffic
Analytics
TLS
interception
architecture
,
JA
3/
JA
4
fingerprinting
and
certificate
metadata
Protocol
Deep
Inspection
TCP
/
IP
,
DNS
,
ARP
,
HTTP
/2,
QUIC
and
BGP
behaviour
under
adversarial
load
Deception
&
Honeypots
Canary
tokens
,
honeynets
and
lateral
movement
lures
for
early
detection
Cryptography
&
Public
Key
Infrastructure
TLS
1.2 /
TLS
1.3
Hardening
Cipher
suite
selection
,
HSTS
,
forward
secrecy
,
OCSP
stapling
and
CT
monitoring
PKI
Design
&
Operations
Microsoft
AD
CS
and
EJBCA
,
two
-
tier
CA
hierarchies
,
CRL
and
OCSP
services
Certificate
Lifecycle
Management
Issuance
,
renewal
automation
,
expiry
monitoring
and
rogue
certificate
discovery
IPsec
&
IKEv
2
Cryptography
Phase
1
and
2
proposals
,
Diffie
-
Hellman
group
selection
and
perfect
forward
secrecy
Key
Management
&
HSM
AWS
KMS
,
Thales
Luna
and
HashiCorp
Vault
Transit
with
rotation
workflows
Hashing
&
Digital
Signatures
SHA
-2/
SHA
-3,
HMAC
,
code
signing
and
non
-
repudiation
controls
Post
-
Quantum
Readiness
ML
-
KEM
and
ML
-
DSA
migration
planning
,
cryptographic
inventory
and
agility
03
04
2 / 7
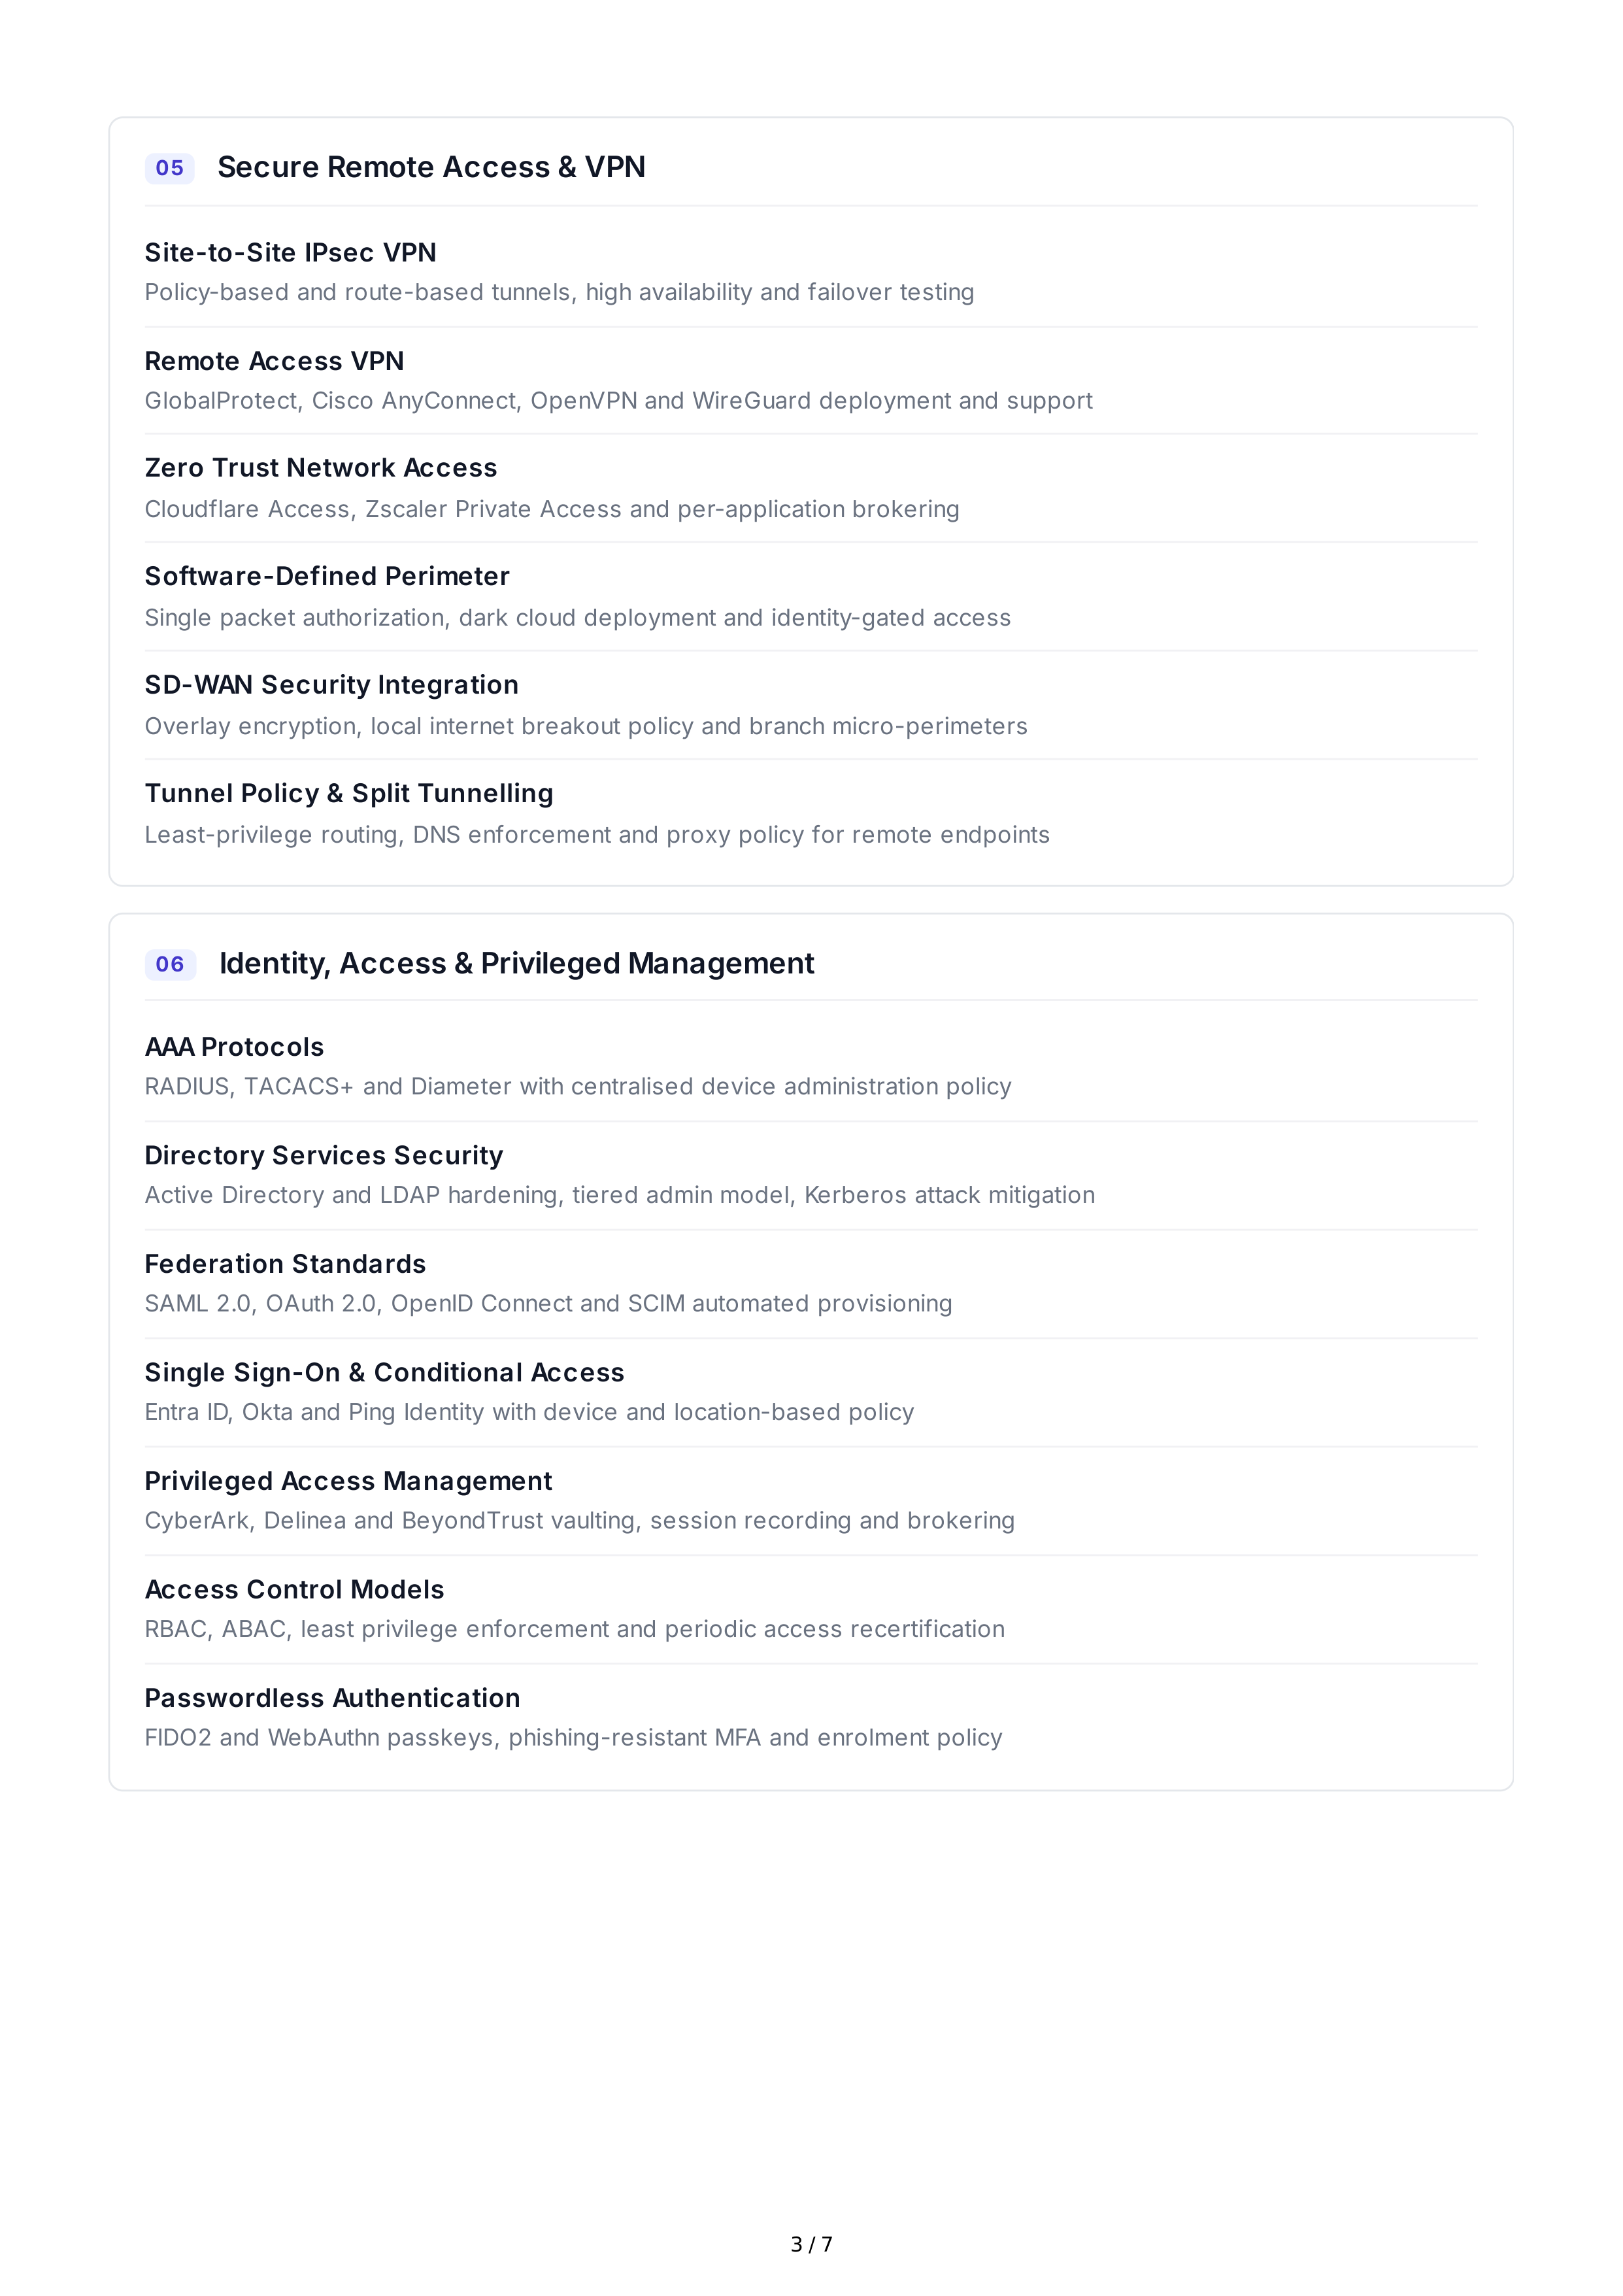
Secure
Remote
Access
&
VPN
Site
-
to
-
Site
IPsec
VPN
Policy
-
based
and
route
-
based
tunnels
,
high
availability
and
failover
testing
Remote
Access
VPN
GlobalProtect
,
Cisco
AnyConnect
,
OpenVPN
and
WireGuard
deployment
and
support
Zero
Trust
Network
Access
Cloudflare
Access
,
Zscaler
Private
Access
and
per
-
application
brokering
Software
-
Defined
Perimeter
Single
packet
authorization
,
dark
cloud
deployment
and
identity
-
gated
access
SD
-
WAN
Security
Integration
Overlay
encryption
,
local
internet
breakout
policy
and
branch
micro
-
perimeters
Tunnel
Policy
&
Split
Tunnelling
Least
-
privilege
routing
,
DNS
enforcement
and
proxy
policy
for
remote
endpoints
Identity
,
Access
&
Privileged
Management
AAA
Protocols
RADIUS
,
TACACS
+
and
Diameter
with
centralised
device
administration
policy
Directory
Services
Security
Active
Directory
and
LDAP
hardening
,
tiered
admin
model
,
Kerberos
attack
mitigation
Federation
Standards
SAML
2.0,
OAuth
2.0,
OpenID
Connect
and
SCIM
automated
provisioning
Single
Sign
-
On
&
Conditional
Access
Entra
ID
,
Okta
and
Ping
Identity
with
device
and
location
-
based
policy
Privileged
Access
Management
CyberArk
,
Delinea
and
BeyondTrust
vaulting
,
session
recording
and
brokering
Access
Control
Models
RBAC
,
ABAC
,
least
privilege
enforcement
and
periodic
access
recertification
Passwordless
Authentication
FIDO
2
and
WebAuthn
passkeys
,
phishing
-
resistant
MFA
and
enrolment
policy
05
06
3 / 7
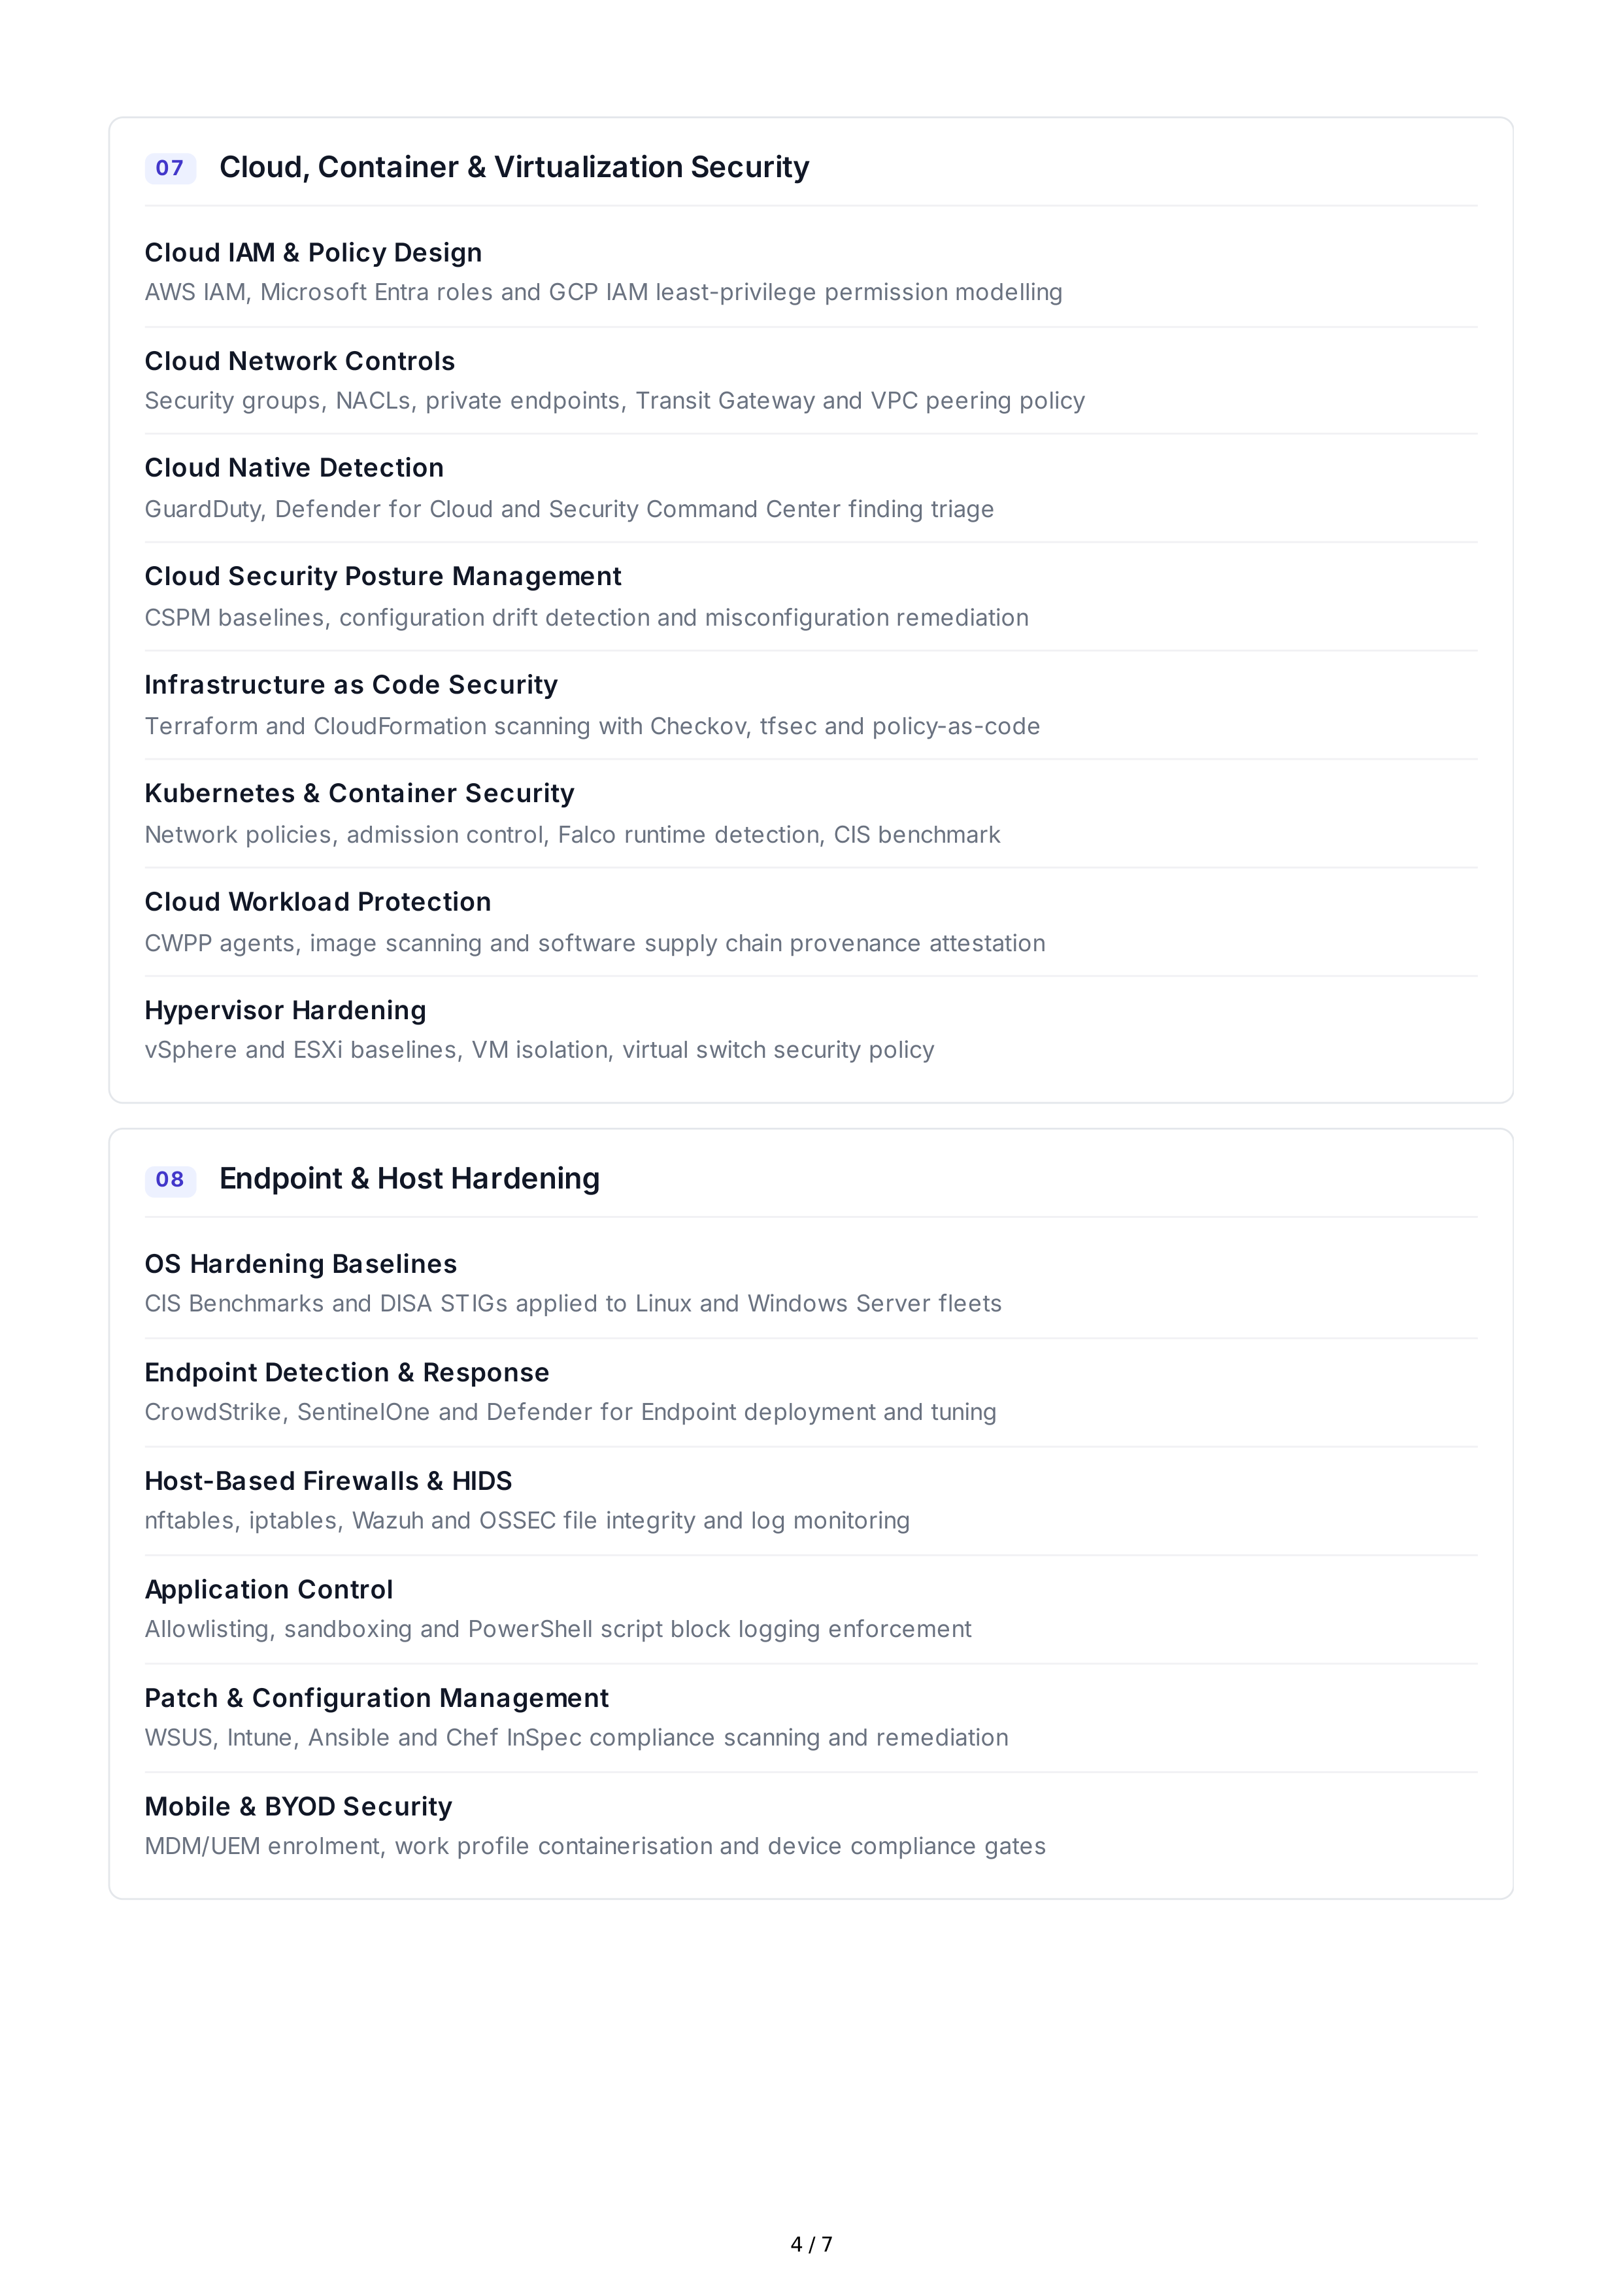
Cloud
,
Container
&
Virtualization
Security
Cloud
IAM
&
Policy
Design
AWS
IAM
,
Microsoft
Entra
roles
and
GCP
IAM
least
-
privilege
permission
modelling
Cloud
Network
Controls
Security
groups
,
NACLs
,
private
endpoints
,
Transit
Gateway
and
VPC
peering
policy
Cloud
Native
Detection
GuardDuty
,
Defender
for
Cloud
and
Security
Command
Center
finding
triage
Cloud
Security
Posture
Management
CSPM
baselines
,
configuration
drift
detection
and
misconfiguration
remediation
Infrastructure
as
Code
Security
Terraform
and
CloudFormation
scanning
with
Checkov
,
tfsec
and
policy
-
as
-
code
Kubernetes
&
Container
Security
Network
policies
,
admission
control
,
Falco
runtime
detection
,
CIS
benchmark
Cloud
Workload
Protection
CWPP
agents
,
image
scanning
and
software
supply
chain
provenance
attestation
Hypervisor
Hardening
vSphere
and
ESXi
baselines
,
VM
isolation
,
virtual
switch
security
policy
Endpoint
&
Host
Hardening
OS
Hardening
Baselines
CIS
Benchmarks
and
DISA
STIGs
applied
to
Linux
and
Windows
Server
fleets
Endpoint
Detection
&
Response
CrowdStrike
,
SentinelOne
and
Defender
for
Endpoint
deployment
and
tuning
Host
-
Based
Firewalls
&
HIDS
nftables
,
iptables
,
Wazuh
and
OSSEC
file
integrity
and
log
monitoring
Application
Control
Allowlisting
,
sandboxing
and
PowerShell
script
block
logging
enforcement
Patch
&
Configuration
Management
WSUS
,
Intune
,
Ansible
and
Chef
InSpec
compliance
scanning
and
remediation
Mobile
&
BYOD
Security
MDM
/
UEM
enrolment
,
work
profile
containerisation
and
device
compliance
gates
07
08
4 / 7
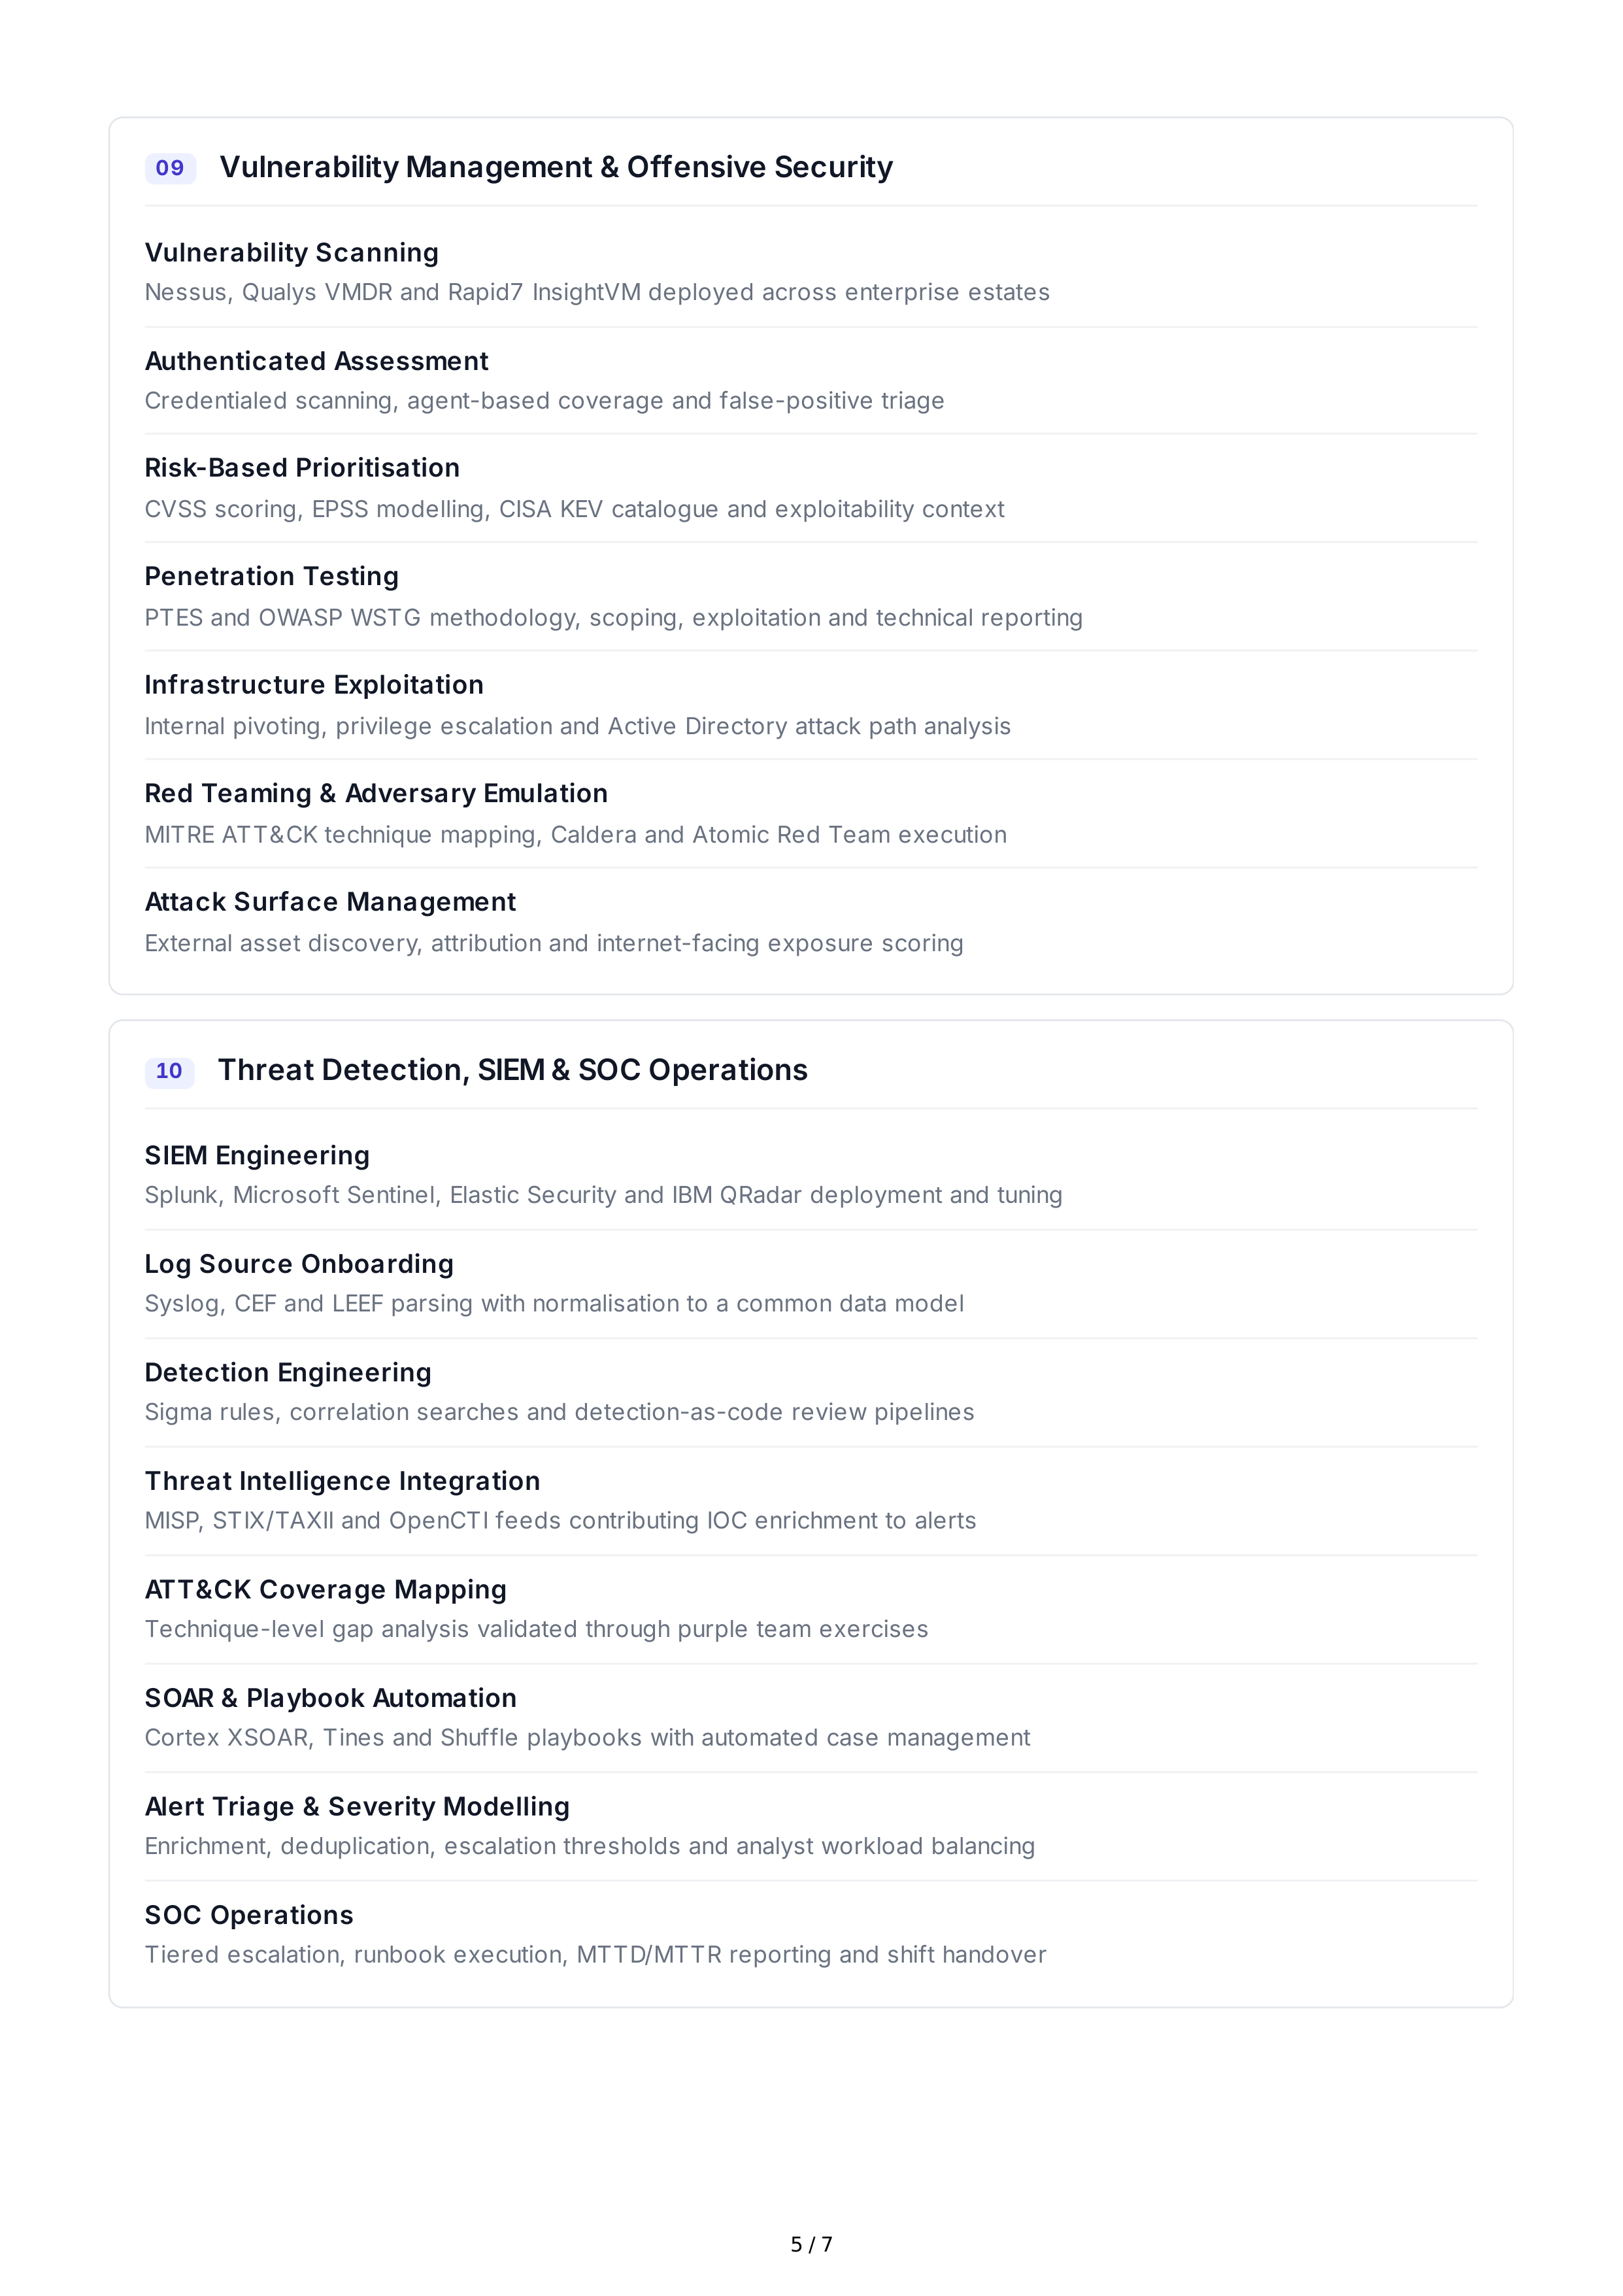
Vulnerability
Management
&
Offensive
Security
Vulnerability
Scanning
Nessus
,
Qualys
VMDR
and
Rapid
7
InsightVM
deployed
across
enterprise
estates
Authenticated
Assessment
Credentialed
scanning
,
agent
-
based
coverage
and
false
-
positive
triage
Risk
-
Based
Prioritisation
CVSS
scoring
,
EPSS
modelling
,
CISA
KEV
catalogue
and
exploitability
context
Penetration
Testing
PTES
and
OWASP
WSTG
methodology
,
scoping
,
exploitation
and
technical
reporting
Infrastructure
Exploitation
Internal
pivoting
,
privilege
escalation
and
Active
Directory
attack
path
analysis
Red
Teaming
&
Adversary
Emulation
MITRE
ATT
&
CK
technique
mapping
,
Caldera
and
Atomic
Red
Team
execution
Attack
Surface
Management
External
asset
discovery
,
attribution
and
internet
-
facing
exposure
scoring
Threat
Detection
,
SIEM
&
SOC
Operations
SIEM
Engineering
Splunk
,
Microsoft
Sentinel
,
Elastic
Security
and
IBM
QRadar
deployment
and
tuning
Log
Source
Onboarding
Syslog
,
CEF
and
LEEF
parsing
with
normalisation
to
a
common
data
model
Detection
Engineering
Sigma
rules
,
correlation
searches
and
detection
-
as
-
code
review
pipelines
Threat
Intelligence
Integration
MISP
,
STIX
/
TAXII
and
OpenCTI
feeds
contributing
IOC
enrichment
to
alerts
ATT
&
CK
Coverage
Mapping
Technique
-
level
gap
analysis
validated
through
purple
team
exercises
SOAR
&
Playbook
Automation
Cortex
XSOAR
,
Tines
and
Shuffle
playbooks
with
automated
case
management
Alert
Triage
&
Severity
Modelling
Enrichment
,
deduplication
,
escalation
thresholds
and
analyst
workload
balancing
SOC
Operations
Tiered
escalation
,
runbook
execution
,
MTTD
/
MTTR
reporting
and
shift
handover
09
10
5 / 7
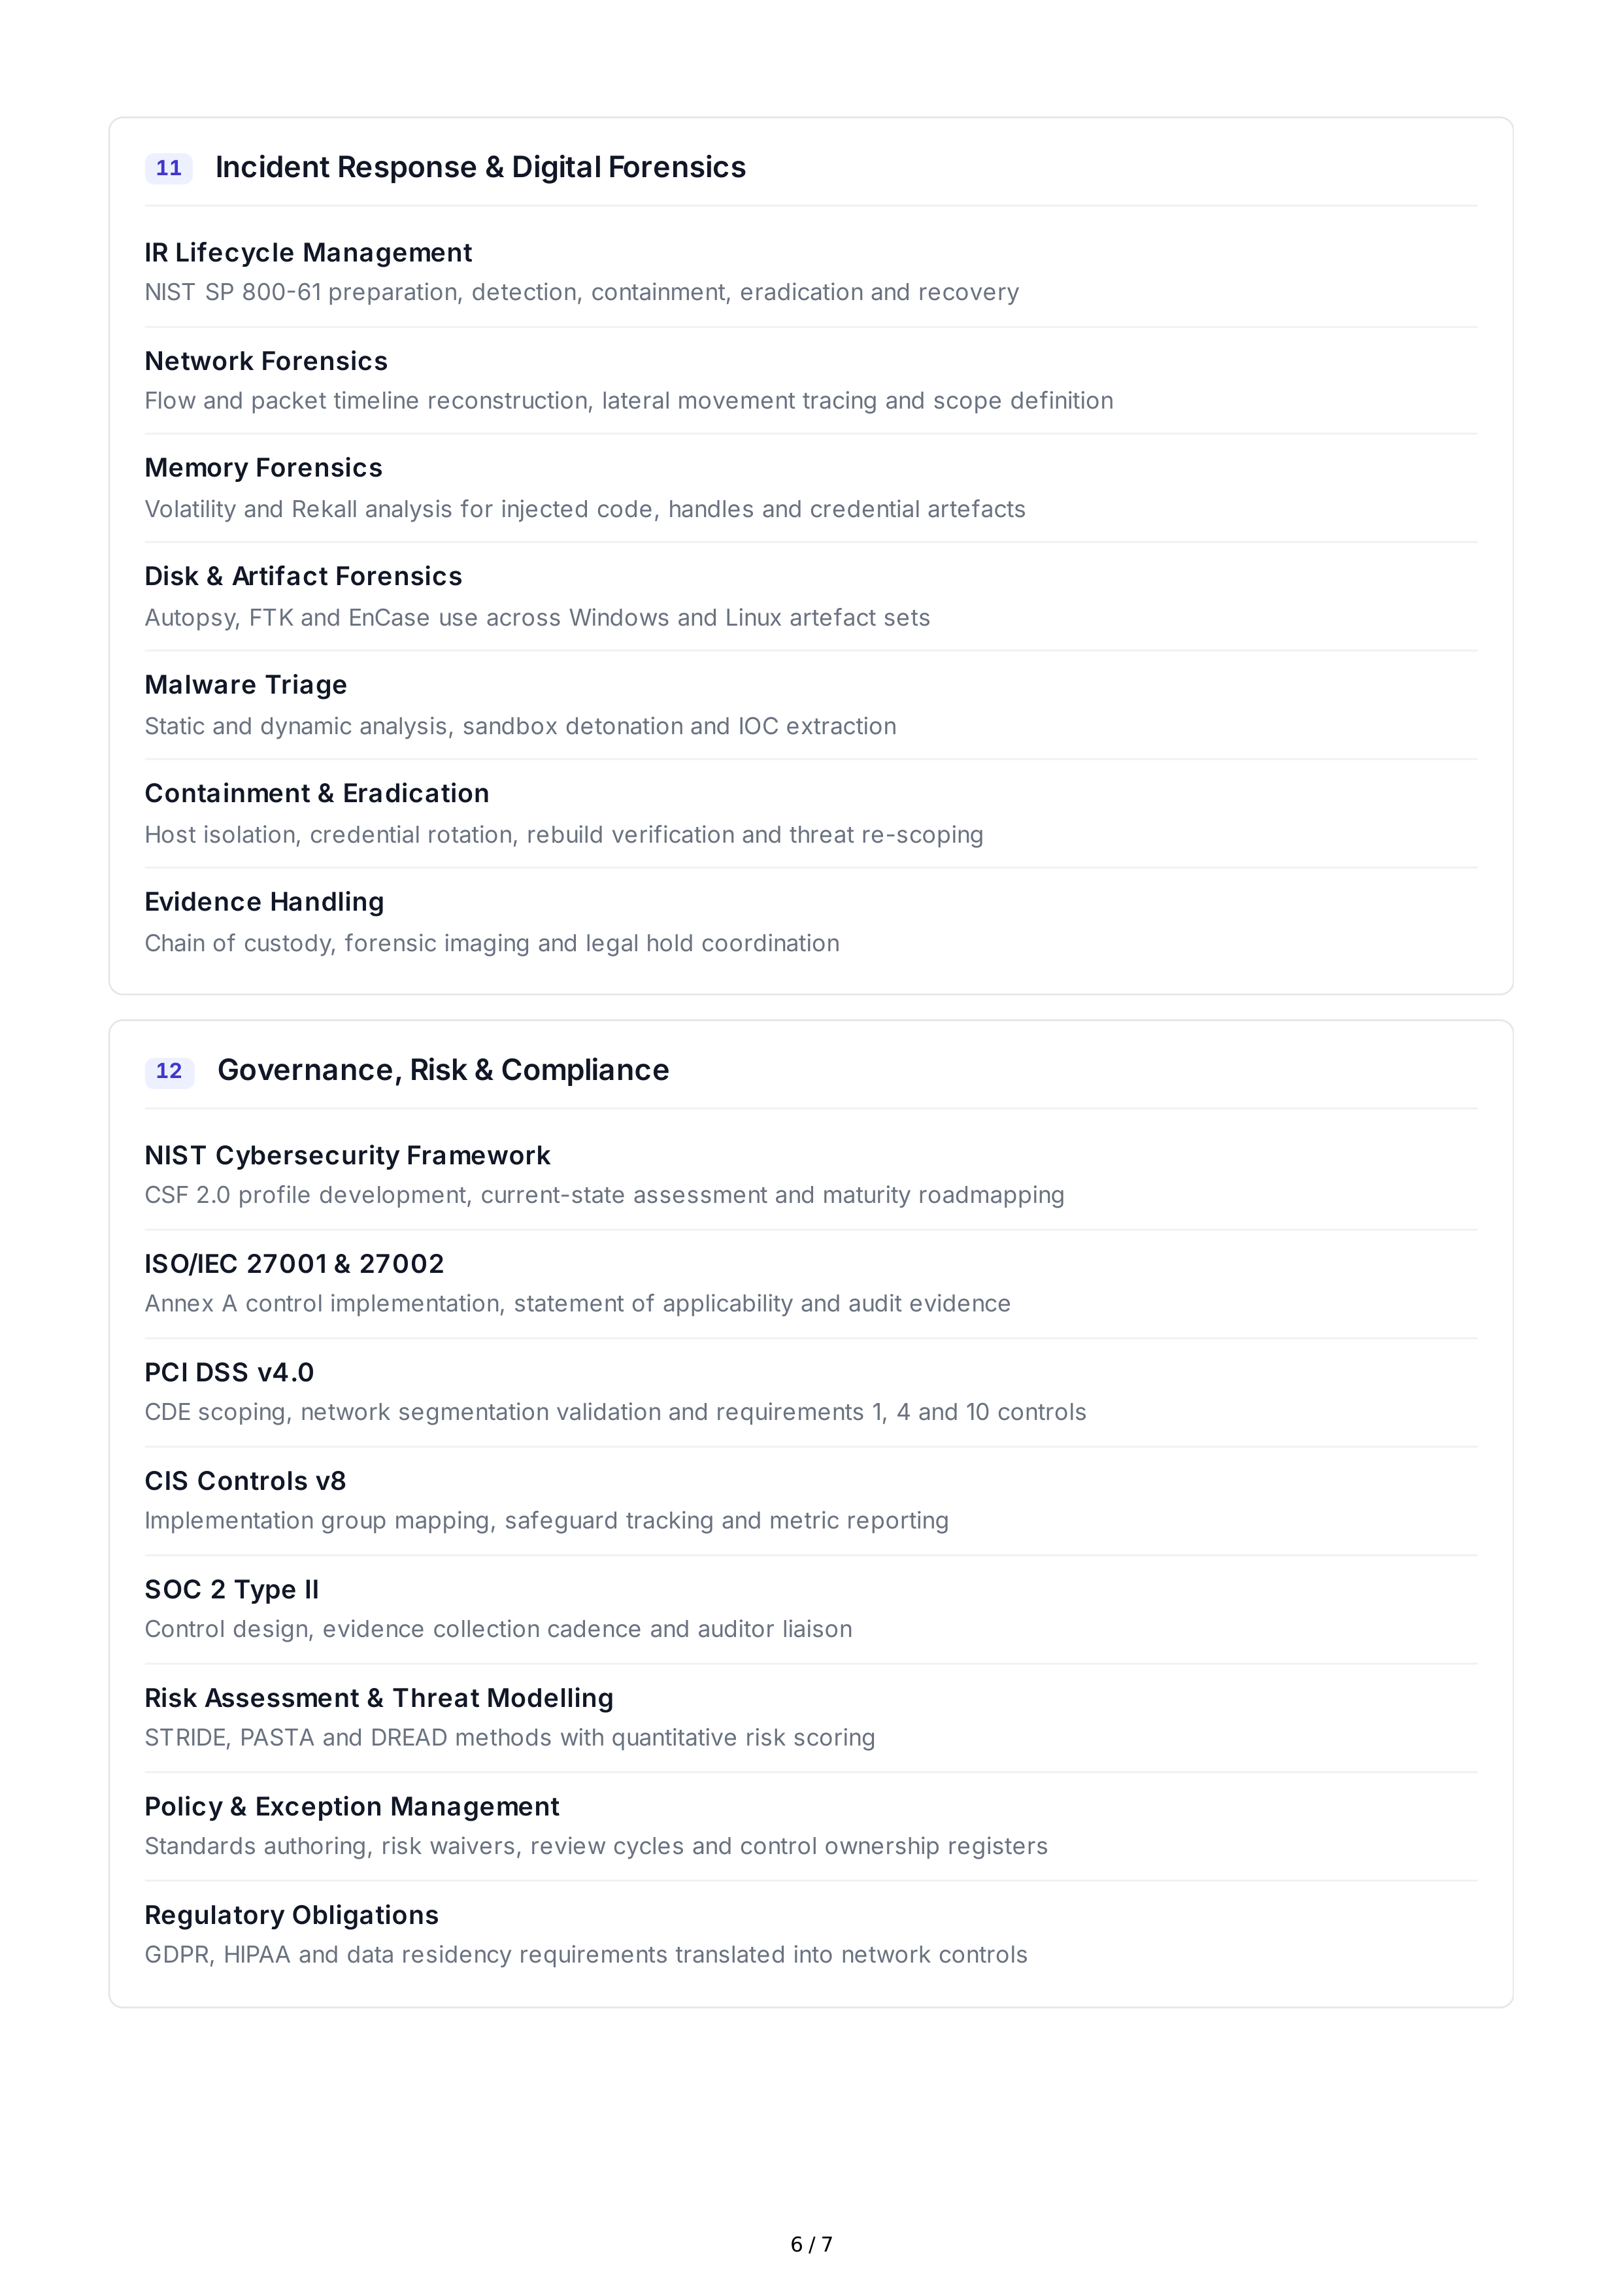
Incident
Response
&
Digital
Forensics
IR
Lifecycle
Management
NIST
SP
800-61
preparation
,
detection
,
containment
,
eradication
and
recovery
Network
Forensics
Flow
and
packet
timeline
reconstruction
,
lateral
movement
tracing
and
scope
definition
Memory
Forensics
Volatility
and
Rekall
analysis
for
injected
code
,
handles
and
credential
artefacts
Disk
&
Artifact
Forensics
Autopsy
,
FTK
and
EnCase
use
across
Windows
and
Linux
artefact
sets
Malware
Triage
Static
and
dynamic
analysis
,
sandbox
detonation
and
IOC
extraction
Containment
&
Eradication
Host
isolation
,
credential
rotation
,
rebuild
verification
and
threat
re
-
scoping
Evidence
Handling
Chain
of
custody
,
forensic
imaging
and
legal
hold
coordination
Governance
,
Risk
&
Compliance
NIST
Cybersecurity
Framework
CSF
2.0
profile
development
,
current
-
state
assessment
and
maturity
roadmapping
ISO
/
IEC
27001 & 27002
Annex
A
control
implementation
,
statement
of
applicability
and
audit
evidence
PCI
DSS
v
4.0
CDE
scoping
,
network
segmentation
validation
and
requirements
1, 4
and
10
controls
CIS
Controls
v
8
Implementation
group
mapping
,
safeguard
tracking
and
metric
reporting
SOC
2
Type
II
Control
design
,
evidence
collection
cadence
and
auditor
liaison
Risk
Assessment
&
Threat
Modelling
STRIDE
,
PASTA
and
DREAD
methods
with
quantitative
risk
scoring
Policy
&
Exception
Management
Standards
authoring
,
risk
waivers
,
review
cycles
and
control
ownership
registers
Regulatory
Obligations
GDPR
,
HIPAA
and
data
residency
requirements
translated
into
network
controls
11
12
6 / 7
Security
Automation
,
Scripting
&
DevSecOps
Python
for
Security
Tooling
,
API
clients
,
log
parsers
and
automation
frameworks
for
repetitive
tasks
Shell
&
PowerShell
Scripting
Bash
and
PowerShell
for
hardening
,
remediation
and
bulk
configuration
change
API
Integration
REST
and
GraphQL
consumption
for
SOAR
,
CMDB
and
asset
inventory
tooling
Configuration
as
Code
Ansible
playbooks
,
Terraform
modules
and
golden
image
build
pipelines
CI
/
CD
Pipeline
Security
SAST
,
DAST
and
software
composition
analysis
gates
with
artefact
signing
Secrets
Management
HashiCorp
Vault
and
AWS
Secrets
Manager
with
automated
rotation
workflows
Version
Control
&
Change
Review
Git
workflows
,
peer
review
discipline
and
controlled
change
management
13
7 / 7