Penetration
Testing
—
Technical
Skills
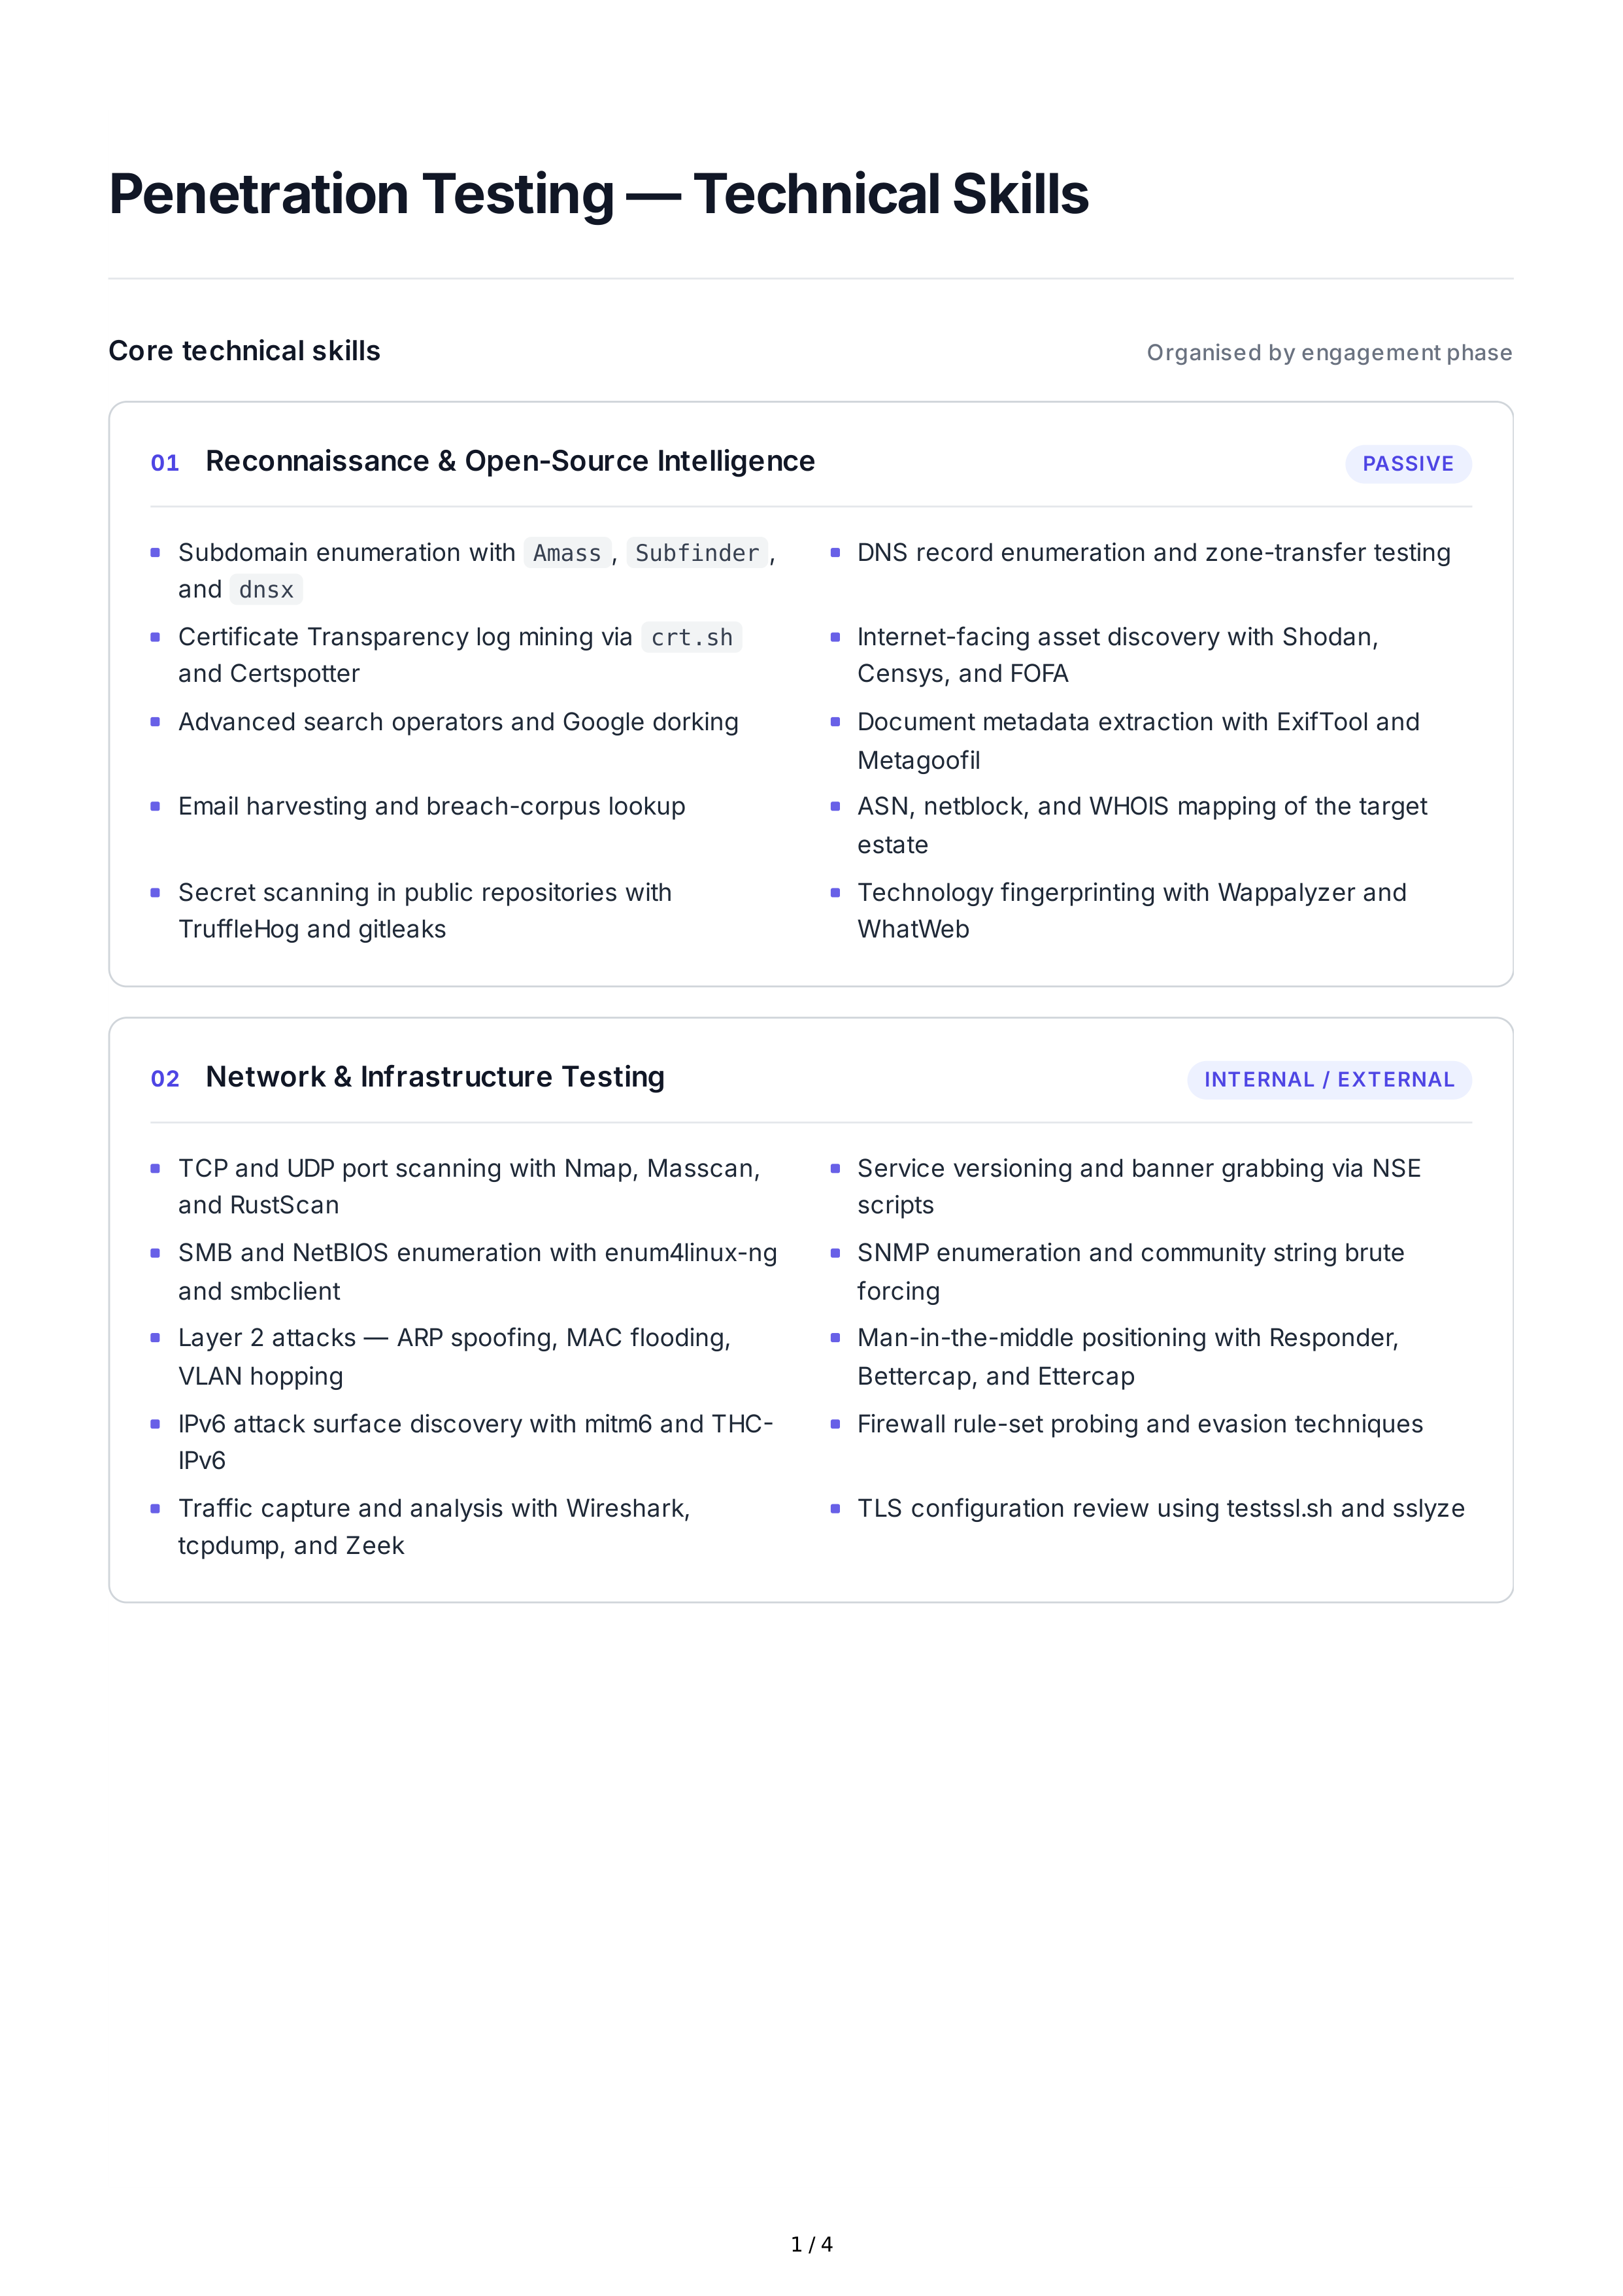
Core
technical
skills
Organised
by
engagement
phase
01
Reconnaissance
&
Open
-
Source
Intelligence
PASSIVE
02
Network
&
Infrastructure
Testing
INTERNAL
/
EXTERNAL
Subdomain
enumeration
with
Amass
,
Subfinder
,
and
dnsx
DNS
record
enumeration
and
zone
-
transfer
testing
Certificate
Transparency
log
mining
via
crt.sh
and
Certspotter
Internet
-
facing
asset
discovery
with
Shodan
,
Censys
,
and
FOFA
Advanced
search
operators
and
Google
dorking
Document
metadata
extraction
with
ExifTool
and
Metagoofil
Email
harvesting
and
breach
-
corpus
lookup
ASN
,
netblock
,
and
WHOIS
mapping
of
the
target
estate
Secret
scanning
in
public
repositories
with
TruffleHog
and
gitleaks
Technology
fingerprinting
with
Wappalyzer
and
WhatWeb
TCP
and
UDP
port
scanning
with
Nmap
,
Masscan
,
and
RustScan
Service
versioning
and
banner
grabbing
via
NSE
scripts
SMB
and
NetBIOS
enumeration
with
enum
4
linux
-
ng
and
smbclient
SNMP
enumeration
and
community
string
brute
forcing
Layer
2
attacks
—
ARP
spoofing
,
MAC
flooding
,
VLAN
hopping
Man
-
in
-
the
-
middle
positioning
with
Responder
,
Bettercap
,
and
Ettercap
IPv
6
attack
surface
discovery
with
mitm
6
and
THC
-
IPv
6
Firewall
rule
-
set
probing
and
evasion
techniques
Traffic
capture
and
analysis
with
Wireshark
,
tcpdump
,
and
Zeek
TLS
configuration
review
using
testssl
.
sh
and
sslyze
1 / 4
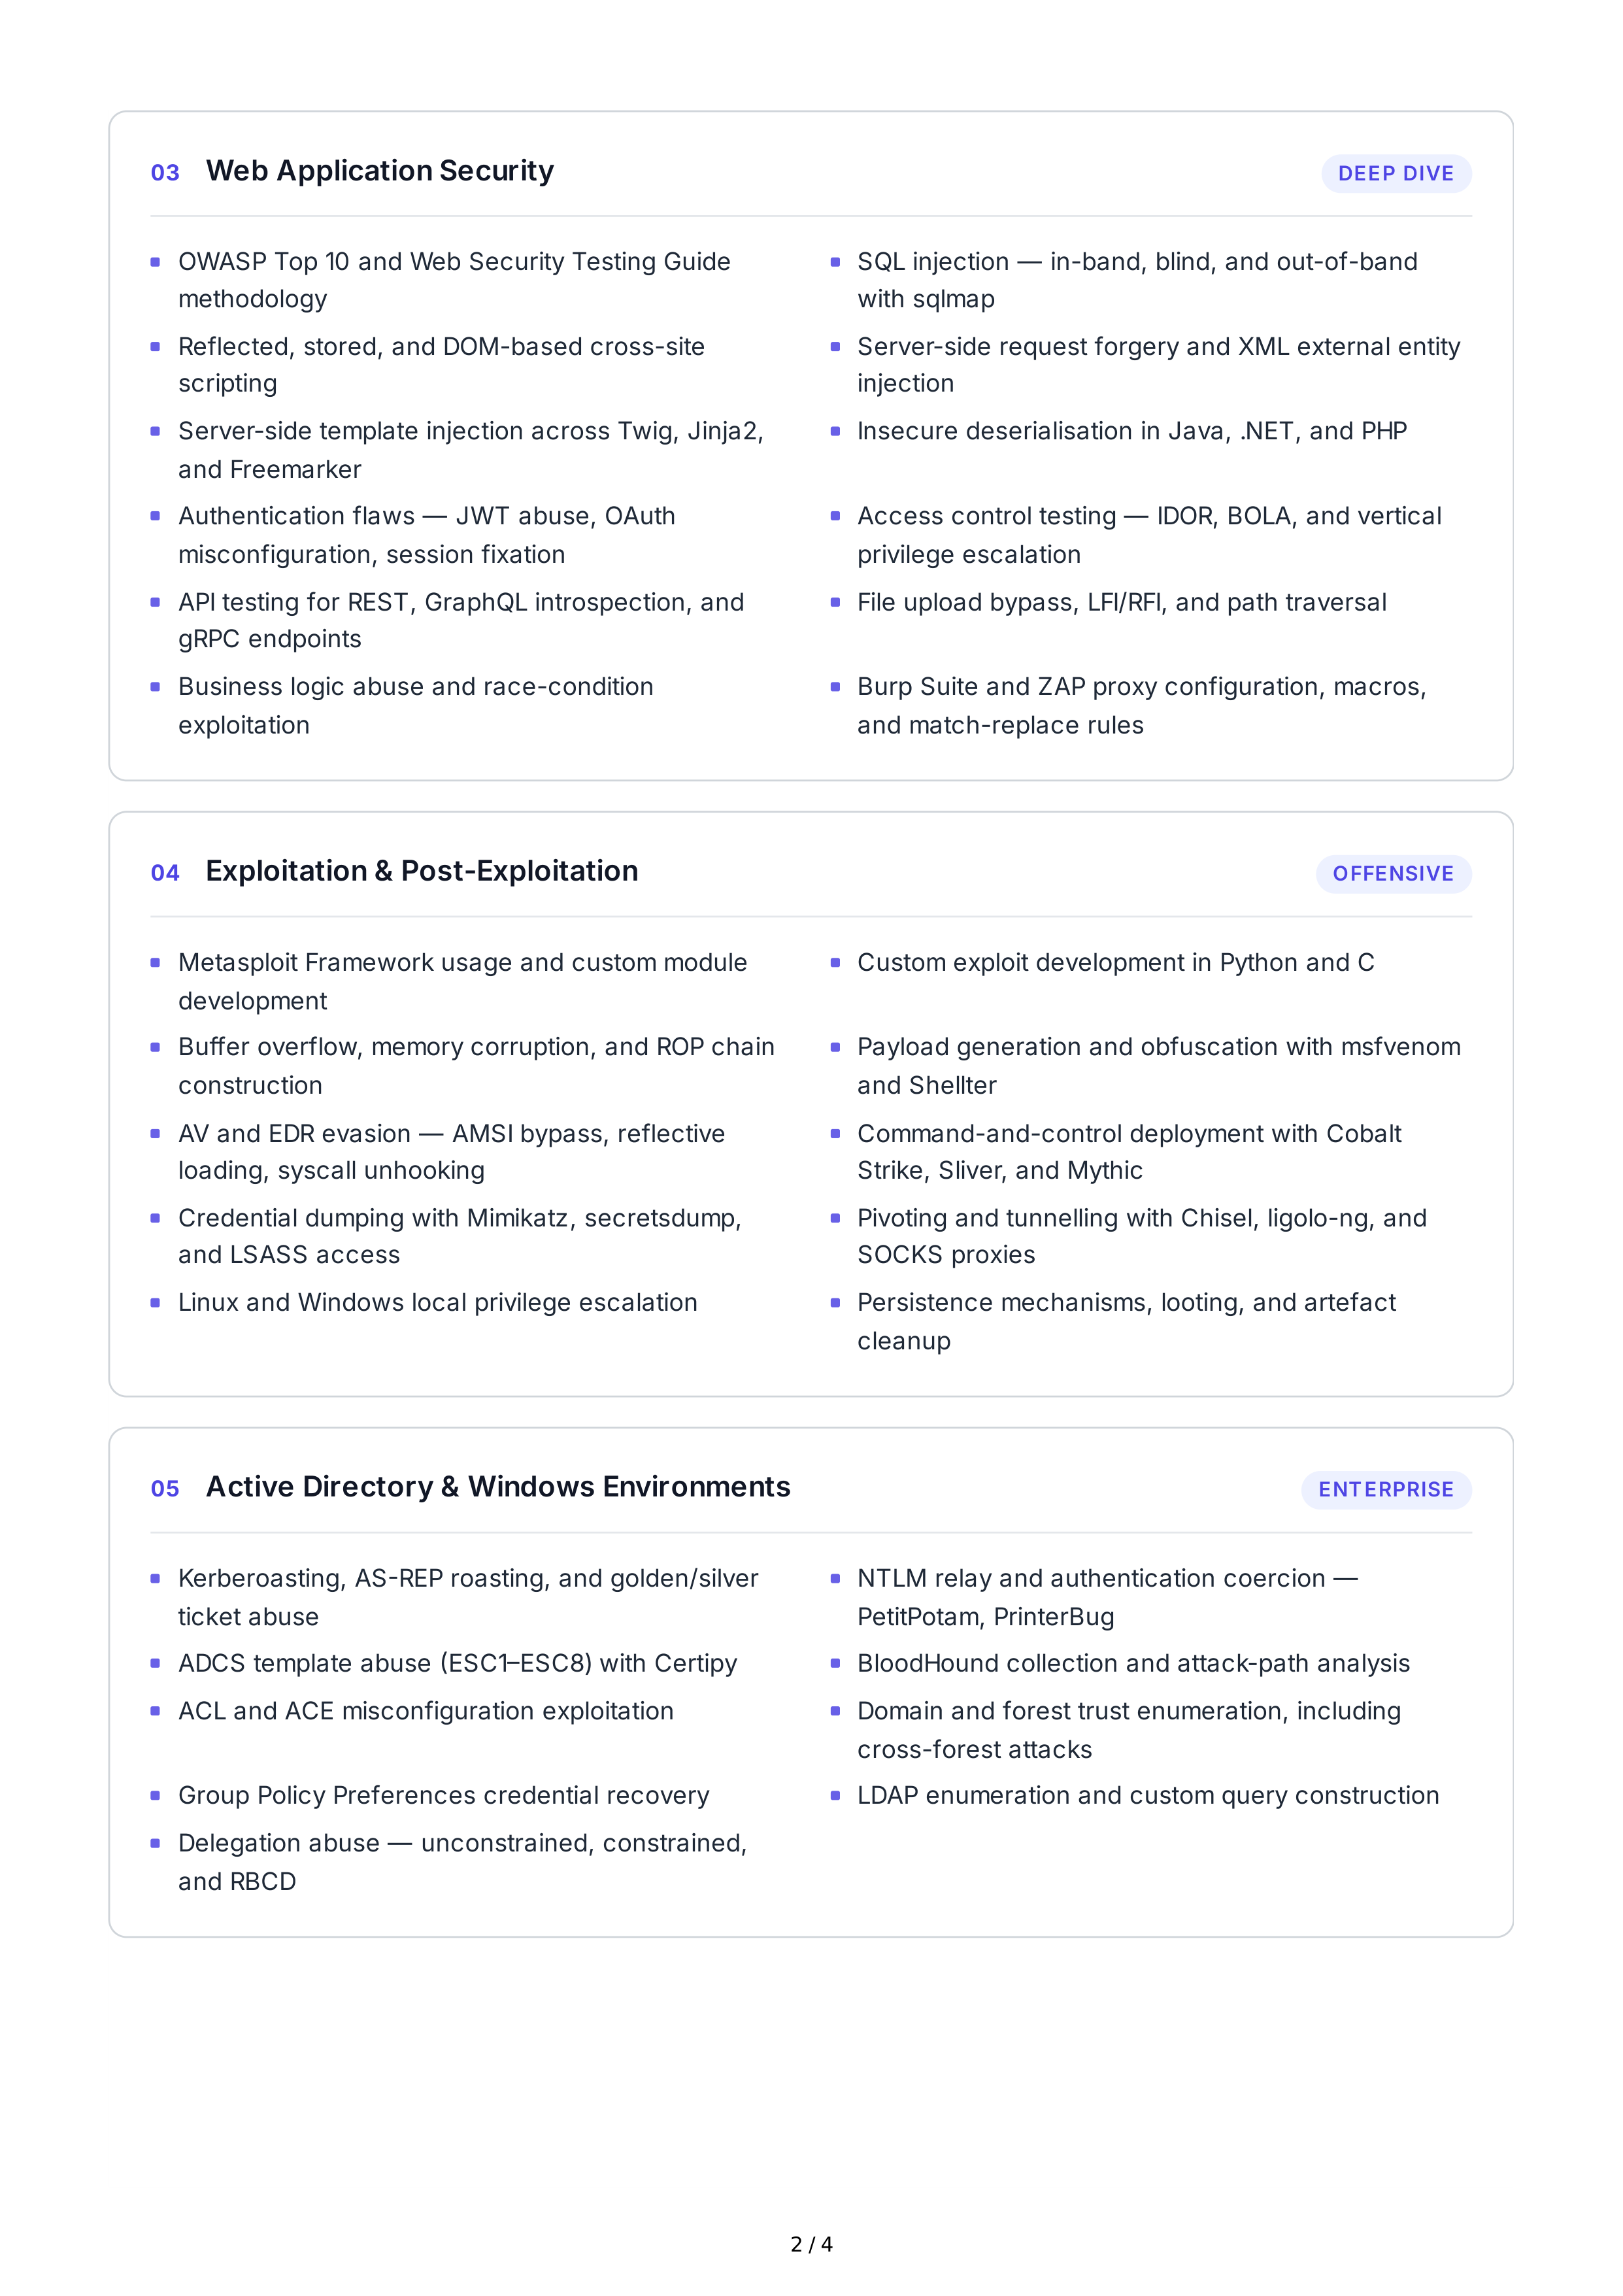
03
Web
Application
Security
DEEP
DIVE
04
Exploitation
&
Post
-
Exploitation
OFFENSIVE
05
Active
Directory
&
Windows
Environments
ENTERPRISE
OWASP
Top
10
and
Web
Security
Testing
Guide
methodology
SQL
injection
—
in
-
band
,
blind
,
and
out
-
of
-
band
with
sqlmap
Reflected
,
stored
,
and
DOM
-
based
cross
-
site
scripting
Server
-
side
request
forgery
and
XML
external
entity
injection
Server
-
side
template
injection
across
Twig
,
Jinja
2,
and
Freemarker
Insecure
deserialisation
in
Java
, .
NET
,
and
PHP
Authentication
flaws
—
JWT
abuse
,
OAuth
misconfiguration
,
session
fixation
Access
control
testing
—
IDOR
,
BOLA
,
and
vertical
privilege
escalation
API
testing
for
REST
,
GraphQL
introspection
,
and
gRPC
endpoints
File
upload
bypass
,
LFI
/
RFI
,
and
path
traversal
Business
logic
abuse
and
race
-
condition
exploitation
Burp
Suite
and
ZAP
proxy
configuration
,
macros
,
and
match
-
replace
rules
Metasploit
Framework
usage
and
custom
module
development
Custom
exploit
development
in
Python
and
C
Buffer
overflow
,
memory
corruption
,
and
ROP
chain
construction
Payload
generation
and
obfuscation
with
msfvenom
and
Shellter
AV
and
EDR
evasion
—
AMSI
bypass
,
reflective
loading
,
syscall
unhooking
Command
-
and
-
control
deployment
with
Cobalt
Strike
,
Sliver
,
and
Mythic
Credential
dumping
with
Mimikatz
,
secretsdump
,
and
LSASS
access
Pivoting
and
tunnelling
with
Chisel
,
ligolo
-
ng
,
and
SOCKS
proxies
Linux
and
Windows
local
privilege
escalation
Persistence
mechanisms
,
looting
,
and
artefact
cleanup
Kerberoasting
,
AS
-
REP
roasting
,
and
golden
/
silver
ticket
abuse
NTLM
relay
and
authentication
coercion
—
PetitPotam
,
PrinterBug
ADCS
template
abuse
(
ESC
1–
ESC
8)
with
Certipy
BloodHound
collection
and
attack
-
path
analysis
ACL
and
ACE
misconfiguration
exploitation
Domain
and
forest
trust
enumeration
,
including
cross
-
forest
attacks
Group
Policy
Preferences
credential
recovery
LDAP
enumeration
and
custom
query
construction
Delegation
abuse
—
unconstrained
,
constrained
,
and
RBCD
2 / 4
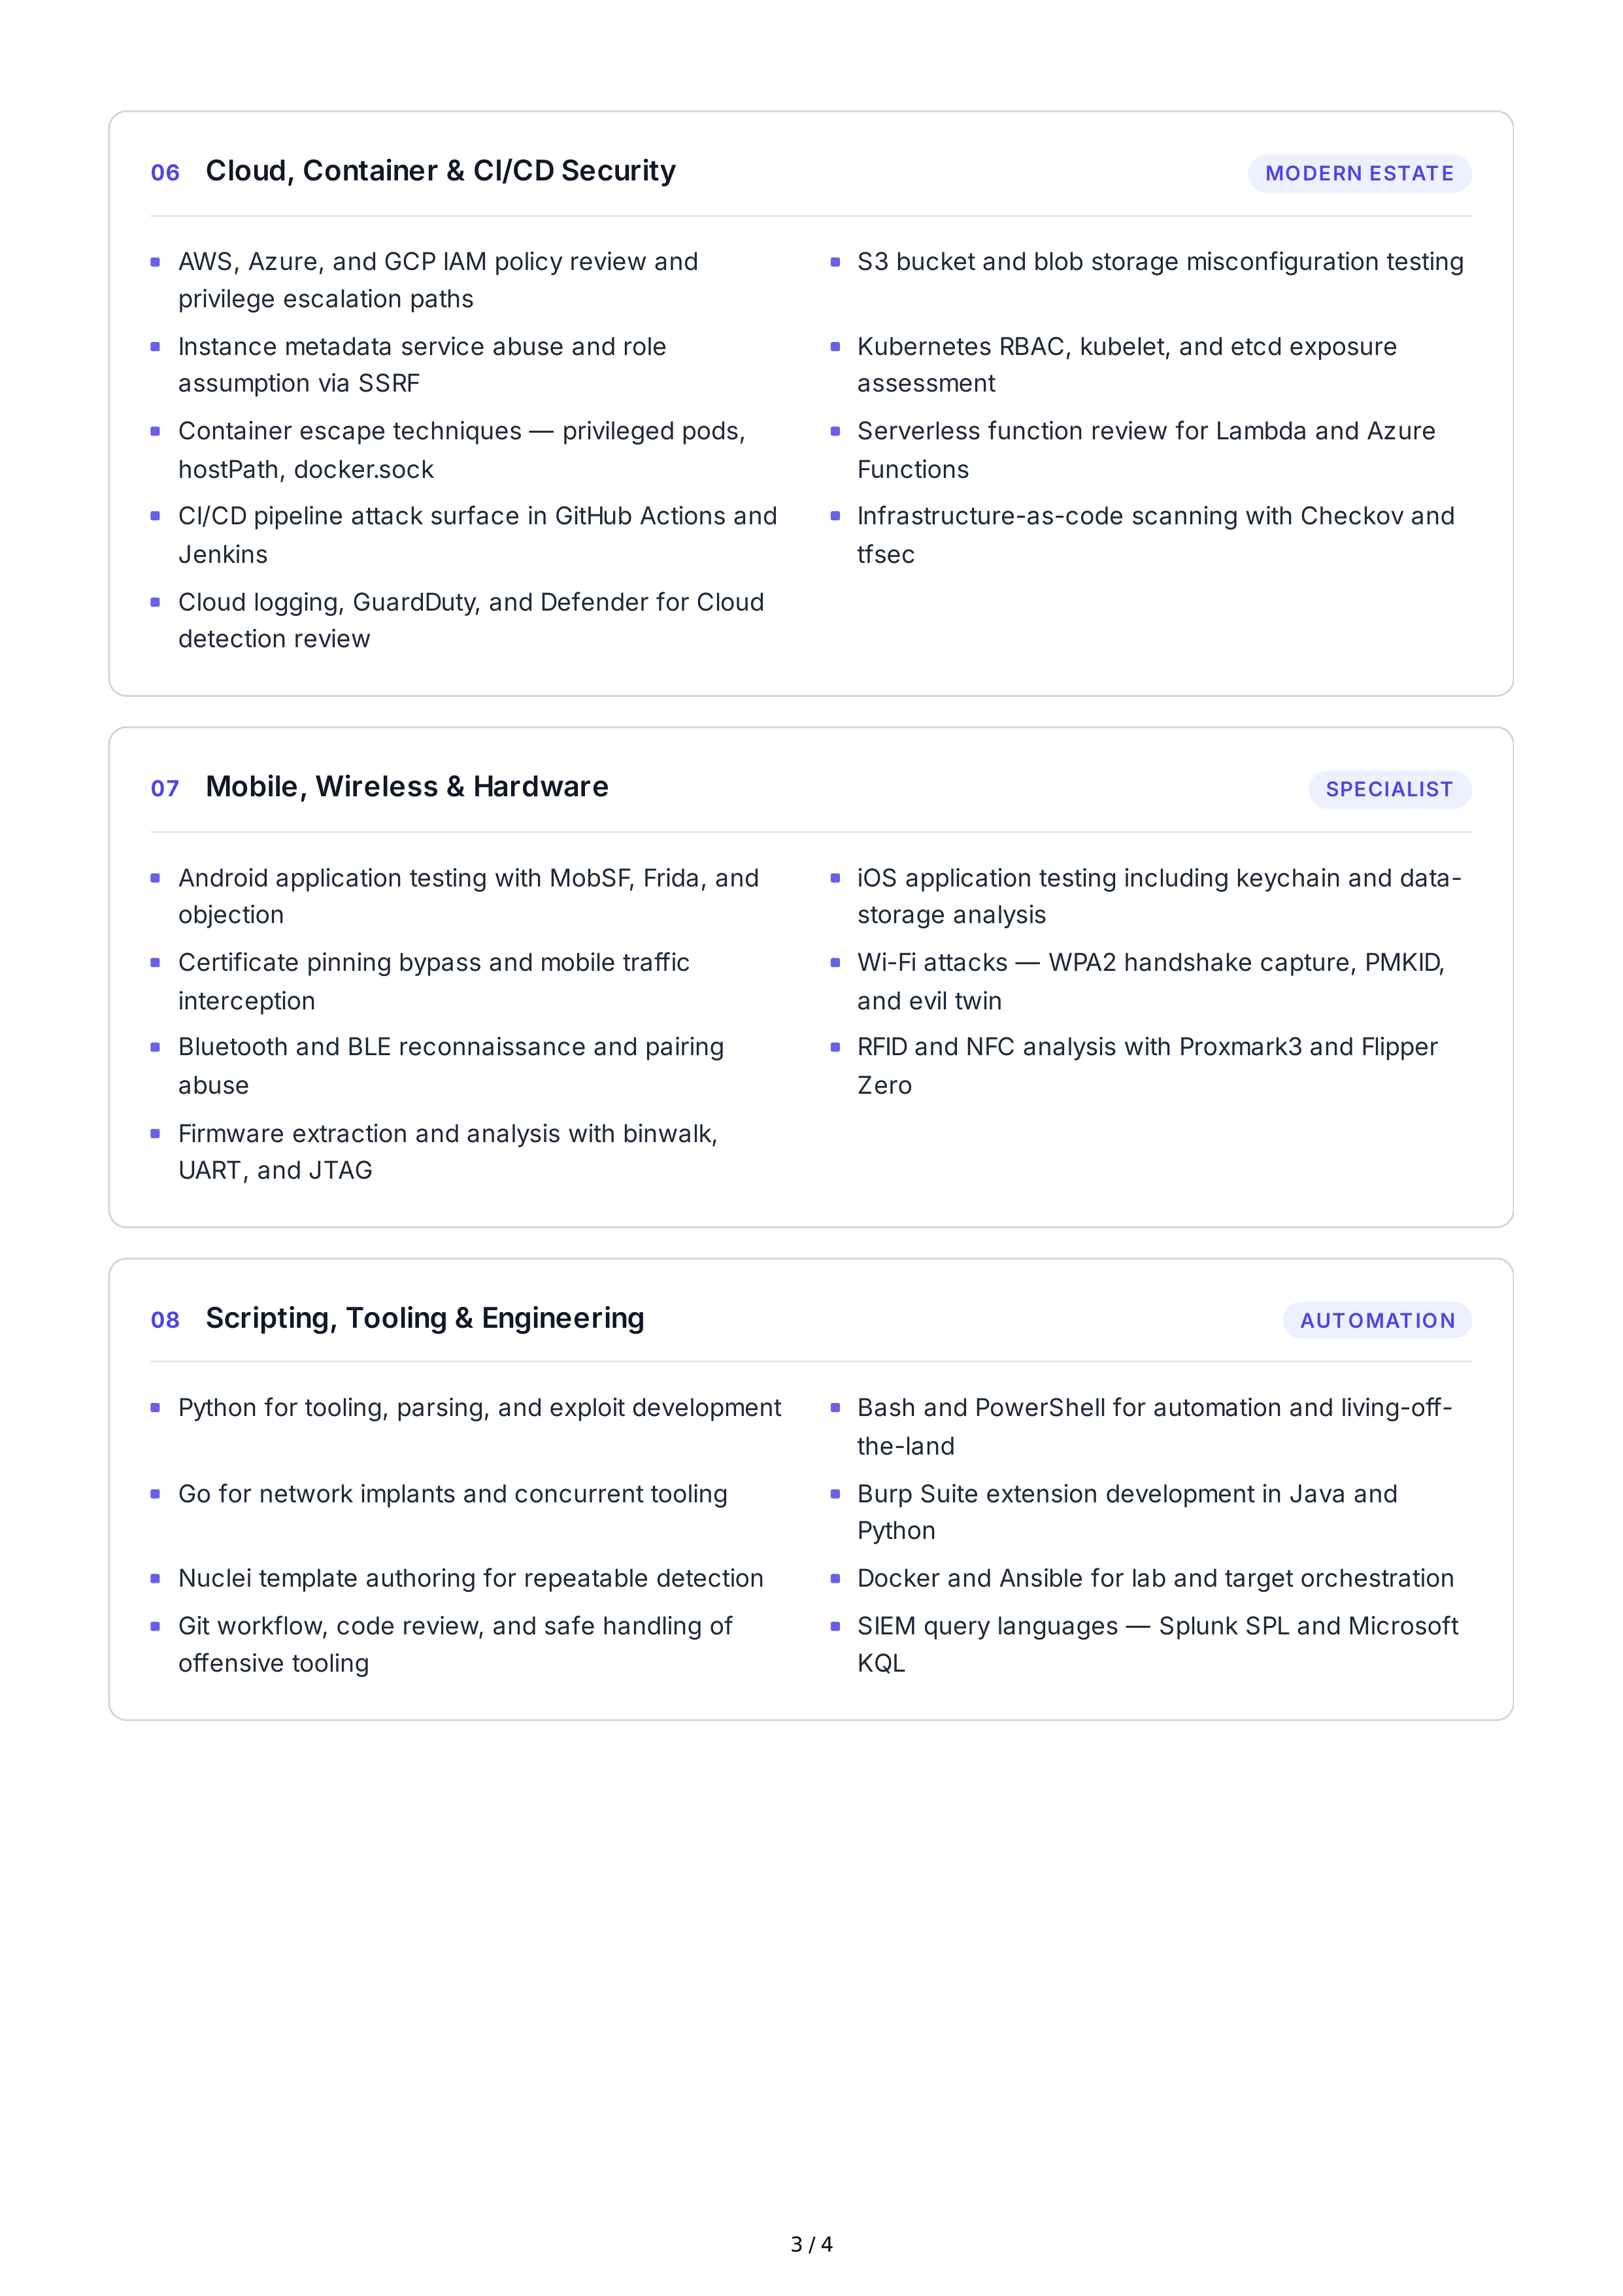
06
Cloud
,
Container
&
CI
/
CD
Security
MODERN
ESTATE
07
Mobile
,
Wireless
&
Hardware
SPECIALIST
08
Scripting
,
Tooling
&
Engineering
AUTOMATION
AWS
,
Azure
,
and
GCP
IAM
policy
review
and
privilege
escalation
paths
S
3
bucket
and
blob
storage
misconfiguration
testing
Instance
metadata
service
abuse
and
role
assumption
via
SSRF
Kubernetes
RBAC
,
kubelet
,
and
etcd
exposure
assessment
Container
escape
techniques
—
privileged
pods
,
hostPath
,
docker
.
sock
Serverless
function
review
for
Lambda
and
Azure
Functions
CI
/
CD
pipeline
attack
surface
in
GitHub
Actions
and
Jenkins
Infrastructure
-
as
-
code
scanning
with
Checkov
and
tfsec
Cloud
logging
,
GuardDuty
,
and
Defender
for
Cloud
detection
review
Android
application
testing
with
MobSF
,
Frida
,
and
objection
iOS
application
testing
including
keychain
and
data
-
storage
analysis
Certificate
pinning
bypass
and
mobile
traffic
interception
Wi
-
Fi
attacks
—
WPA
2
handshake
capture
,
PMKID
,
and
evil
twin
Bluetooth
and
BLE
reconnaissance
and
pairing
abuse
RFID
and
NFC
analysis
with
Proxmark
3
and
Flipper
Zero
Firmware
extraction
and
analysis
with
binwalk
,
UART
,
and
JTAG
Python
for
tooling
,
parsing
,
and
exploit
development
Bash
and
PowerShell
for
automation
and
living
-
off
-
the
-
land
Go
for
network
implants
and
concurrent
tooling
Burp
Suite
extension
development
in
Java
and
Python
Nuclei
template
authoring
for
repeatable
detection
Docker
and
Ansible
for
lab
and
target
orchestration
Git
workflow
,
code
review
,
and
safe
handling
of
offensive
tooling
SIEM
query
languages
—
Splunk
SPL
and
Microsoft
KQL
3 / 4
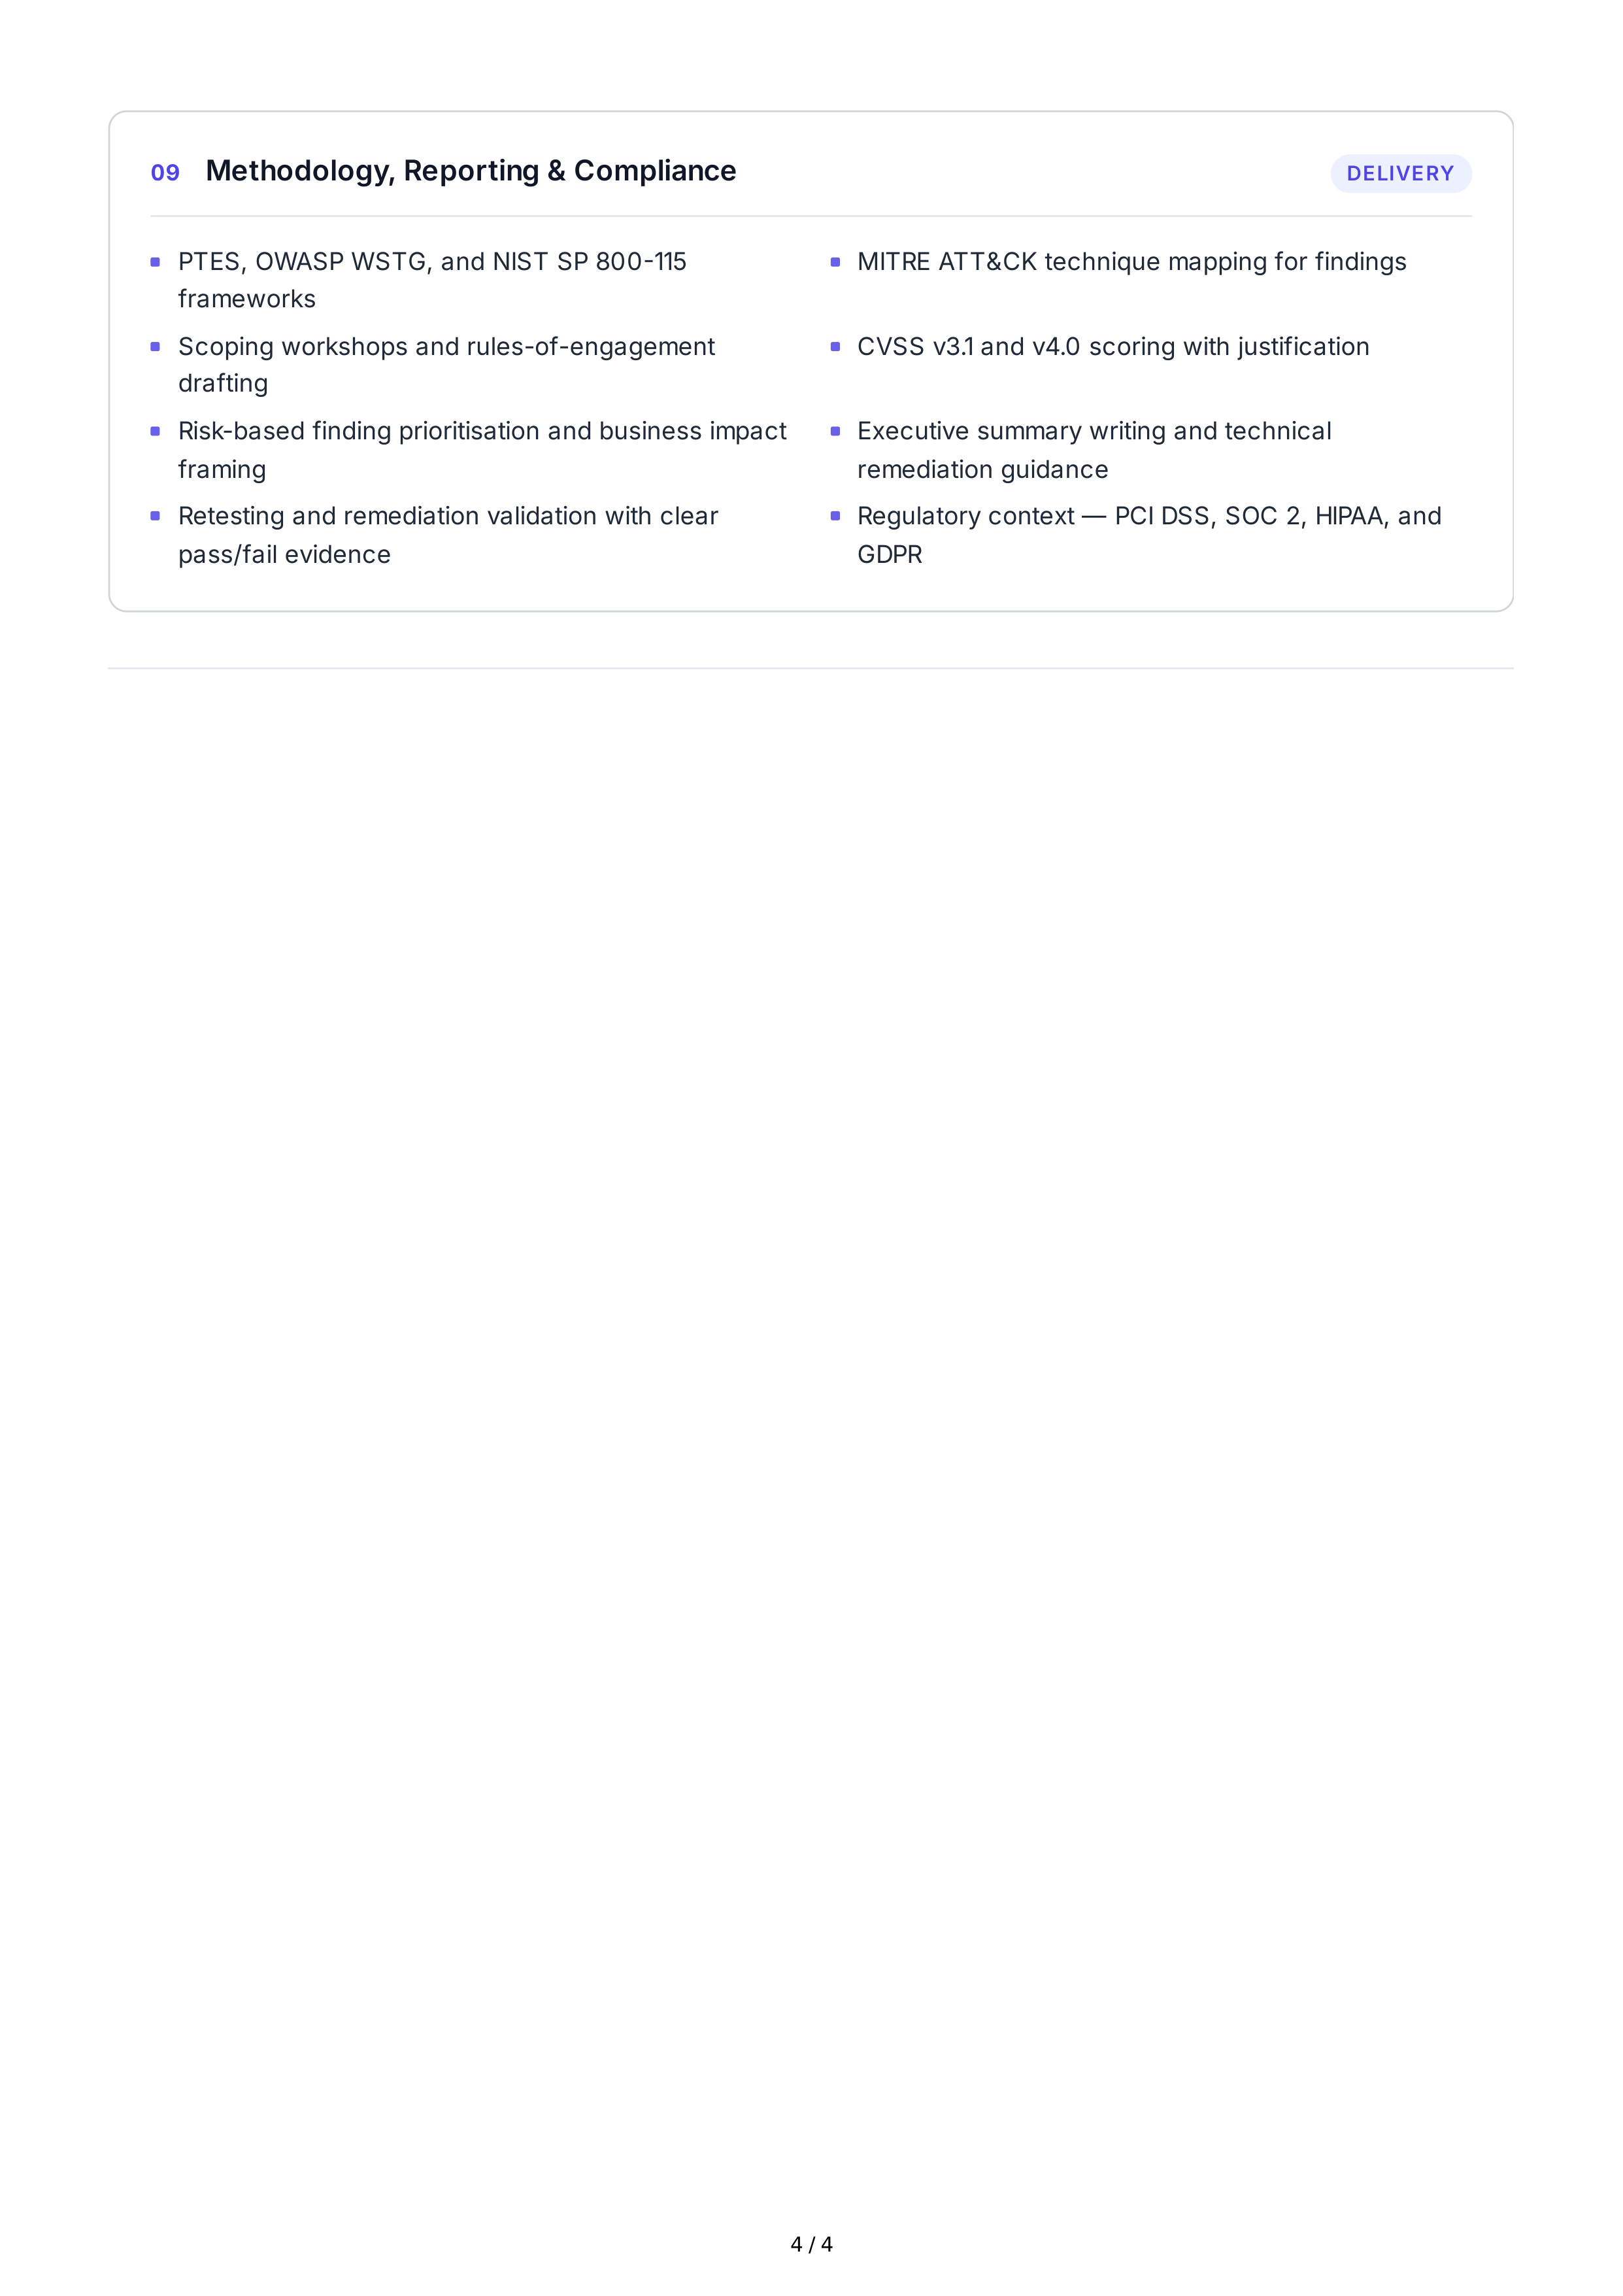
09
Methodology
,
Reporting
&
Compliance
DELIVERY
PTES
,
OWASP
WSTG
,
and
NIST
SP
800-115
frameworks
MITRE
ATT
&
CK
technique
mapping
for
findings
Scoping
workshops
and
rules
-
of
-
engagement
drafting
CVSS
v
3.1
and
v
4.0
scoring
with
justification
Risk
-
based
finding
prioritisation
and
business
impact
framing
Executive
summary
writing
and
technical
remediation
guidance
Retesting
and
remediation
validation
with
clear
pass
/
fail
evidence
Regulatory
context
—
PCI
DSS
,
SOC
2,
HIPAA
,
and
GDPR
4 / 4