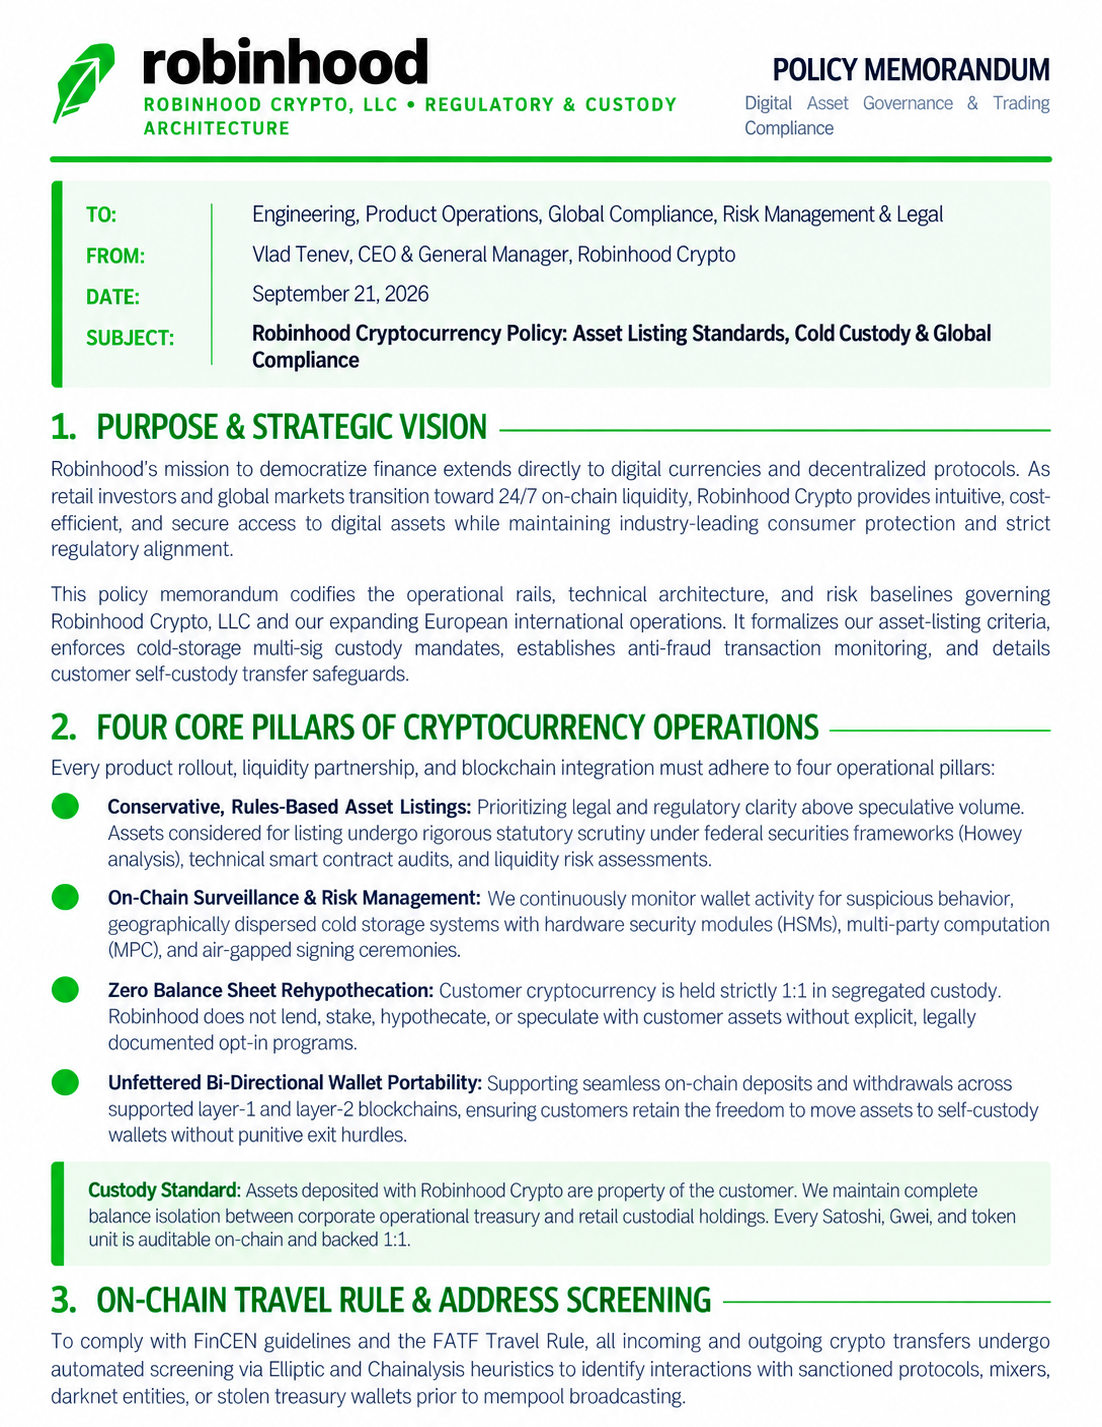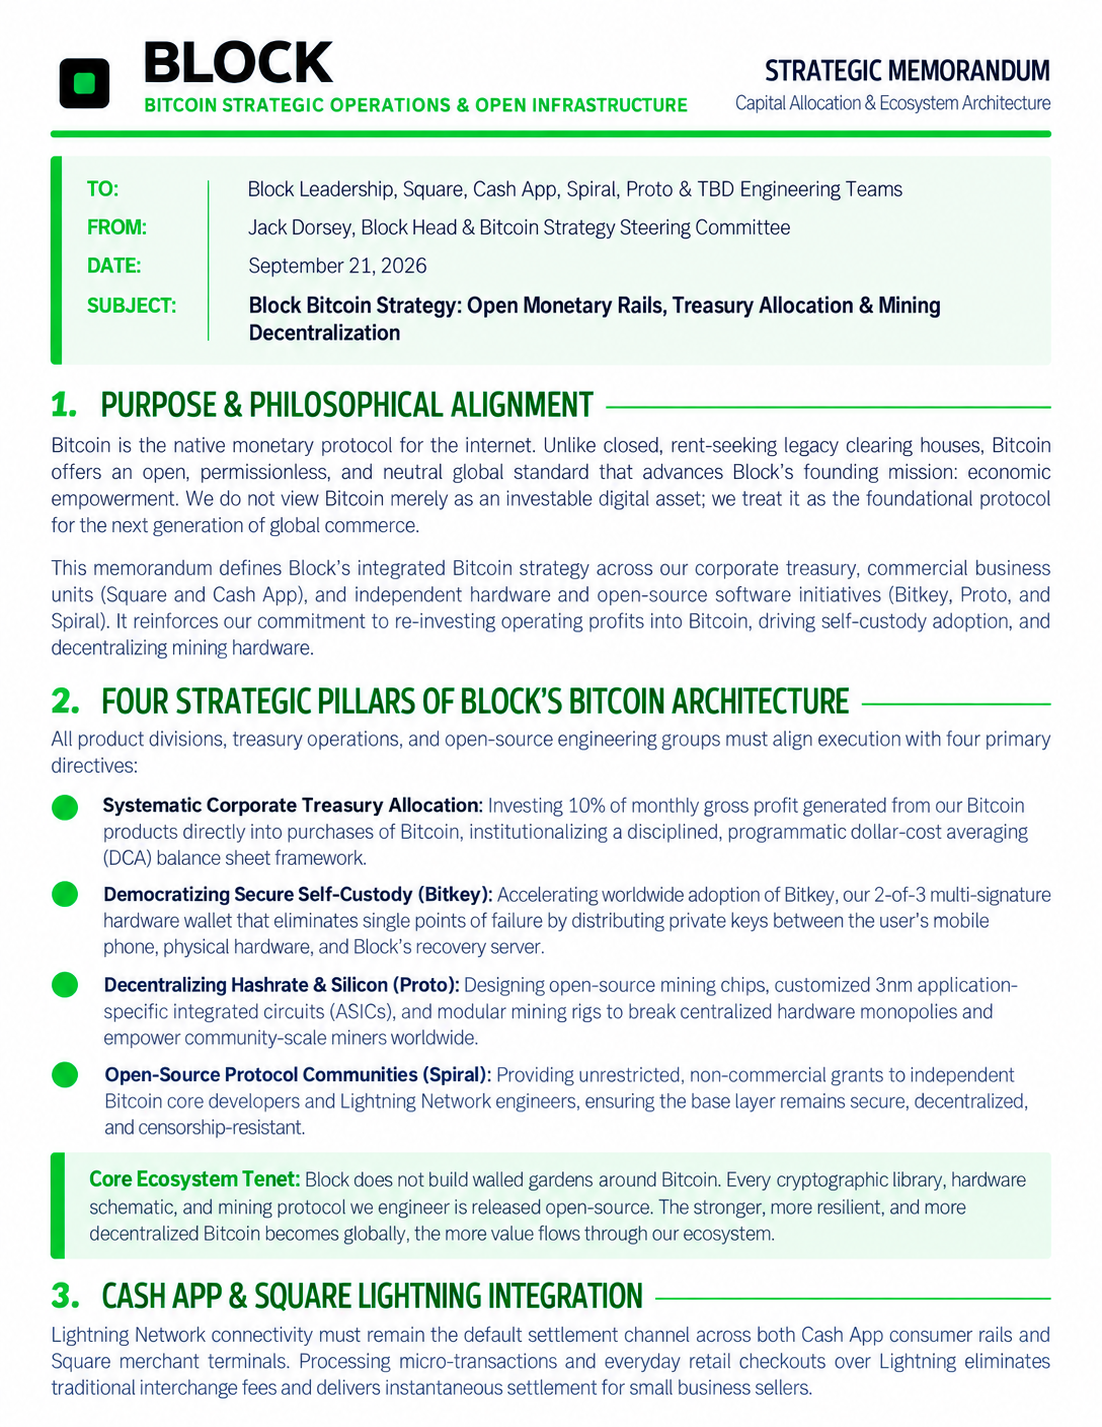
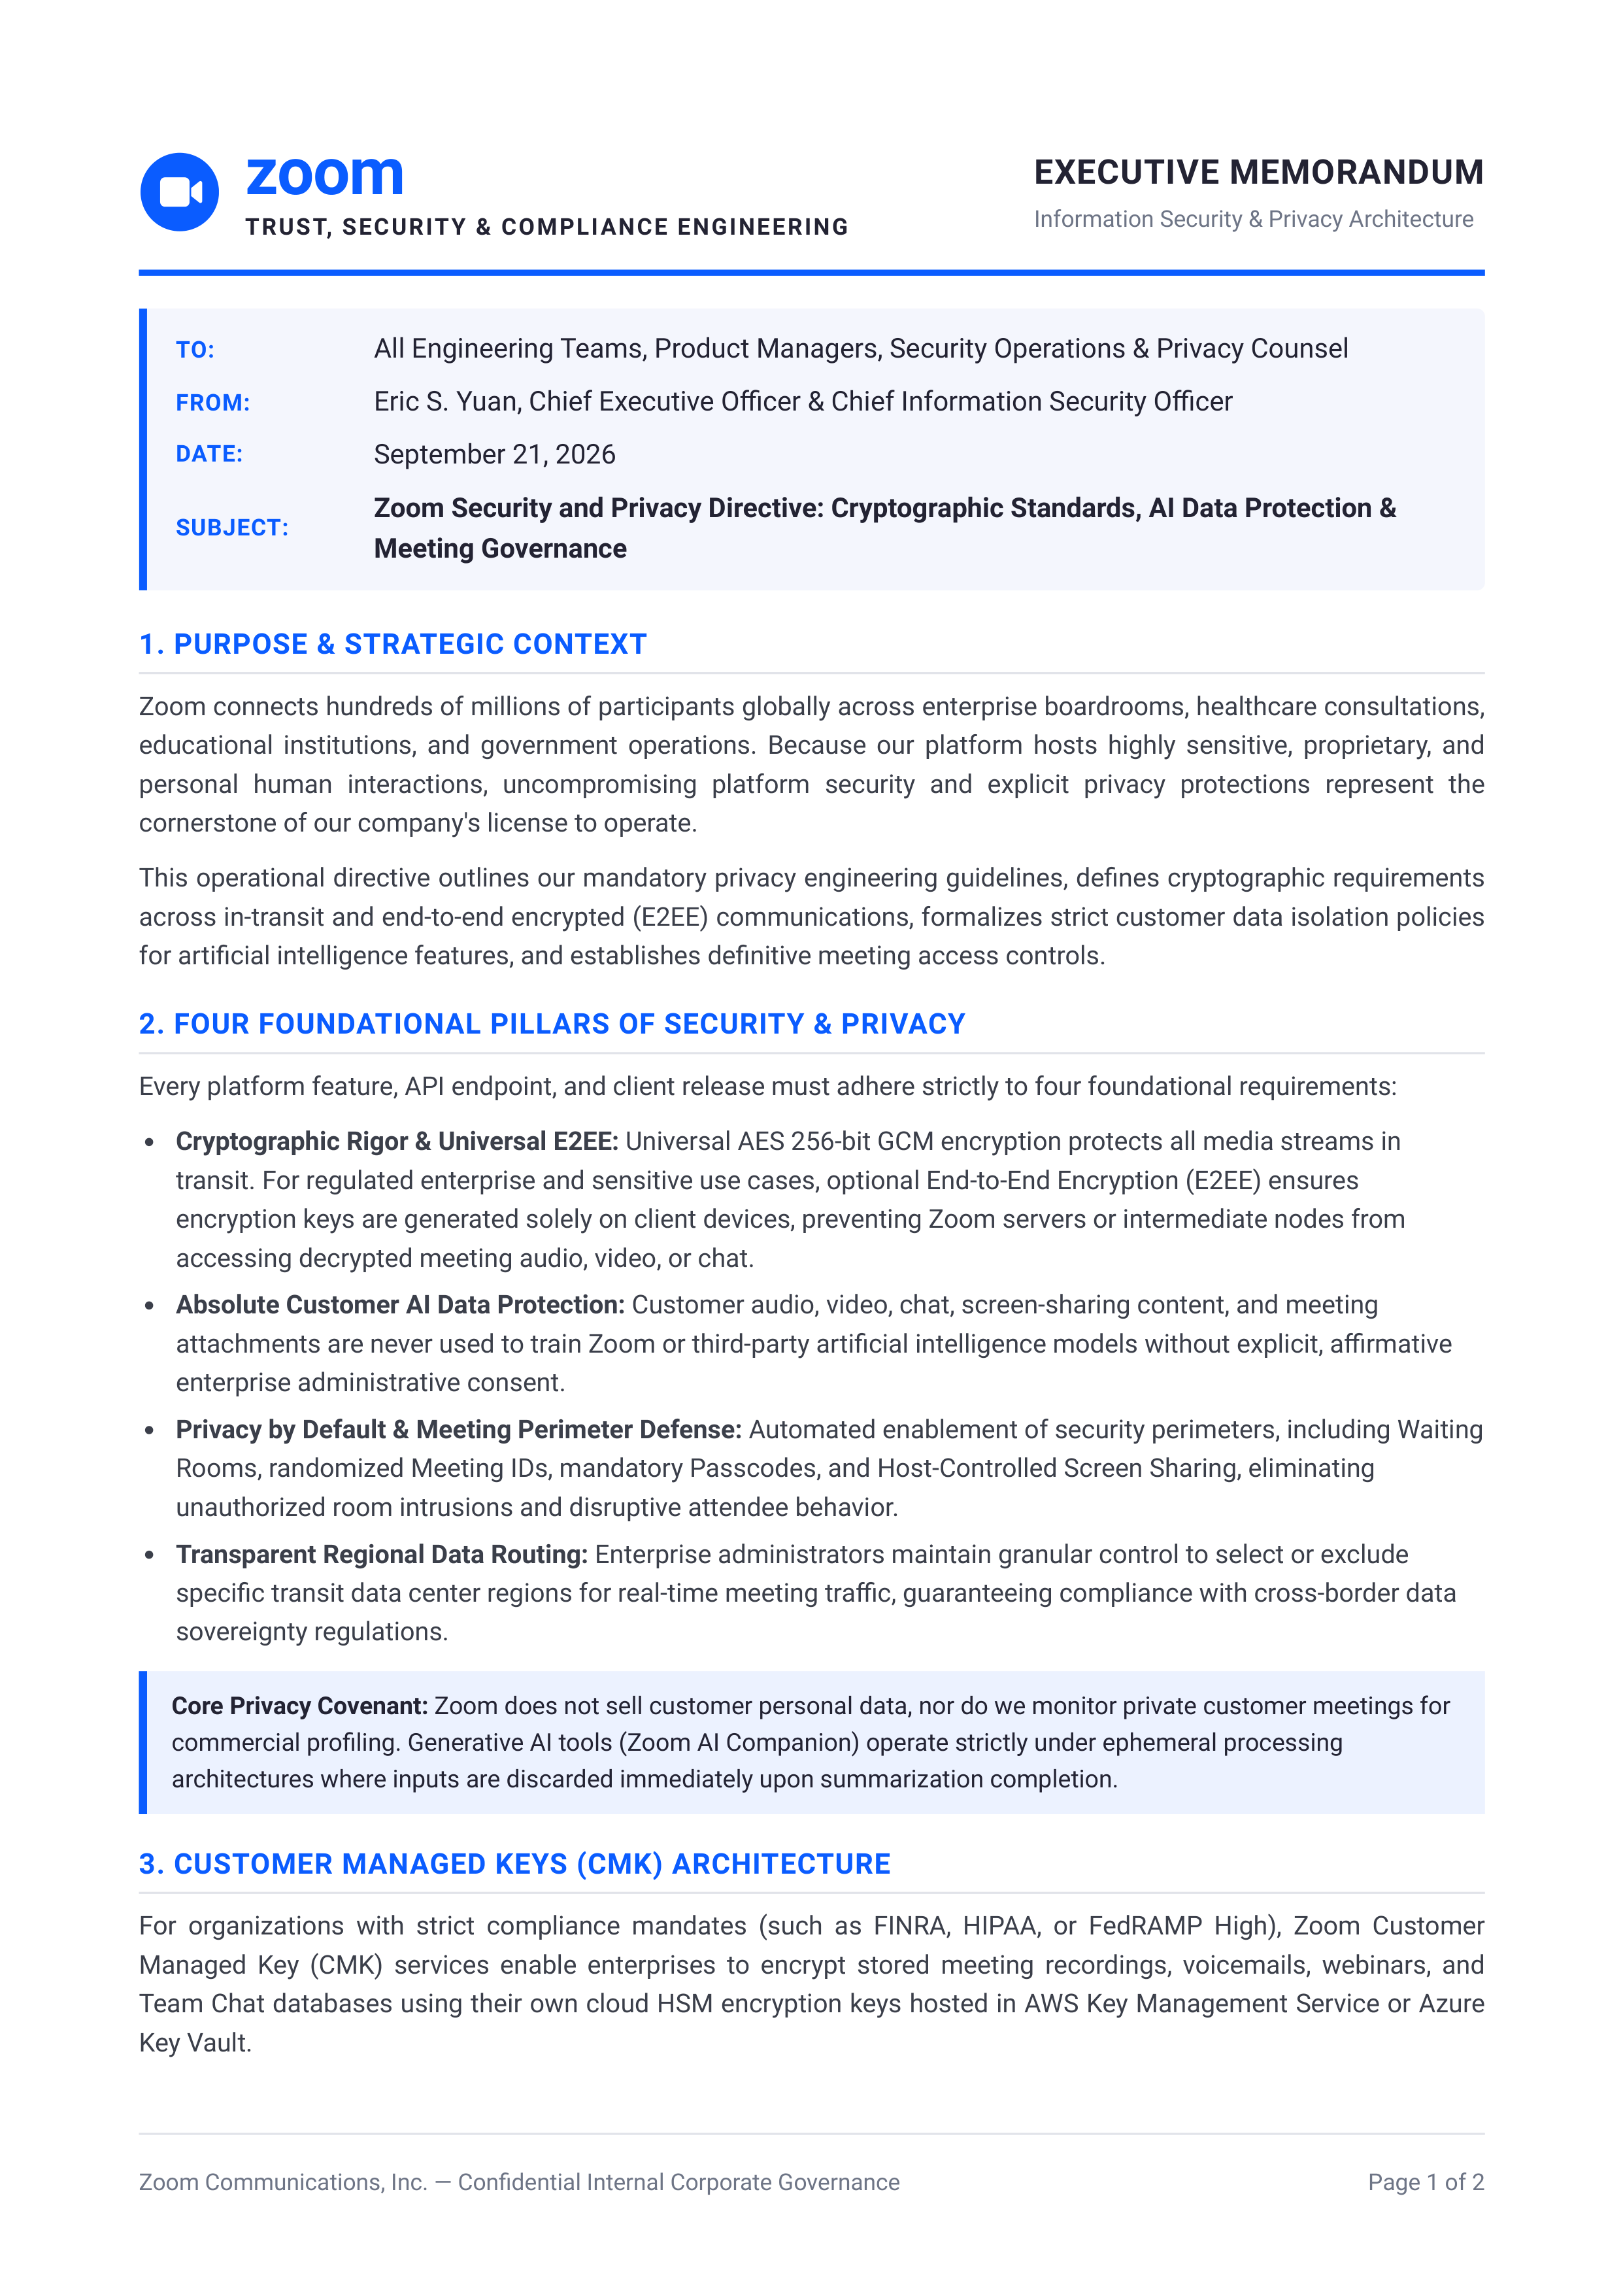
zoom
TRUST, SECURITY & COMPLIANCE ENGINEERING
EXECUTIVE MEMORANDUM
Information Security & Privacy Architecture
TO:
All Engineering Teams, Product Managers, Security Operations & Privacy Counsel
FROM:
Eric S. Yuan, Chief Executive O
ffi
cer & Chief Information Security O
ffi
cer
DATE:
September 21, 2026
SUBJECT:
Zoom Security and Privacy Directive: Cryptographic Standards, AI Data Protection &
Meeting Governance
1. PURPOSE & STRATEGIC CONTEXT
Zoom connects hundreds of millions of participants globally across enterprise boardrooms, healthcare consultations,
educational institutions, and government operations. Because our platform hosts highly sensitive, proprietary, and
personal human interactions, uncompromising platform security and explicit privacy protections represent the
cornerstone of our company's license to operate.
This operational directive outlines our mandatory privacy engineering guidelines, de
fi
nes cryptographic requirements
across in-transit and end-to-end encrypted (E2EE) communications, formalizes strict customer data isolation policies
for arti
fi
cial intelligence features, and establishes de
fi
nitive meeting access controls.
2. FOUR FOUNDATIONAL PILLARS OF SECURITY & PRIVACY
Every platform feature, API endpoint, and client release must adhere strictly to four foundational requirements:
Cryptographic Rigor & Universal E2EE:
Universal AES 256-bit GCM encryption protects all media streams in
transit. For regulated enterprise and sensitive use cases, optional End-to-End Encryption (E2EE) ensures
encryption keys are generated solely on client devices, preventing Zoom servers or intermediate nodes from
accessing decrypted meeting audio, video, or chat.
Absolute Customer AI Data Protection:
Customer audio, video, chat, screen-sharing content, and meeting
attachments are never used to train Zoom or third-party arti
fi
cial intelligence models without explicit, a
ffi
rmative
enterprise administrative consent.
Privacy by Default & Meeting Perimeter Defense:
Automated enablement of security perimeters, including Waiting
Rooms, randomized Meeting IDs, mandatory Passcodes, and Host-Controlled Screen Sharing, eliminating
unauthorized room intrusions and disruptive attendee behavior.
Transparent Regional Data Routing:
Enterprise administrators maintain granular control to select or exclude
speci
fi
c transit data center regions for real-time meeting tra
ffi
c, guaranteeing compliance with cross-border data
sovereignty regulations.
Core Privacy Covenant:
Zoom does not sell customer personal data, nor do we monitor private customer meetings for
commercial pro
fi
ling. Generative AI tools (Zoom AI Companion) operate strictly under ephemeral processing
architectures where inputs are discarded immediately upon summarization completion.
3. CUSTOMER MANAGED KEYS (CMK) ARCHITECTURE
For organizations with strict compliance mandates (such as FINRA, HIPAA, or FedRAMP High), Zoom Customer
Managed Key (CMK) services enable enterprises to encrypt stored meeting recordings, voicemails, webinars, and
Team Chat databases using their own cloud HSM encryption keys hosted in AWS Key Management Service or Azure
Key Vault.
Zoom Communications, Inc.
—
Con
fi
dential Internal Corporate Governance
Page 1 of 2
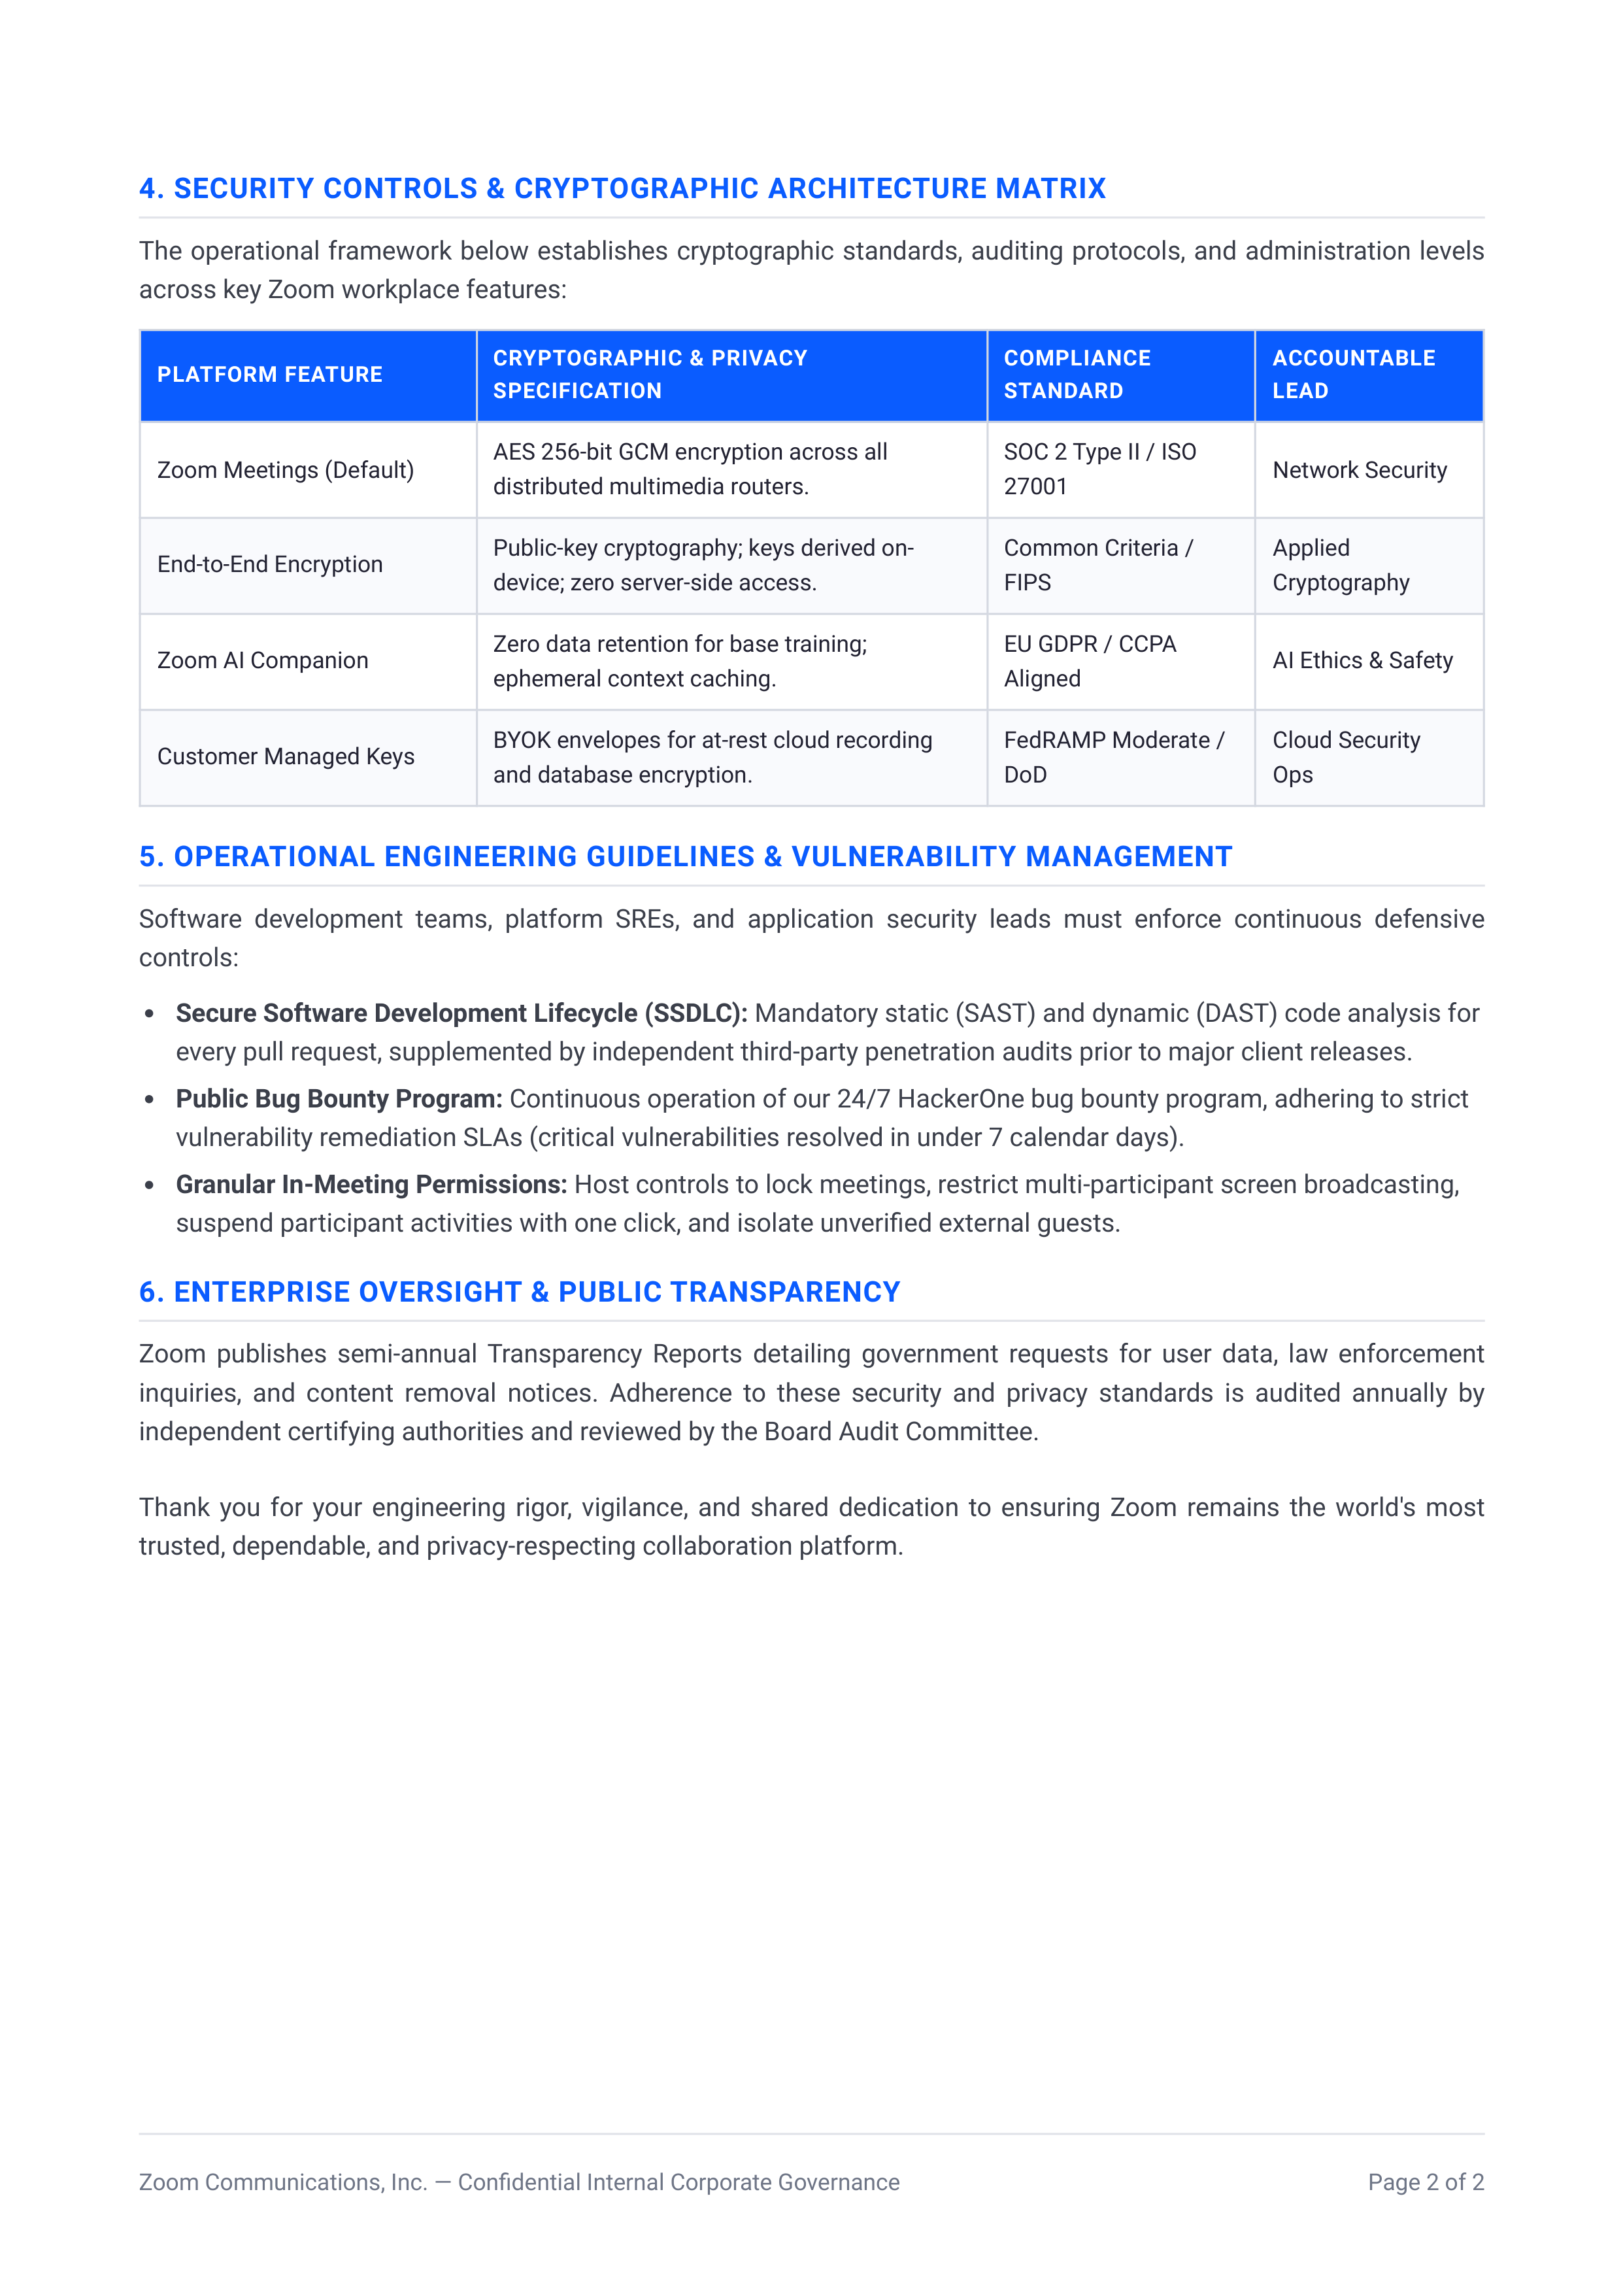
4. SECURITY CONTROLS & CRYPTOGRAPHIC ARCHITECTURE MATRIX
The operational framework below establishes cryptographic standards, auditing protocols, and administration levels
across key Zoom workplace features:
PLATFORM FEATURE
CRYPTOGRAPHIC & PRIVACY
SPECIFICATION
COMPLIANCE
STANDARD
ACCOUNTABLE
LEAD
Zoom Meetings (Default)
AES 256-bit GCM encryption across all
distributed multimedia routers.
SOC 2 Type II / ISO
27001
Network Security
End-to-End Encryption
Public-key cryptography; keys derived on-
device; zero server-side access.
Common Criteria /
FIPS
Applied
Cryptography
Zoom AI Companion
Zero data retention for base training;
ephemeral context caching.
EU GDPR / CCPA
Aligned
AI Ethics & Safety
Customer Managed Keys
BYOK envelopes for at-rest cloud recording
and database encryption.
FedRAMP Moderate /
DoD
Cloud Security
Ops
5. OPERATIONAL ENGINEERING GUIDELINES & VULNERABILITY MANAGEMENT
Software development teams, platform SREs, and application security leads must enforce continuous defensive
controls:
Secure Software Development Lifecycle (SSDLC):
Mandatory static (SAST) and dynamic (DAST) code analysis for
every pull request, supplemented by independent third-party penetration audits prior to major client releases.
Public Bug Bounty Program:
Continuous operation of our 24/7 HackerOne bug bounty program, adhering to strict
vulnerability remediation SLAs (critical vulnerabilities resolved in under 7 calendar days).
Granular In-Meeting Permissions:
Host controls to lock meetings, restrict multi-participant screen broadcasting,
suspend participant activities with one click, and isolate unveri
fi
ed external guests.
6. ENTERPRISE OVERSIGHT & PUBLIC TRANSPARENCY
Zoom publishes semi-annual Transparency Reports detailing government requests for user data, law enforcement
inquiries, and content removal notices. Adherence to these security and privacy standards is audited annually by
independent certifying authorities and reviewed by the Board Audit Committee.
Thank you for your engineering rigor, vigilance, and shared dedication to ensuring Zoom remains the world's most
trusted, dependable, and privacy-respecting collaboration platform.
Zoom Communications, Inc.
—
Con
fi
dential Internal Corporate Governance
Page 2 of 2